admin
In what is being characterized as the most significant financial breach in the history of decentralized finance, hackers affiliated with the North Korean regime have been identified as the primary suspects in a massive cyberattack against Binance, the world’s largest cryptocurrency exchange by volume. Initial forensic reports indicate that the attackers successfully exfiltrated approximately $6.3 billion in digital assets from the company’s hot wallets, sending shockwaves through global financial markets and raising urgent questions regarding the security infrastructure of major trading platforms. While the scale of the theft is staggering, security researchers and blockchain intelligence firms report that roughly $3 billion of the stolen funds has been successfully frozen as it moved across various liquidity protocols and interconnected blockchains. This intervention, facilitated by a coalition of industry partners and law enforcement agencies, has mitigated some of the immediate damage, yet the incident remains an active crisis with the final tally of lost assets still subject to fluctuation.
The breach represents a watershed moment for the cryptocurrency industry, surpassing all previous exploits in terms of total value. Despite the severity of the situation, the resolution of the incident remains ongoing, and Binance has yet to confirm that the threat has been fully neutralized. The company’s internal investigation, shared partially via public communications, suggests that the point of entry was not a systemic vulnerability in the blockchain itself, but rather a targeted compromise of a single employee’s hardware. According to Binance, the attackers gained access to the corporate network by compromising a laptop belonging to a Binance engineer. This unauthorized access allowed the threat actors to penetrate a service container—a virtualized environment used to run specific applications—and subsequently submit a series of unauthorized withdrawal transactions that bypassed standard security checkpoints.
The Mechanics of the Breach and Initial Discovery
The speed and precision of the attack have left many cybersecurity experts stunned. Data provided by TRM Labs, a leading blockchain intelligence firm, suggests that the actual exfiltration of the $6.3 billion took place in a window of approximately 20 minutes. This level of automation indicates a highly sophisticated operation, likely involving pre-written scripts designed to drain wallets as soon as the service container was compromised. By targeting a service container rather than the exchange’s core private keys, the hackers were able to manipulate the system’s internal logic to authorize transfers. Binance has emphasized that there is currently no evidence suggesting that its master private keys—the cryptographic codes that provide total control over the exchange’s reserves—were compromised. Had the private keys been stolen, the hackers would have had near-unfettered access to all user funds, potentially leading to the total collapse of the platform.
In response to the detection of unusual activity, Binance took the drastic step of suspending all deposits and withdrawals. This move, while necessary to prevent further loss, has locked millions of users out of their assets, leading to widespread anxiety regarding the solvency of the exchange. While Binance leadership has issued statements assuring the public that "user funds are safe," the company has not yet provided the cryptographic "proof of reserves" necessary to substantiate this claim in the wake of such a massive loss. The exchange has stated that an updated audit of its holdings will be published once the remediation and forensic processes are complete.
Chronology of a Global Financial Crisis
The timeline of the heist suggests a meticulously planned operation that likely began months before the actual theft occurred. While the primary exploit was executed rapidly, the initial compromise of the engineer’s laptop is believed to be the result of a long-term social engineering or supply chain campaign.
- Phase 1: Initial Infiltration: Though the exact date is unknown, security researchers believe the engineer’s device was infected with malware through a compromised open-source library or a sophisticated phishing attempt.
- Thursday, October 29: Unusual withdrawal patterns are detected on the Binance Smart Chain and other integrated networks. Binance quietly begins pausing withdrawals on specific bridges to contain the flow of assets.
- Thursday Evening: News of the suspension breaks globally. TechCrunch reports that Binance has halted operations, leading to a sharp decline in the price of Binance Coin (BNB) and other major cryptocurrencies.
- Friday, October 30: Binance issues a formal statement via X (formerly Twitter) acknowledging the breach and attributing it to a compromised employee device.
- Friday Afternoon: Blockchain forensics firms TRM Labs and Elliptic release independent reports attributing the attack to North Korean state-sponsored actors, specifically the "TraderTraitor" group.
- Ongoing: Binance spokesperson Andie Cooper confirms that $3 billion has been frozen through the cooperation of stablecoin issuers, other exchanges, and law enforcement. The investigation into the remaining $3.3 billion continues.
Geopolitical Attribution: The North Korean Connection
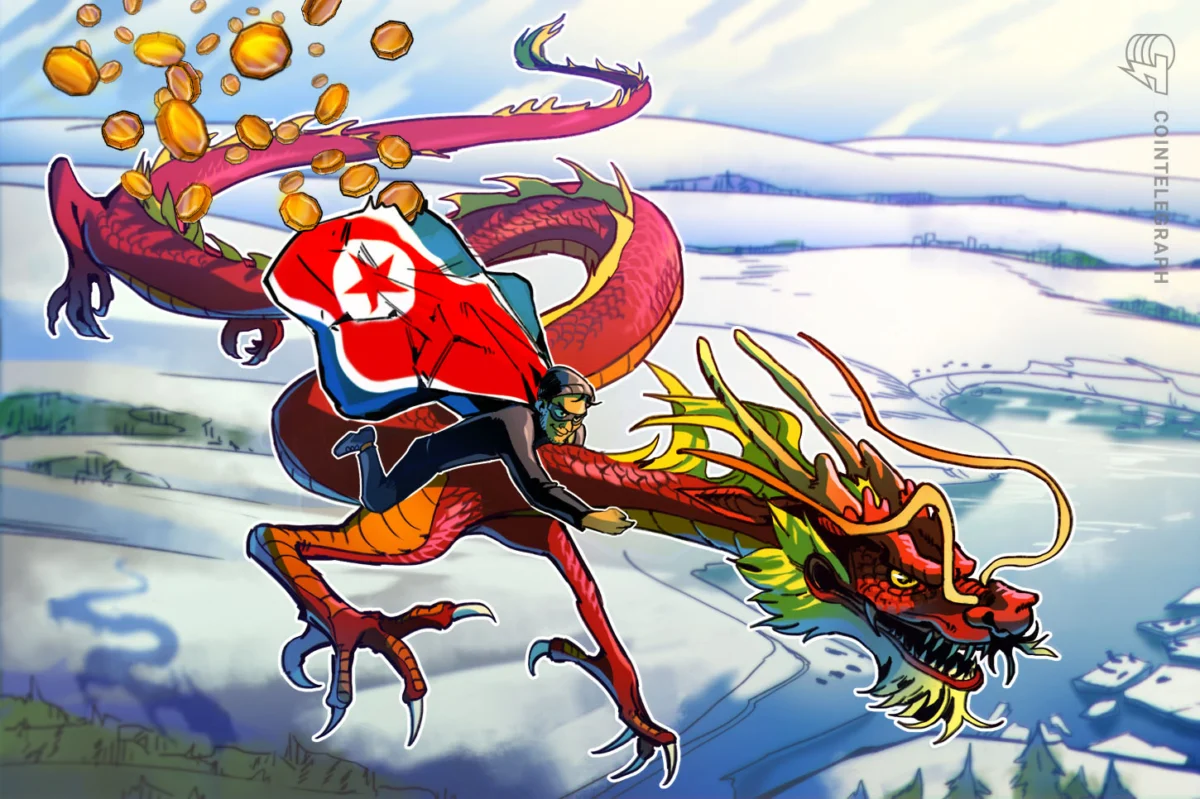
The attribution of the hack to North Korea places the incident within a broader geopolitical context. For years, the U.S. Department of the Treasury and the FBI have warned that the Democratic People’s Republic of Korea (DPRK) relies on cybercrime to fund its sanctioned nuclear weapons and ballistic missile programs. The group identified in this attack, known as TraderTraitor or the Lazarus Group, has a long history of high-stakes digital heists. This group was previously held responsible for the $1.4 billion theft from the Bybit exchange in 2025 and the $351 million exploit of Bitget earlier this year.
Forensic evidence linking this attack to North Korea includes the use of specific laundering techniques and the movement of funds into digital wallets previously associated with DPRK operations. Elliptic noted that a portion of the stolen Binance funds was transferred to a wallet address used in the Bitget heist, creating a clear "on-chain" link between the two events. For North Korea, these thefts are not merely criminal enterprises but essential state functions designed to bypass international banking restrictions and maintain the regime’s military capabilities.
Technical Analysis and Systemic Vulnerabilities
The Binance hack highlights a critical weakness in the security posture of even the largest financial institutions: the "human element." The use of a compromised laptop as a gateway to a service container capable of moving billions of dollars suggests a failure in the principle of least privilege. In a robust security architecture, no single device or employee should have the permissions necessary to authorize transactions of this magnitude without multi-factor, multi-person authentication.
Experts point out that the attack likely utilized a "supply chain" strategy. Modern software is rarely built from scratch; it relies on thousands of open-source packages. Hackers regularly target these packages, inserting malicious code that remains dormant until it is installed on a high-value target’s machine. Once active, this malware can steal session tokens, allowing hackers to impersonate the employee and access internal cloud environments—such as the service containers mentioned by Binance—without ever needing a password or a physical 2FA key.
Industry Response and Recovery Efforts
The recovery of $3 billion is a testament to the increasing "traceability" of the blockchain, despite its reputation for anonymity. Because most major cryptocurrencies operate on public ledgers, the movement of the stolen funds was visible in real-time. Binance has been working around the clock with blockchain intelligence firms and "issuers"—companies like Tether (USDT) and Circle (USDC) that have the ability to blacklist specific addresses and effectively "turn off" the stolen tokens.
"We have begun recovering affected assets for users and continue to work with law enforcement, issuers, and industry partners to trace, freeze and recover additional funds," said Binance spokesperson Andie Cooper. This collaborative effort marks a significant shift in how the crypto industry handles large-scale theft, moving toward a more unified defensive front. However, the remaining $3.3 billion consists of assets that are harder to freeze, such as Bitcoin or tokens that have already been cycled through "mixers" or "tumblers" designed to obscure their origin.
Implications for the Future of Decentralized Finance
The fallout from the Binance heist is expected to be felt for years. Regulators in the United States, Europe, and Asia are likely to use this incident as a catalyst for stricter oversight of cryptocurrency exchanges. Questions are already being raised about why a security audit did not identify the risks associated with single-employee access to service containers.
Furthermore, the incident damages the credibility of the "Proof of Reserves" movement. While Binance has promised an updated report, the delay in providing proof that user funds are indeed safe has led to a "crisis of confidence" among retail investors. If the world’s largest exchange, with its massive resources, can be compromised by a single infected laptop, the perceived safety of the entire ecosystem is called into question.
As the investigation continues, the focus will remain on two fronts: the technical remediation of Binance’s network and the international effort to prevent North Korea from successfully laundering the remaining billions. The outcome of this struggle will likely determine the regulatory trajectory of the cryptocurrency industry and the future of digital asset security. For now, the global financial community watches as Binance attempts to recover from the largest digital robbery in history, a 20-minute breach that changed the landscape of cyber warfare forever.