admin
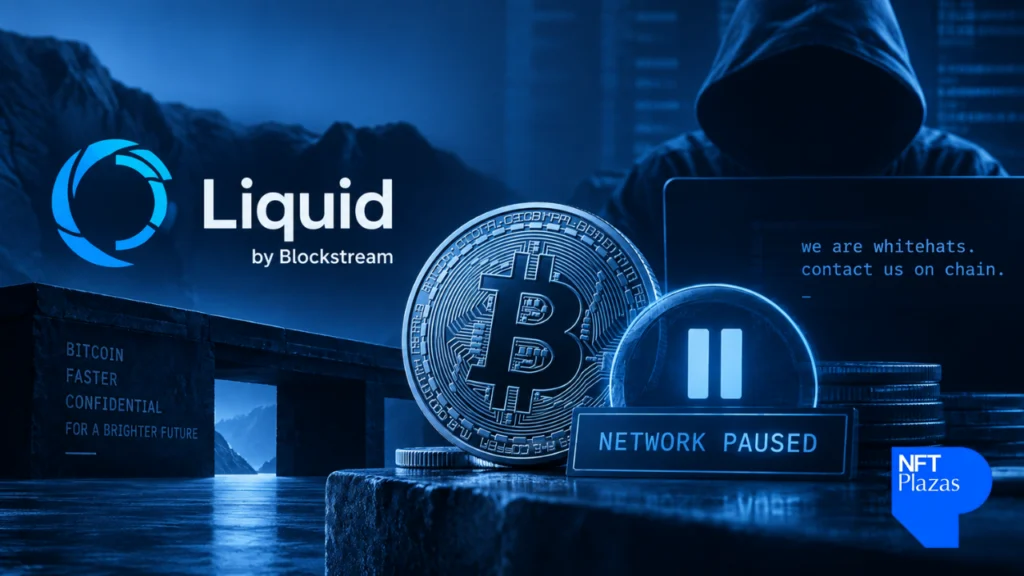
The Liquid Network, a prominent Bitcoin sidechain, has been brought to a standstill following a sophisticated exploit that saw approximately 4,000 BTC, valued at over $320 million at the time of the incident, siphoned from its federation wallet. This unprecedented event, which occurred on September 6, 2026, appears to have leveraged a critical vulnerability within the network’s underlying software, Elements, rather than a direct compromise of its cryptographic keys. The incident has cast a spotlight on the security paradigms of federated sidechains, the intricacies of their operational integrity, and ignited a contentious debate over the ethical boundaries of so-called "white-hat" hacking in the cryptocurrency space.
The Anatomy of an Exploit: A Vulnerability in Elements
The incident unfolded through a seemingly legitimate "peg-out" process, the mechanism by which L-BTC (Liquid Bitcoin) tokens on the sidechain are redeemed for native Bitcoin on the mainnet. At approximately 14:05 UTC on September 6, a sum of 4,000 L-BTC was transferred to SideSwap, a Liquid federation member operating a peg-out service. These tokens were subsequently "burned" under what appeared to be a valid Peg-out Authorization Key (PAK) authorization. Within 23 minutes, the Liquid Federation’s multi-signature wallet released approximately 3,996 BTC to the customer’s designated Bitcoin address.
Initially, the sheer scale of the withdrawal—representing about 95% of the roughly 4,200 BTC held in the federation wallet prior to the incident—triggered immediate alarms. However, further investigation by Liquid and its developer, Blockstream, revealed that the exploit did not stem from a compromise of SideSwap’s systems or the federation’s cryptographic keys. SideSwap explicitly confirmed that its infrastructure remained unbreached and its PAK was not stolen. Instead, the L-BTC used in the transaction was reportedly created illicitly through a previously undisclosed vulnerability within Elements, the open-source software powering the Liquid Network.
This distinction is crucial. The attackers did not need to bypass the robust multi-signature security of the federation’s keys or penetrate the defenses of a member entity. Rather, the vulnerability allowed for the creation of L-BTC that should not have existed, effectively counterfeiting tokens within the sidechain environment. Once these illegitimate tokens entered the normal redemption process and passed the system’s validation checks, the federation’s automated mechanisms proceeded to pay out real BTC against them, effectively draining the reserves. This highlights a fundamental challenge in sidechain security: even if the ultimate asset custody (the federation wallet) is secure, a flaw in the logic governing asset creation and transfer within the sidechain can lead to catastrophic losses.
Blockstream has yet to publicly release a comprehensive technical root cause analysis. However, it was disclosed that a fix for the underlying vulnerability had already been integrated into the Elements software codebase prior to the exploit. Disturbingly, this critical patch had not been fully deployed across all nodes within the Liquid Network when the attack occurred, leaving a window open for the exploit. This raises serious questions about release management, patch deployment protocols, and the overall resilience of decentralized networks against known, but unpatched, vulnerabilities.
Chronology of Events: From Exploit to Standoff
The timeline of the incident unfolded rapidly, gripping the cryptocurrency community:

- September 6, 14:05 UTC: Approximately 4,000 L-BTC are sent to SideSwap’s peg-out service, appearing to initiate a standard withdrawal.
- September 6, 14:28 UTC: The Liquid Federation’s wallet releases 3,996 BTC to a Bitcoin address controlled by the exploiter.
- September 6 (Later): Liquid Network issues an official confirmation via its X (formerly Twitter) account, acknowledging the withdrawal and stating the network’s bridge nodes have been disabled to prevent further transactions. Exchanges are simultaneously requested to suspend L-BTC deposits and withdrawals.
- September 6 (Evening): The party controlling the withdrawn Bitcoin leaves an on-chain message on the Bitcoin blockchain: "we are whitehats. contact us on chain." This message, embedded within a transaction, initiates a highly unusual negotiation.
- September 7 (Early): Blockstream, the primary developer behind Liquid, responds to the on-chain message with a signed Bitcoin transaction, providing an email address for direct communication.
- September 7 (Ongoing): Subsequent communications between the alleged white-hats and Blockstream are exchanged, including PGP-signed messages recorded on-chain, lending a layer of cryptographic verification to their dialogue.
- September 7 (Afternoon): The purported hackers offer to return the vast majority of the funds, but with a significant condition: Liquid must fully patch the identified vulnerability and ensure that every node running the network is updated to the secure version. They also reportedly send encrypted technical details of the vulnerability to Blockstream, according to Alex Thorn, head of research at Galaxy Digital.
- September 7 (Evening): Blockstream acknowledges the condition and begins intensive work to patch the affected infrastructure across the network. However, as of the time of publication, the withdrawn Bitcoin had not been returned to the federation wallet, maintaining the state of a tense standoff.
- September 7 (Ongoing): Liquid Network’s bridge infrastructure remains offline, with exchanges continuing to suspend L-BTC operations, effectively freezing the sidechain’s primary function.
The "White-Hat" Conundrum: Ethics Under Scrutiny
The self-proclaimed "white-hat" status of the actors behind the exploit has sparked a fervent debate within the crypto community, highlighting an increasingly difficult distinction in the realm of decentralized security incidents. While the attackers claimed benevolent intentions, their methodology—exploiting a critical vulnerability to extract hundreds of millions of dollars before demanding conditions for the funds’ return—deviates significantly from conventional white-hat practices.
Charles Guillemet, Chief Technology Officer at Ledger, was among those who publicly questioned this characterization. He argued that taking such a substantial amount of funds before disclosure fundamentally differs from the established norms of security research, where vulnerabilities are typically reported privately and responsibly, often with a grace period for remediation, before any public action or fund movement. The prevailing sentiment among many cybersecurity professionals is that true white-hat hackers do not hold funds hostage as a condition for disclosure or remediation.
This incident forces a re-evaluation of the ethical framework surrounding security exploits in the crypto world. Is an actor who identifies a vulnerability, exploits it to gain control of funds, and then offers to return them post-remediation, a security researcher or an attacker leveraging an exploit for leverage? The answer has profound implications for how the industry responds to and categorizes such events, potentially influencing future regulatory perspectives and legal precedents. The financial magnitude of the Liquid exploit amplifies this ethical grey area, moving it from a theoretical discussion to a tangible, high-stakes dilemma.
Broader Implications: Sidechain Security, Reputation, and Market Confidence
The Liquid Network exploit carries significant implications for the broader cryptocurrency ecosystem, particularly concerning the security of sidechains and other interoperability solutions.
- Sidechain Security Model: The incident underscores that while cryptographic key security is paramount, it is not the sole vulnerability vector. Software logic flaws within the sidechain’s operational code, especially in critical components like asset issuance and redemption mechanisms, can be equally devastating. This will likely prompt a re-evaluation of security audit scopes for sidechains, moving beyond just multi-signature wallets to comprehensive code audits of the underlying protocols.
- Reputational Damage: For Liquid Network and its primary developer, Blockstream, the exploit represents a substantial reputational blow. Despite Blockstream’s standing as a leading Bitcoin development company, the incident challenges the perception of Liquid as a secure and reliable layer-2 solution for Bitcoin. Such incidents can erode user trust, affecting adoption rates and the willingness of other projects to integrate with the network.
- Impact on Federated Models: Liquid operates as a federated sidechain, relying on a consortium of trusted entities (the federation) to validate transactions and manage the bridge to the mainnet. While the federation’s keys remained secure, a flaw in the underlying Elements software allowed the exploit to bypass this federated security model. This raises questions about the robustness of federated designs against internal software vulnerabilities and whether greater decentralization or alternative security mechanisms are needed.
- Market Confidence: While Bitcoin’s main network remained unaffected, the loss of $320 million from a prominent sidechain can send ripples through the broader market. It serves as a stark reminder of the inherent risks in the nascent DeFi and layer-2 ecosystems, potentially leading to increased caution among investors and users interacting with such platforms.
- Regulatory Scrutiny: Such high-profile exploits, particularly those involving substantial financial losses and complex ethical debates, are likely to attract the attention of financial regulators worldwide. They could bolster arguments for stricter oversight of cryptocurrency platforms, especially those handling significant amounts of locked capital.
- Operational Disruption: The prolonged pause of Liquid’s bridge infrastructure has disrupted services that rely on its ability to move assets between the sidechain and Bitcoin. While other assets issued on Liquid, such as USDT, DePix, and various tokenized real-world assets, were reported to be unaffected in terms of their underlying integrity, their transferability and utility are severely hampered by the network-wide freeze. This demonstrates the cascading effects of a single point of failure (the bridge) in an interconnected financial system.
The Path Forward: Remediation and Rebuilding Trust
For Liquid Network, the immediate priorities are unambiguous: a full and verifiable patch of the identified vulnerability, followed by the rigorous update of every affected node across the network. Simultaneously, efforts to negotiate the return of the withdrawn Bitcoin remain critical, though their success hinges on the willingness of the purported white-hats to honor their stated intentions. Only after these steps are demonstrably completed can the federation even consider the safe reopening of its bridge.
As of September 7, the substantial sum of 4,000 BTC remained outside the federation’s control, and the Liquid Network itself remained in a paused state. The incident is still developing, with the full technical explanation of how such a significant amount of Bitcoin was able to leave the reserve wallet yet to be made public. The coming days and weeks will be crucial in determining the long-term impact on Liquid Network, the future of federated sidechains, and the evolving landscape of security and ethics in the rapidly advancing world of decentralized finance. The crypto community watches closely, hoping for a resolution that reinforces security and trust, rather than further eroding it.