admin
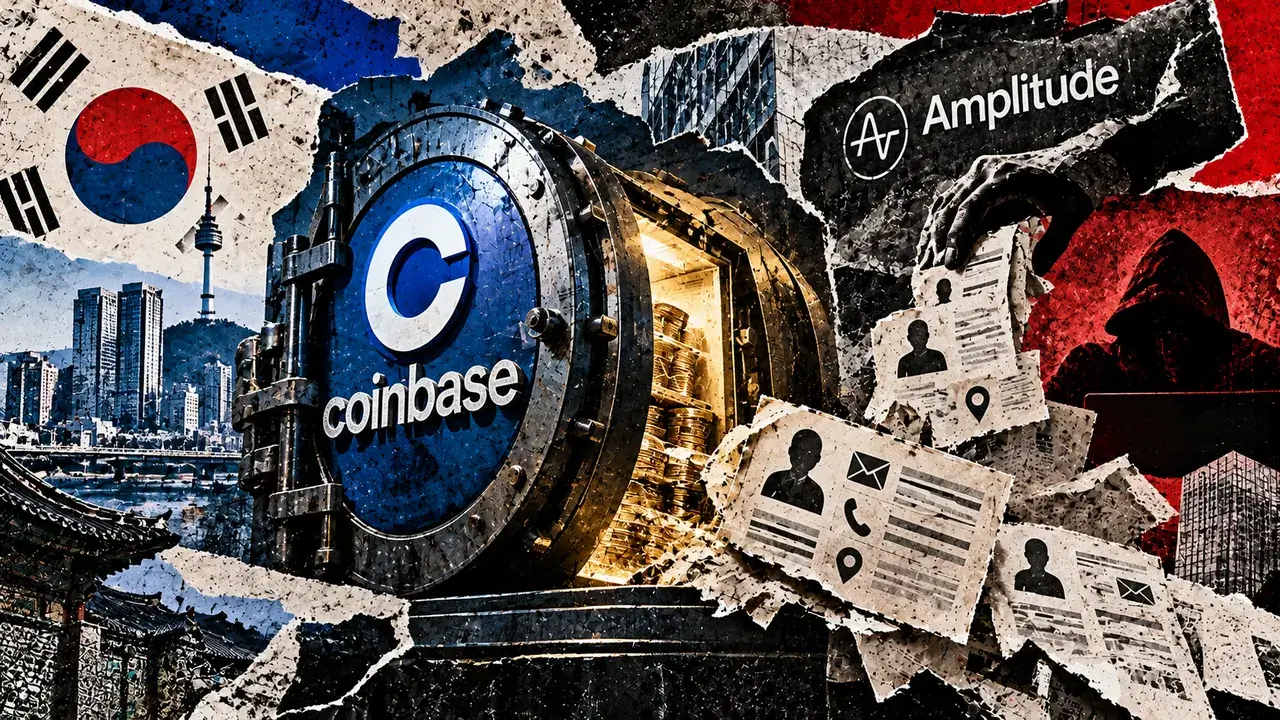
Coinbase has vehemently denied suffering a security breach following an incident at its third-party analytics vendor, Amplitude, which resulted in the exposure of contact information for a “small subset” of its customers. The cryptocurrency exchange addressed the situation in an official post on X, formerly Twitter, on October 28, 2026, stating that its internal systems remained secure and customer funds were unaffected. This incident, however, has surfaced amidst a wave of cybersecurity vulnerabilities impacting major financial institutions, particularly in South Korea, prompting heightened concern from industry leaders about the growing risks of compromised personal and financial data.
The disclosure from Coinbase occurred concurrently with reports of significant cyber incidents affecting South Korean cryptocurrency exchange Bithumb, as well as financial services firms Daishin Securities and Mirae Asset Global Investments. The confluence of these events led Binance founder Changpeng Zhao, widely known as CZ, to issue a stark warning on X regarding the escalating threats posed by exposed financial information. Zhao identified the four companies involved in recent data leaks and elaborated on the insidious ways criminals exploit compromised customer records, including phishing attacks, SIM swapping, and sophisticated social engineering schemes. He emphasized that while preventing leaks entirely may be impossible, individuals can take proactive steps to safeguard themselves.
Coinbase has stated that it is in the process of notifying all affected customers and relevant regulatory bodies. However, the company has not yet disclosed the precise number of individuals impacted by the Amplitude incident or the specific types of contact details that were compromised. The exchange’s swift denial of a direct breach underscores its commitment to maintaining customer trust, yet the incident highlights the inherent risks associated with relying on third-party vendors for critical data processing and analytics.
South Korea Grapples with Multi-Front Cyber Assaults
The cybersecurity landscape in South Korea was significantly disrupted on Wednesday, October 28, 2026, as authorities launched comprehensive investigations into unauthorized access incidents at three prominent financial institutions: Bithumb, Daishin Securities, and Mirae Asset Global Investments. This coordinated effort by South Korean regulators aims to assess the full scope of these breaches and identify responsible parties.
Daishin Securities officially confirmed that personal and financial information belonging to 38,490 of its customers was exposed. The company detected suspicious activity on October 17, 2026, which subsequently led to the data compromise. The compromised records reportedly include sensitive details such as customer names, email addresses, residential addresses, login credentials, bank names, and encrypted account and telephone numbers. Despite the significant exposure of customer data, Daishin Securities asserted that it had found no evidence of unauthorized access to its core operating systems or any subsequent misuse of the leaked information.
In parallel, Bithumb, one of South Korea’s largest cryptocurrency exchanges, reported that attackers gained access to an internal employee communications system. The initial assessment suggests that this breach may have exposed information pertaining to staff members, subsidiaries, and business partners. The exchange is currently conducting a thorough investigation to determine if customer records were also compromised as a result of this internal system intrusion. The Financial Services Commission (FSC) of South Korea has stated that, as of its latest update, it has not confirmed any exposure of wallet addresses or information that could facilitate fraudulent cryptocurrency transfers, offering a sliver of reassurance to Bithumb’s customer base.
Mirae Asset Global Investments also disclosed a separate security incident, reporting unauthorized access to its internal web systems. The investment firm, however, was quick to emphasize that investor information and other sensitive financial records remained unaffected by this intrusion. This distinction is crucial, as it suggests a more contained breach compared to the potential implications for Bithumb and Daishin Securities.
The collective nature of these breaches has prompted an emergency regulatory meeting and has triggered on-site investigations by relevant authorities. This situation extends a concerning pattern of cyber incidents that have previously affected at least 16 other South Korean financial institutions, underscoring a persistent vulnerability within the nation’s financial sector.
A Growing Tide of Crypto Data Breaches and CZ’s Stark Warning
The incidents involving Coinbase and the South Korean financial institutions are not isolated events but rather part of a broader trend of escalating cybersecurity threats targeting the cryptocurrency industry and its associated service providers. Earlier in 2026, several other notable breaches occurred, including those affecting Israeli crypto broker Bits of Gold and hardware wallet manufacturer Trezor.
In August 2026, Bits of Gold announced an unauthorized access to its analytics infrastructure. This breach potentially exposed customer names, contact information, Israeli identification numbers, bank details, and public wallet addresses. The breadth of information compromised raised immediate concerns about identity theft and financial fraud.
Trezor, a widely recognized provider of hardware cryptocurrency wallets, also experienced a data breach. This incident, which involved their shipping provider, ShipMonk, led to the exposure of customer names, telephone numbers, and delivery addresses. While seemingly less sensitive than financial details, this information can be instrumental in targeted phishing campaigns or even physical threats.
Adding to the concern, a separate incident in September 2026 impacted Trezor’s email marketing provider, Brevo. This breach resulted in the exfiltration of 347,149 marketing email addresses. Malicious actors subsequently used this compromised list to distribute fraudulent messages, attempting to trick users into revealing their wallet recovery phrases—a critical piece of information that grants full access to cryptocurrency holdings.
These cumulative incidents have intensified anxieties among cryptocurrency users and industry participants about attackers leveraging information obtained from sources outside of an exchange’s core trading and custody systems. The interconnectedness of the digital economy means that a vulnerability in one service provider can have cascading effects across multiple platforms and users.
Changpeng Zhao’s warning on X reflects a deep understanding of these evolving threats. He highlighted that leaked personal information, when combined with publicly available cryptocurrency holdings data, can expose investors to a spectrum of risks. These include not only online account compromises but also more severe threats such as physical extortion and robbery. The direct correlation between digital footprints and real-world danger is a chilling implication of these data leaks.
Zhao provided a series of actionable recommendations for cryptocurrency users to bolster their defenses:
- Utilize distinct email aliases and phone numbers: Separating communication channels for cryptocurrency exchanges from personal accounts can limit the impact of a breach on one service.
- Transition from SMS authentication: Replacing SMS-based two-factor authentication (2FA) with more secure alternatives like passkeys or dedicated hardware security keys significantly reduces the risk of SIM swapping attacks.
- Enable withdrawal restrictions: Many platforms offer options to limit or temporarily disable withdrawals, providing an extra layer of security against unauthorized transactions.
- Regularly review account sessions and API permissions: Proactively monitoring active sessions and authorized API connections can help detect and disable any unauthorized access.
- Exercise extreme caution with unsolicited communications: Users are urged to maintain a healthy skepticism towards any unsolicited messages claiming to be from exchange support, as these are often phishing attempts designed to elicit sensitive information.
Broader Implications and Future Outlook
The recent surge in data breaches across both traditional financial institutions and the cryptocurrency sector underscores a critical need for enhanced cybersecurity measures and greater transparency from all entities handling sensitive customer data. The fact that breaches are occurring through third-party vendors, as seen with Coinbase and Amplitude, highlights the importance of robust vendor risk management protocols. Companies must rigorously vet their partners and ensure they adhere to stringent security standards.
The regulatory response in South Korea, with investigations and emergency meetings, signals a growing awareness among governments about the systemic risks posed by these cyber threats. As the digital asset space continues to mature and integrate more deeply into the global financial system, regulators will likely impose stricter cybersecurity mandates and increase oversight.
For individual users, the recurring breaches serve as a potent reminder that digital security is an ongoing responsibility. The advice from figures like CZ is invaluable, emphasizing a multi-layered approach to personal security in the digital realm. The shift towards more advanced authentication methods and the vigilant monitoring of online accounts are no longer optional but essential practices for anyone engaging with financial services, especially in the volatile cryptocurrency market.
The long-term implications of these data exposures are multifaceted. Beyond the immediate financial and personal risks to affected individuals, repeated security failures can erode public trust in both traditional financial institutions and the burgeoning cryptocurrency ecosystem. Rebuilding and maintaining that trust will require a concerted effort from all stakeholders – exchanges, vendors, regulators, and users – to prioritize and invest in robust, evolving cybersecurity strategies. The current climate demands a proactive, rather than reactive, approach to security, ensuring that the digital financial future is built on a foundation of resilience and trust.