admin
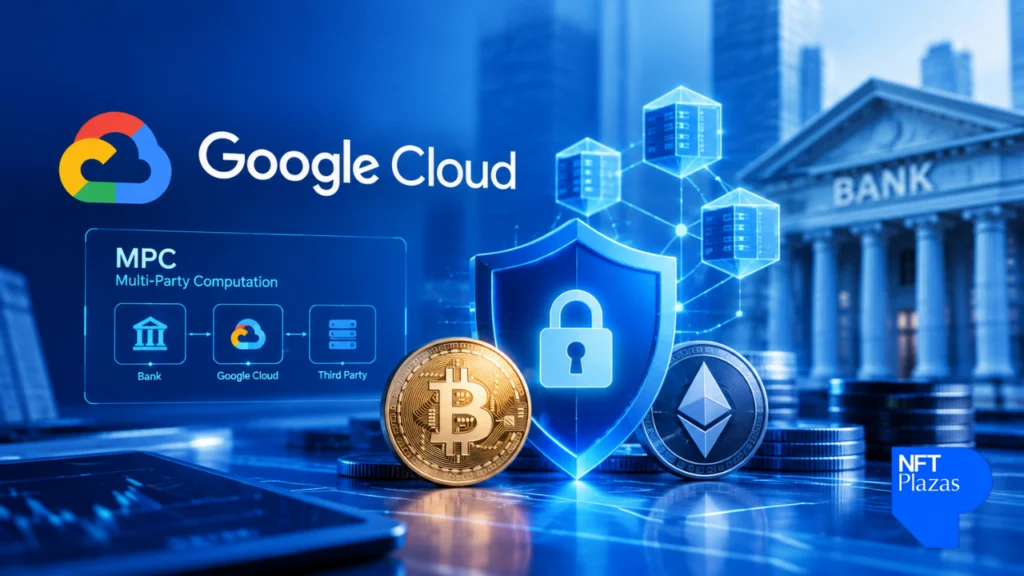
Google is embarking on a significant expansion into the digital asset security landscape, announcing a new multi-party computation (MPC) based custody system designed to fortify cryptocurrency holdings for banks and other financial institutions. This strategic initiative, dubbed "Google Multi-Party Compute," arrives at a critical juncture for the digital asset ecosystem, as the industry grapples with escalating threats ranging from sophisticated private-key theft and AI-driven cyberattacks to the long-term, existential challenge posed by future quantum computers. Currently in a private preview phase with a select group of institutional partners, Google Cloud aims to roll out the service commercially in early 2027. This move positions the technology giant as a pivotal player in constructing the robust security infrastructure essential for broader institutional adoption of cryptocurrencies and tokenized assets.
The Imperative for Advanced Digital Asset Security
The core vulnerability in cryptocurrency lies in the private key—a string of alphanumeric characters that grants ultimate control over associated digital assets. If compromised, a private key allows unauthorized access and transfer of funds, with blockchain transactions being largely irreversible once confirmed. For traditional financial institutions (TradFi) and asset managers, who are increasingly allocating substantial capital to cryptocurrency reserves, a single compromised key could translate into catastrophic financial losses and severe reputational damage. The stakes are particularly high given the volatile nature of digital assets and the substantial value they can represent. Industry reports from firms like Chainalysis have consistently highlighted billions of dollars lost annually to hacks and exploits, many stemming directly from private key compromises or inadequate security protocols. For instance, 2022 alone saw over $3.8 billion stolen in crypto hacks, with a significant portion attributable to private key and seed phrase vulnerabilities. This underscores the urgent need for enterprise-grade security solutions that transcend conventional approaches.
Google’s MPC Technology: A Paradigm Shift in Key Management
Google’s Multi-Party Compute system directly confronts this fundamental risk by fundamentally altering how cryptographic keys are managed. Instead of storing a complete private key in a single, vulnerable location—a single point of failure—MPC technology distributes cryptographic key shares across multiple, isolated environments. This architectural shift significantly enhances security by preventing any one party or system from having full control over the private key.
Consider a practical application: a financial institution could strategically divide a private key into three or more shares. One share might reside on the institution’s secure on-premises infrastructure, another within the Google Cloud environment, and a third with an entirely separate, independent security provider. When a transaction requires authorization, these distributed components collaboratively generate a valid digital signature. Crucially, this signature is created without ever reconstructing the complete private key in any single location. This distributed consensus mechanism means that an attacker would need to simultaneously compromise multiple, disparate systems to gain control of assets, dramatically increasing the complexity and cost of a successful attack.
A cornerstone of Google’s offering is its commitment to customer autonomy. The company explicitly states that customers retain ultimate control over their keys. Google cannot access the key shares in unencrypted form, even when those shares are hosted on its cloud infrastructure, thereby mitigating concerns about centralized control or potential access by the service provider. Beyond the core key management, the MPC system also supports sophisticated transaction controls. These include granular features like spending limits, whitelisted destination addresses, and configurable internal authorization procedures. Such capabilities empower institutions to enforce strict governance, define clear rules regarding who can approve transfers, and under what specific conditions, aligning digital asset operations with existing compliance frameworks.
However, even with its advanced design, MPC is not an absolute panacea. Its efficacy is inherently tied to the implementation and operational discipline of the institutions utilizing it. The distribution of key shares, the configuration of permissions, and the rigor of approval processes all play critical roles. If attackers manage to compromise a sufficient number of authorized participants or their respective environments, unauthorized transactions could still occur. This highlights that while MPC offers a robust technological solution, it must be integrated into a comprehensive security strategy that includes strong operational controls, continuous monitoring, and employee training.
The Evolving Cyber Threat Landscape: AI and Quantum
Google’s entry into institutional crypto custody is particularly timely given the rapid evolution of the cybersecurity landscape, driven by advancements in artificial intelligence (AI) and the looming specter of quantum computing.
AI’s Double-Edged Sword in Cybersecurity:
Artificial intelligence is fundamentally reshaping both offensive and defensive cybersecurity strategies. Malicious actors are increasingly leveraging AI-powered tools to automate the discovery of software vulnerabilities, craft highly convincing phishing attacks, and streamline their operational exploits. For instance, AI can be used to analyze vast codebases to pinpoint weaknesses, or to generate hyper-realistic deepfakes for social engineering. On the flip side, security researchers and defenders are also deploying AI to identify anomalies, predict attack vectors, and rapidly respond to threats, creating an ongoing arms race.
Recent incidents underscore the growing complexity. While the original article cited a potential vulnerability in the XRP Ledger, the broader trend shows a proliferation of sophisticated attacks targeting various blockchain systems. These often exploit smart contract vulnerabilities, cross-chain bridge weaknesses, or social engineering tactics. Ethereum co-founder Vitalik Buterin has been a prominent voice in warning the industry about the potential for AI-accelerated mathematical research to weaken certain cryptographic systems sooner than anticipated. His concerns extend beyond just quantum computing, suggesting that AI could significantly accelerate cryptanalytic attacks against algorithms currently deemed secure, demanding a proactive re-evaluation of cryptographic primitives. For financial institutions, this dynamic environment means that protecting digital assets extends far beyond mere key storage; it necessitates dynamic permission management, real-time transaction monitoring, and agile incident response capabilities. Google’s MPC framework directly addresses a crucial part of this challenge by distributing signing authority, making it exponentially harder for a single compromised component, potentially identified or exploited by AI, to authorize an illicit transfer.
The Long-Term Quantum Threat:
Beyond AI, quantum computing presents a more distant yet potentially disruptive threat to current cryptographic standards. While no quantum computer today possesses the scale or stability to break modern encryption algorithms, theoretical advances suggest that sufficiently powerful quantum machines could eventually undermine some of the cryptographic methods underpinning digital assets, including those used in Bitcoin and Ethereum.

Research indicates that approximately 6.9 million Bitcoin could face potential quantum-related risks because their public keys have been exposed through past transactions. This doesn’t imply an immediate threat but rather highlights a vulnerability that could be exploited if quantum computing capabilities advance significantly. The risk is contingent on the development of powerful quantum computers and the absence of adequate post-quantum cryptographic protections when such capabilities emerge.
It’s important to clarify that MPC, while enhancing security against credential compromise, does not inherently make a wallet resistant to quantum attacks. The cryptographic algorithms themselves must evolve to withstand quantum threats. Google’s longer-term security strategy will undoubtedly need to incorporate ongoing research and development in post-quantum cryptography (PQC), which focuses on creating new cryptographic primitives designed to resist attacks from quantum computers. This will involve future upgrades to the underlying cryptographic libraries and protocols used within their MPC framework to ensure future-proofing.
Background and Context: The Institutional Embrace of Digital Assets
The burgeoning interest from traditional finance in digital assets is a primary driver behind the demand for advanced security solutions like Google’s MPC offering. Over the past few years, the landscape has shifted dramatically. Major financial institutions, including asset managers, hedge funds, and even retail banks, are increasingly exploring or actively engaging with cryptocurrencies, tokenized securities, and blockchain technology for various applications.
This institutional pivot is fueled by several factors:
- Regulatory Clarity: While still evolving, regulatory frameworks in key jurisdictions are slowly providing more guidance, giving institutions a clearer path to participation. The approval of spot Bitcoin ETFs in various markets is a testament to this shift.
- Market Opportunity: The sheer size and growth potential of the digital asset market, coupled with its diversification benefits, are attractive to institutional investors.
- Technological Innovation: Blockchain’s underlying technology promises efficiencies in settlement, asset management, and new financial product creation through tokenization.
- Client Demand: A growing segment of high-net-worth individuals and corporate clients are demanding access to digital asset investments, pushing institutions to provide compliant and secure offerings.
However, the primary barrier for many institutions has been the perceived security risks and the lack of enterprise-grade infrastructure that meets their stringent compliance, governance, and operational requirements. Traditional financial firms operate under strict regulatory oversight (e.g., KYC/AML, Basel III, MiFID II) that demands robust audit trails, segregated accounts, and ironclad security. Existing crypto security solutions, particularly those originating from the retail or early-stage crypto ecosystem, often fall short of these institutional benchmarks. Google’s move is a direct response to this gap, aiming to bridge the trust deficit by offering a solution built on its formidable cloud infrastructure and security expertise. The fact that Alphabet, Google’s parent company, is already leveraging MPC to protect its own digital assets on networks like Ethereum and Solana provides a strong testament to the technology’s internal validation and efficacy.
Competitive Landscape and Google’s Strategic Positioning
Google is entering an increasingly competitive, yet rapidly expanding, market for institutional digital asset custody. Established players like Fireblocks, BitGo, Ledger Enterprise, and Fordefi have already carved out significant niches, offering a suite of custody infrastructure, transaction security tools, and operational frameworks tailored for institutional clients. These companies have spent years building trust and expertise within the crypto-native institutional space.
What makes Google’s entry particularly impactful is its unique competitive advantage:
- Brand Trust and Scale: Google’s reputation as a global technology leader and its massive cloud infrastructure (Google Cloud) offer an unparalleled level of trust and scalability that resonates strongly with traditional financial institutions. For banks wary of nascent crypto-native providers, Google represents a familiar and reliable partner.
- Integration Capabilities: Google Cloud’s extensive suite of services and APIs can facilitate seamless integration of the MPC custody solution with an institution’s existing legacy IT systems, enterprise resource planning (ERP) software, and compliance tools. This "cloud-native" approach can significantly reduce implementation friction.
- Security Expertise: Google’s deep expertise in cybersecurity, cryptography, and distributed systems, honed over decades of protecting vast amounts of user data and critical infrastructure, is directly transferable to digital asset security.
- Holistic Offering: Beyond just custody, Google could potentially offer a broader ecosystem of services, from data analytics on blockchain activity to AI-powered fraud detection, leveraging its diverse technological capabilities.
However, challenges remain. Google will need to demonstrate its understanding of the specific nuances of digital asset custody, including complex regulatory requirements across different jurisdictions. Pricing models, full feature sets beyond the initial preview, and the speed of institutional adoption will all be critical factors in determining its long-term success. The planned commercial availability in early 2027 suggests a methodical, long-term strategy, allowing time for extensive testing, refinement, and regulatory engagement.
Broader Implications and Future Outlook
Google’s MPC initiative signifies a pivotal moment in the evolution of digital asset security and the broader integration of blockchain technology into mainstream finance.
- Elevated Industry Standards: The entry of a tech titan like Google into institutional crypto custody will likely raise the bar for security standards across the industry, compelling existing providers to innovate further and smaller players to enhance their offerings.
- Accelerated Institutional Adoption: By providing a highly secure, enterprise-grade custody solution from a trusted brand, Google could significantly reduce the perceived risk for traditional financial institutions, thereby accelerating their entry and deeper engagement with digital assets. This could unlock substantial capital flows into the crypto market.
- Validation of MPC Technology: Google’s endorsement and deployment of MPC at an institutional level validate the technology as a leading solution for key management in the digital asset space, potentially driving its broader adoption across various sectors.
- Shift in Financial Infrastructure: This development underscores a broader trend where major technology companies are increasingly becoming critical infrastructure providers for the financial system. Just as Google Cloud supports traditional banking operations, it is now extending that role to the nascent digital asset economy.
- Ongoing Security Evolution: The initiative highlights that digital asset security is not a static problem but an evolving challenge requiring continuous innovation. The threats from AI and quantum computing necessitate a dynamic approach to security that integrates technological advancements with robust operational protocols.
Ultimately, Google’s foray into digital asset custody reflects a broader understanding that as financial institutions increasingly embrace the crypto market, foundational security solutions that distribute control, strengthen transaction oversight, and proactively prepare for emerging threats are not merely desirable, but absolutely essential. Whether Google can establish itself as a dominant custody provider will depend on the framework’s proven reliability, unparalleled security, and its ability to seamlessly meet the diverse and stringent requirements of the global financial sector. Nevertheless, this development unmistakably signals that major technology companies now view digital asset protection as a critical and indispensable component of the financial system’s ongoing transformation.