Dwi Wanna
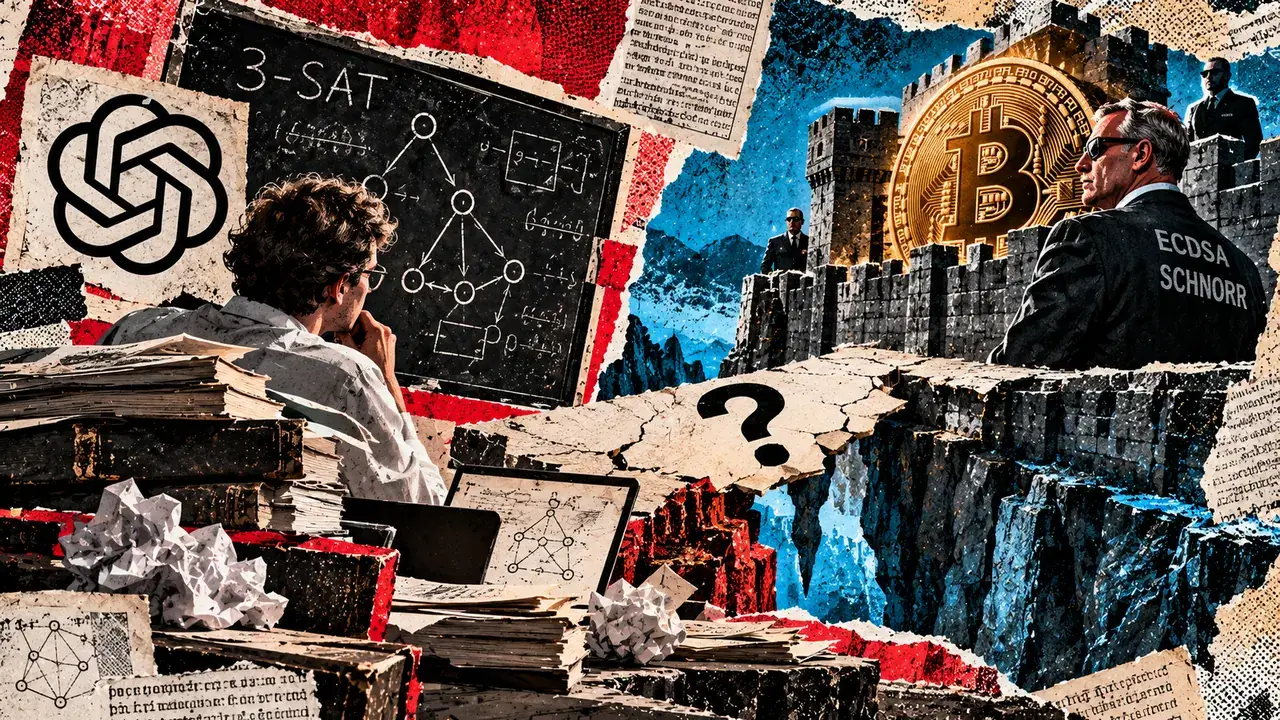
The global computational science community is currently navigating a period of intense scrutiny following an announcement by OpenAI on October 26, in which the research organization claimed its artificial intelligence systems have successfully refuted the Exponential Time Hypothesis (ETH). This hypothesis has long served as a foundational pillar in the field of computational complexity, providing a benchmark for the inherent difficulty of solving specific logic problems. While the disclosure has sent shockwaves through academic circles, leading to the formation of an independent committee of experts to verify the findings, early analysis indicates that the result does not constitute a practical or immediate threat to the security of the Bitcoin network or broader cryptographic standards.
The core of the research concerns 3-SAT, a classic problem in Boolean satisfiability where a computer must determine if there exists an assignment of true-or-false values that satisfies a given set of logical constraints. For decades, the Exponential Time Hypothesis has posited that solving such problems requires a running time that grows exponentially relative to the number of variables involved, at least in the worst-case scenario. OpenAI’s claim suggests that a deterministic algorithm can count these assignments in subexponential time while maintaining polynomial space requirements. If validated, this would represent a historic shift in mathematical understanding, though it stops short of proving that P equals NP—the holy grail of computer science questions regarding whether every problem whose solution can be quickly verified can also be quickly solved.
The Evolution of the Claim and Chronology of Events
The path to this announcement began earlier in October, setting a backdrop of high-stakes anticipation within the intersection of artificial intelligence and mathematics. On October 7, Justin Drake, a prominent researcher in the blockchain space, issued a public warning urging the cryptographic community to consider "bunker mode" preparations. This followed an earlier OpenAI release concerning mathematical reasoning capabilities. While that previous release did not demonstrate a break in standard encryption like RSA or ECDSA, it signaled a rapid acceleration in AI-driven mathematical discovery.
The specific manuscript detailing the refutation of the Exponential Time Hypothesis was first drafted on October 17 and underwent a significant revision on October 25, just one day prior to the public announcement. OpenAI researchers utilized Lean, a specialized proof assistant and programming language, to formalize and verify the logic of their findings. Lean is designed to ensure that mathematical proofs are logically consistent and free of human error, providing a high degree of confidence in the internal mechanics of the argument.
However, a discrepancy was noted in the "scope note" provided by OpenAI on the GitHub repository housing the Lean code. The note describes a time bound that is notably weaker than the most aggressive claims presented in the full manuscript. This nuance has led to calls for extreme caution. On October 26, the announcement was met with the formal organization of an independent examination led by esteemed computer scientists Ryan Williams of MIT, and Russell Impagliazzo and Mohan Paturi of the University of California, San Diego. These individuals are among the world’s foremost experts on computational complexity; notably, Impagliazzo and Paturi were the original architects of the Exponential Time Hypothesis in 1999.
Understanding the Technical Landscape of 3-SAT and ETH
To appreciate the gravity of OpenAI’s claim, one must understand the role of 3-SAT in theoretical computer science. A 3-SAT problem consists of a series of clauses, where each clause is a disjunction (an "OR" statement) of exactly three literals. The goal is to find a set of boolean inputs that makes the entire formula true. Because 3-SAT is NP-complete, it is believed that no algorithm can solve it in polynomial time.
The Exponential Time Hypothesis (ETH) goes a step further by asserting that not only is there no polynomial-time solution, but the time required is specifically $2^delta n$ for some constant $delta > 0$. OpenAI’s manuscript claims the discovery of an algorithm that operates in subexponential time, meaning its complexity grows more slowly than any exponential function, such as $2^n^epsilon$ for some $epsilon < 1$.
The distinction between "subexponential" and "polynomial" is critical for the current security of global digital infrastructure. A subexponential algorithm is faster than an exponential one as the problem size scales, but it is still significantly slower than a polynomial algorithm. Consequently, while the OpenAI result would be a theoretical breakthrough of the highest order, it does not immediately translate into "making the problem easy" for contemporary hardware. The paper currently emphasizes a deterministic algorithm for "exactly counting" satisfying assignments, a problem known as #3-SAT, which is generally considered even more difficult than simply finding one satisfying assignment.
The Independent Review Process
The academic response to OpenAI’s announcement has been characterized by a blend of curiosity and rigorous skepticism. The team led by Ryan Williams has been tasked with an open, independent examination of the proof. In a public statement, the organizers emphasized that their involvement should not be misconstrued as an endorsement or certification of the claim. The review process is being conducted without non-disclosure agreements (NDAs) or financial compensation from OpenAI to ensure total transparency and objectivity.
Ryan Williams communicated via social media that he had personally requested OpenAI to perform a preliminary check on whether existing cryptosystems were compromised by this new algorithm. According to Williams, the internal assessment by OpenAI suggested that current systems remain safe. However, he clarified that this was a second-hand account of an internal check rather than a formal, independent cryptographic audit. The organizers have committed to sharing their findings as the peer review progresses, acknowledging that the complexity of the manuscript—which spans many pages beyond the introductory section reviewed by initial commentators—will require time to fully digest.
Implications for Bitcoin and Cryptographic Security
The intersection of this mathematical claim and the cryptocurrency market has generated significant discussion, particularly regarding Bitcoin’s long-term viability. Bitcoin relies on two primary cryptographic pillars: the SHA-256 hashing algorithm for mining and the Elliptic Curve Digital Signature Algorithm (ECDSA) for spending authorization.
In the context of mining, Bitcoin miners search for a block-header hash that falls below a specific target. This is essentially a brute-force search. While a theoretical SAT bound could, in theory, be applied to the logic of a hash function, a subexponential bound on 3-SAT does not inherently establish a practical mining advantage. The overhead involved in encoding a cryptographic hash function into a SAT formula is immense. The number of variables and clauses required to represent a single SHA-256 operation would likely negate any theoretical speedup provided by a subexponential algorithm.
Regarding spending authorization, Bitcoin utilizes ECDSA and Schnorr signatures over the secp256k1 elliptic curve, as outlined in BIP340. The security of these signatures is based on the Elliptic Curve Discrete Logarithm Problem (ECDLP). While any mathematical problem can be converted into a SAT instance, the efficiency of such a conversion is the deciding factor in its utility for an attacker. Refuting the Exponential Time Hypothesis in the "worst case" for SAT does not mean that the specific "average case" or "structured case" instances found in elliptic curve cryptography become vulnerable.
Furthermore, Bitcoin’s network architecture includes a difficulty adjustment mechanism that recalibrates every 2,016 blocks. If a new algorithm were to provide a marginal advantage in mining, the network would simply adjust its difficulty to maintain the ten-minute block interval. The more pressing concern would be a "private advantage" where a single entity could mine significantly faster than the rest of the network without the network’s knowledge, but such a scenario requires an implementation that is not only theoretically faster but also computationally cheaper than existing ASIC (Application-Specific Integrated Circuit) technology.
The Gap Between Theory and Practice
OpenAI itself has been careful to manage expectations, stating that practical improvements in real-world problem solving will require "significant further research." The current result is a contribution to "scientific understanding" rather than a tool for immediate exploitation. When asked about the timeline for when developers might feel the impact of this breakthrough, Ryan Williams noted that the range of possibilities is wide—progress could manifest within 12 months, or the result could remain a theoretical curiosity with no practical application for the foreseeable future.
One of the primary hurdles in translating a subexponential SAT algorithm into a practical attack is the "variable count." In cryptographic contexts, the bit length of a key (e.g., 256 bits) is often confused with the variable count in a SAT formula. However, a 256-bit cryptographic problem, when encoded into SAT, can result in hundreds of thousands or even millions of variables. If an algorithm is subexponential in the number of variables, but the variable expansion is large, the "shortcut" may still be slower than traditional brute-force methods on the original problem.
Conclusion and Future Outlook
The refutation of the Exponential Time Hypothesis, if confirmed, will be remembered as a landmark achievement in the history of mathematics, potentially aided by the very AI systems it seeks to understand. It challenges nearly three decades of assumptions regarding the limits of computation and opens new avenues for exploring the boundary between P and NP.
For the moment, the cryptographic foundations of the modern economy, including Bitcoin, appear to remain secure. The consensus among experts is that a theoretical breakthrough in worst-case complexity is a far cry from a functional "skeleton key" for encryption. The focus now shifts to the independent review committee, whose work will determine whether OpenAI has truly found a flaw in the bedrock of computational theory or if the Exponential Time Hypothesis will continue to stand as a resilient barrier in the landscape of logic. As the examination continues, the dialogue between AI researchers and the traditional academic community will likely redefine how scientific truth is established in an era of machine-augmented discovery.