Dwi Wanna
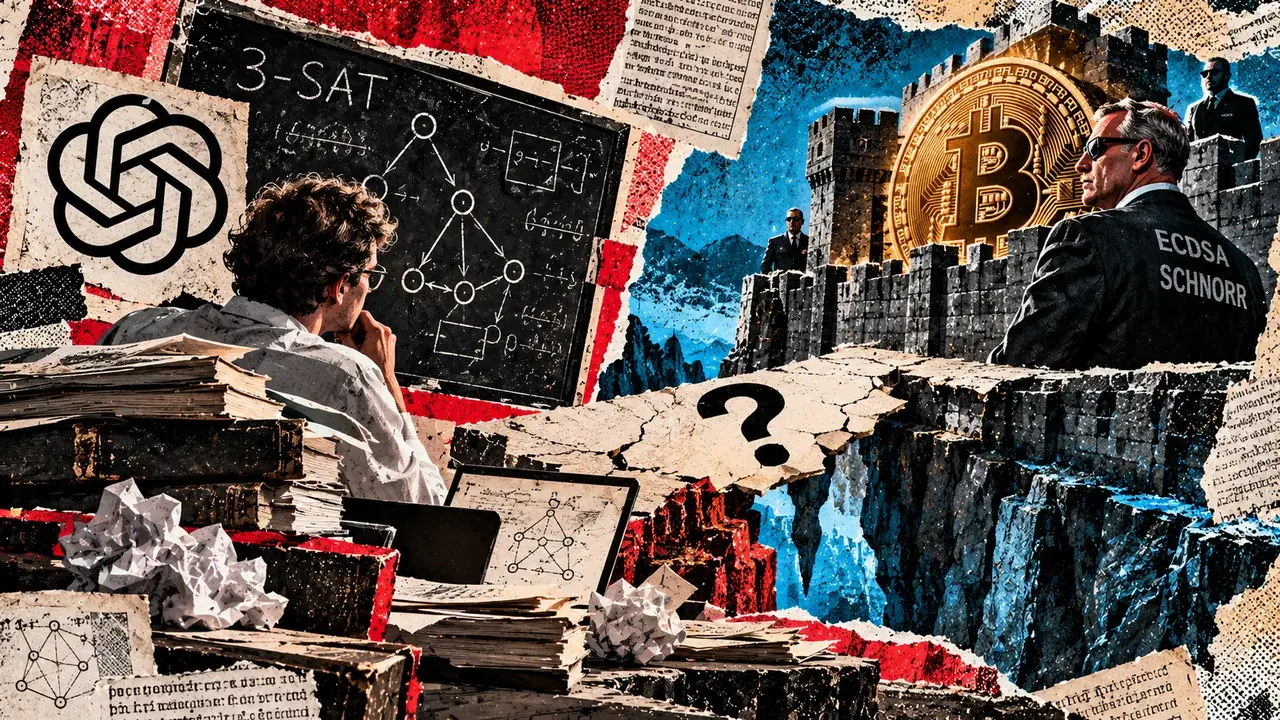
The field of computational complexity theory is currently navigating a significant disruption following an announcement by OpenAI on October 26, 2024, asserting that its researchers have refuted the Exponential Time Hypothesis (ETH). This hypothesis has long served as a foundational assumption in computer science, dictating the perceived limits of how quickly specific logical problems can be solved. While the claim suggests a monumental shift in theoretical mathematics, the disclosed results do not currently establish a viable or practical threat to the security of the Bitcoin network or other widely used cryptographic systems.
The Exponential Time Hypothesis, first formulated by Russell Impagliazzo and Mohan Paturi in 1999, posits that certain NP-complete problems—specifically the 3-satisfiability problem (3-SAT)—cannot be solved in subexponential time in the worst case. In simpler terms, the hypothesis assumes that as the number of variables in a logic puzzle increases, the time required for a computer to find a solution must grow at an exponential rate. OpenAI’s claim challenges this bedrock principle, suggesting that a more efficient deterministic algorithm exists.
Understanding the Exponential Time Hypothesis and 3-SAT
To grasp the magnitude of OpenAI’s claim, it is necessary to understand the nature of the 3-SAT problem. In computational logic, 3-SAT is a puzzle where a computer must determine if there is a way to assign "true" or "false" values to a set of variables to satisfy a series of logical clauses, where each clause contains exactly three literals. This problem is the cornerstone of NP-completeness; thousands of other complex problems in logistics, biology, and cryptography are mathematically reducible to 3-SAT.
For decades, the prevailing belief in the academic community was that no algorithm could solve every instance of 3-SAT in less than exponential time. If a problem has $n$ variables, an exponential time bound implies the difficulty scales like $2^n$. OpenAI’s manuscript, which underwent revisions on October 25, claims to have discovered a deterministic algorithm capable of counting the satisfying assignments of fixed-width Boolean formulas in subexponential time while maintaining polynomial space requirements.
Subexponential time means that while the complexity still grows as the problem size increases, it does so more slowly than any exponential function. While this is a breakthrough in theoretical efficiency, it does not necessarily translate to "fast" or "easy" computations on contemporary hardware. A subexponential algorithm can still be prohibitively slow for large-scale practical applications, a distinction that is vital for assessing the immediate risk to digital infrastructure.
Chronology of the Announcement and Academic Response
The timeline of this discovery began to surface in early October 2024, following an earlier release of mathematical tools by OpenAI. On October 7, Ethereum researcher Justin Drake expressed concerns regarding the rapid advancement of AI in solving complex mathematical proofs, suggesting that the industry might need to prepare for a "bunker mode" to protect cryptographic secrets. However, that earlier warning was speculative and did not reference a specific break in cryptographic protocols like RSA or ECDSA.
The current controversy centers on a manuscript dated October 17, with a revised version released on October 25. On October 26, OpenAI officially announced the results, noting that the proof had been partially verified using Lean, an interactive theorem prover and programming language used for formal verification of mathematical theorems.
The academic community has responded with a mixture of intense interest and rigorous skepticism. A group of prominent researchers, including Ryan Williams of MIT and the original authors of the hypothesis, Russell Impagliazzo and Mohan Paturi of the University of California, San Diego, have been tasked with organizing an independent examination of the findings. In a public letter, these researchers explicitly stated that their involvement in the review process should not be interpreted as a certification of OpenAI’s claims. They emphasized the need for a transparent, open-source audit free from non-disclosure agreements (NDAs) or financial compensation to ensure scientific integrity.
Technical Discrepancies and the Role of Lean
One of the primary points of contention among researchers is the "scope note" provided in the OpenAI GitHub repository. This note describes a time bound that appears weaker than the most aggressive claims made in the primary manuscript. Formal verification in Lean is a rigorous process, but it is limited by the specific parameters and definitions fed into the system. If the Lean proof only covers a subset of the problem or uses a different metric for complexity, the "refutation" of ETH may be more nuanced or limited than the headlines suggest.
Furthermore, the manuscript’s evidence is currently concentrated in its introductory pages (1–8). Independent experts have noted that a full review of the entire proof is required before any definitive conclusions can be drawn. The distinction between a "theoretical bound" and a "practical algorithm" is a recurring theme in the critique; even if the math holds, the constant factors involved in the subexponential algorithm might be so large that they offer no benefit over current methods for any problem size encountered in the real world.
Implications for Bitcoin and Cryptographic Security
The intersection of computational complexity and cryptocurrency often leads to concerns about the "breaking" of encryption. However, Bitcoin’s security is not a monolithic structure; it relies on two distinct mathematical pillars: mining (Proof of Work) and spending authorization (Digital Signatures).
Bitcoin Mining and Hashing Functions
Bitcoin mining involves a process where participants search for a block-header hash that falls below a specific target value. This is a search problem based on the SHA-256 cryptographic hash function. OpenAI’s claim regarding a subexponential SAT bound does not inherently provide a shortcut for mining. SAT solvers and hash functions operate on different mathematical principles. While a hash function can be represented as a SAT problem, the resulting formula is typically so massive and complex that solving it via a SAT solver is significantly less efficient than the brute-force hardware-accelerated hashing (ASICs) currently used by miners.
Digital Signatures and Key Recovery
The more sensitive area of Bitcoin security involves spending authorization, which uses the Elliptic Curve Digital Signature Algorithm (ECDSA) and Schnorr signatures over the secp256k1 curve. These systems are based on the Elliptic Curve Discrete Logarithm Problem (ECDLP).
The security of these signatures rests on the difficulty of deriving a private key from a public key. Refuting a hypothesis about worst-case 3-SAT solving does not automatically provide a mechanism to solve the discrete logarithm problem efficiently. To mount a practical attack, an adversary would need to:
- Efficiently encode the ECDLP into a SAT formula.
- Ensure the variable count and clause density are within the range where the new subexponential algorithm outperforms existing methods.
- Implement the algorithm on hardware capable of handling the memory and processing requirements.
Currently, there is no evidence that OpenAI’s result facilitates any of these steps. Ryan Williams, after communicating with OpenAI, relayed that existing cryptosystems appear to remain safe. However, this remains a second-hand assurance rather than the result of a formal cryptographic audit.
Broader Impact on Computer Science and P vs. NP
The refutation of the Exponential Time Hypothesis, if verified, would have profound implications for the P vs. NP question—one of the seven Millennium Prize Problems. While OpenAI’s disclosure does not settle P vs. NP or establish a polynomial-time algorithm for NP-complete problems, it narrows the gap.
For decades, the assumption that NP-complete problems require exponential time has been used to prove "hardness" results in other areas of computer science, such as fine-grained complexity and the hardness of approximation. If ETH is false, many of these secondary proofs may need to be re-evaluated. It could mean that certain problems previously thought to be intractable might eventually succumb to more advanced algorithmic techniques.
This event also highlights the changing landscape of mathematical discovery. The use of AI systems to assist in or generate complex proofs represents a shift in the scientific method. As AI models become more adept at formal logic and symbolic manipulation, the bottleneck shifts from "finding" a proof to "verifying" it. The reliance on tools like Lean suggests a future where human mathematicians and AI work in tandem to explore the boundaries of what is computable.
Future Outlook and Independent Scrutiny
The scientific community is now in a "wait-and-see" period. The independent organizers of the review have committed to sharing their findings as the examination progresses. OpenAI itself has maintained a cautious stance regarding practical applications, stating that significant further research is required before these theoretical improvements could lead to real-world software enhancements.
When asked about the timeline for when developers might see practical benefits from this breakthrough, Ryan Williams indicated a wide range of possibilities, from notable progress within the next 12 months to the possibility that no practical development ever emerges from this specific theoretical result.
In conclusion, while OpenAI’s announcement represents a potentially historic moment in theoretical computer science, it is not an immediate "zero-day" event for global encryption. The distinction between refuting a worst-case theoretical hypothesis and breaking a concrete, average-case cryptographic implementation is vast. For now, Bitcoin’s cryptographic foundations remain intact, even as the mathematical world prepares for a potential paradigm shift in how we understand the limits of logic and time.