admin
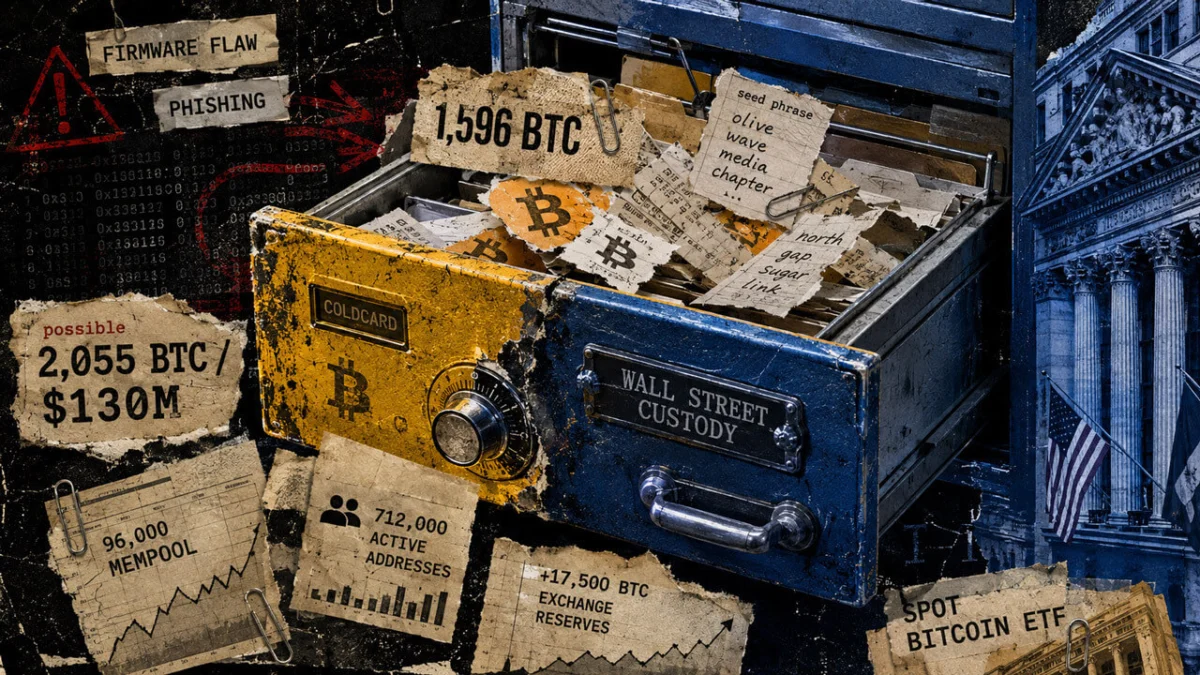
The cryptocurrency community is reeling from a significant security breach affecting the Coldcard hardware wallet, resulting in the theft of approximately 1,596 Bitcoin (BTC), valued at around $130 million USD. This sophisticated exploit, which impacted an estimated 7,300 addresses, has triggered a mass exodus of funds as users scramble to secure their digital assets, fundamentally challenging the tenets of self-custody and highlighting the inherent risks associated with relying on a single point of failure for private key generation.
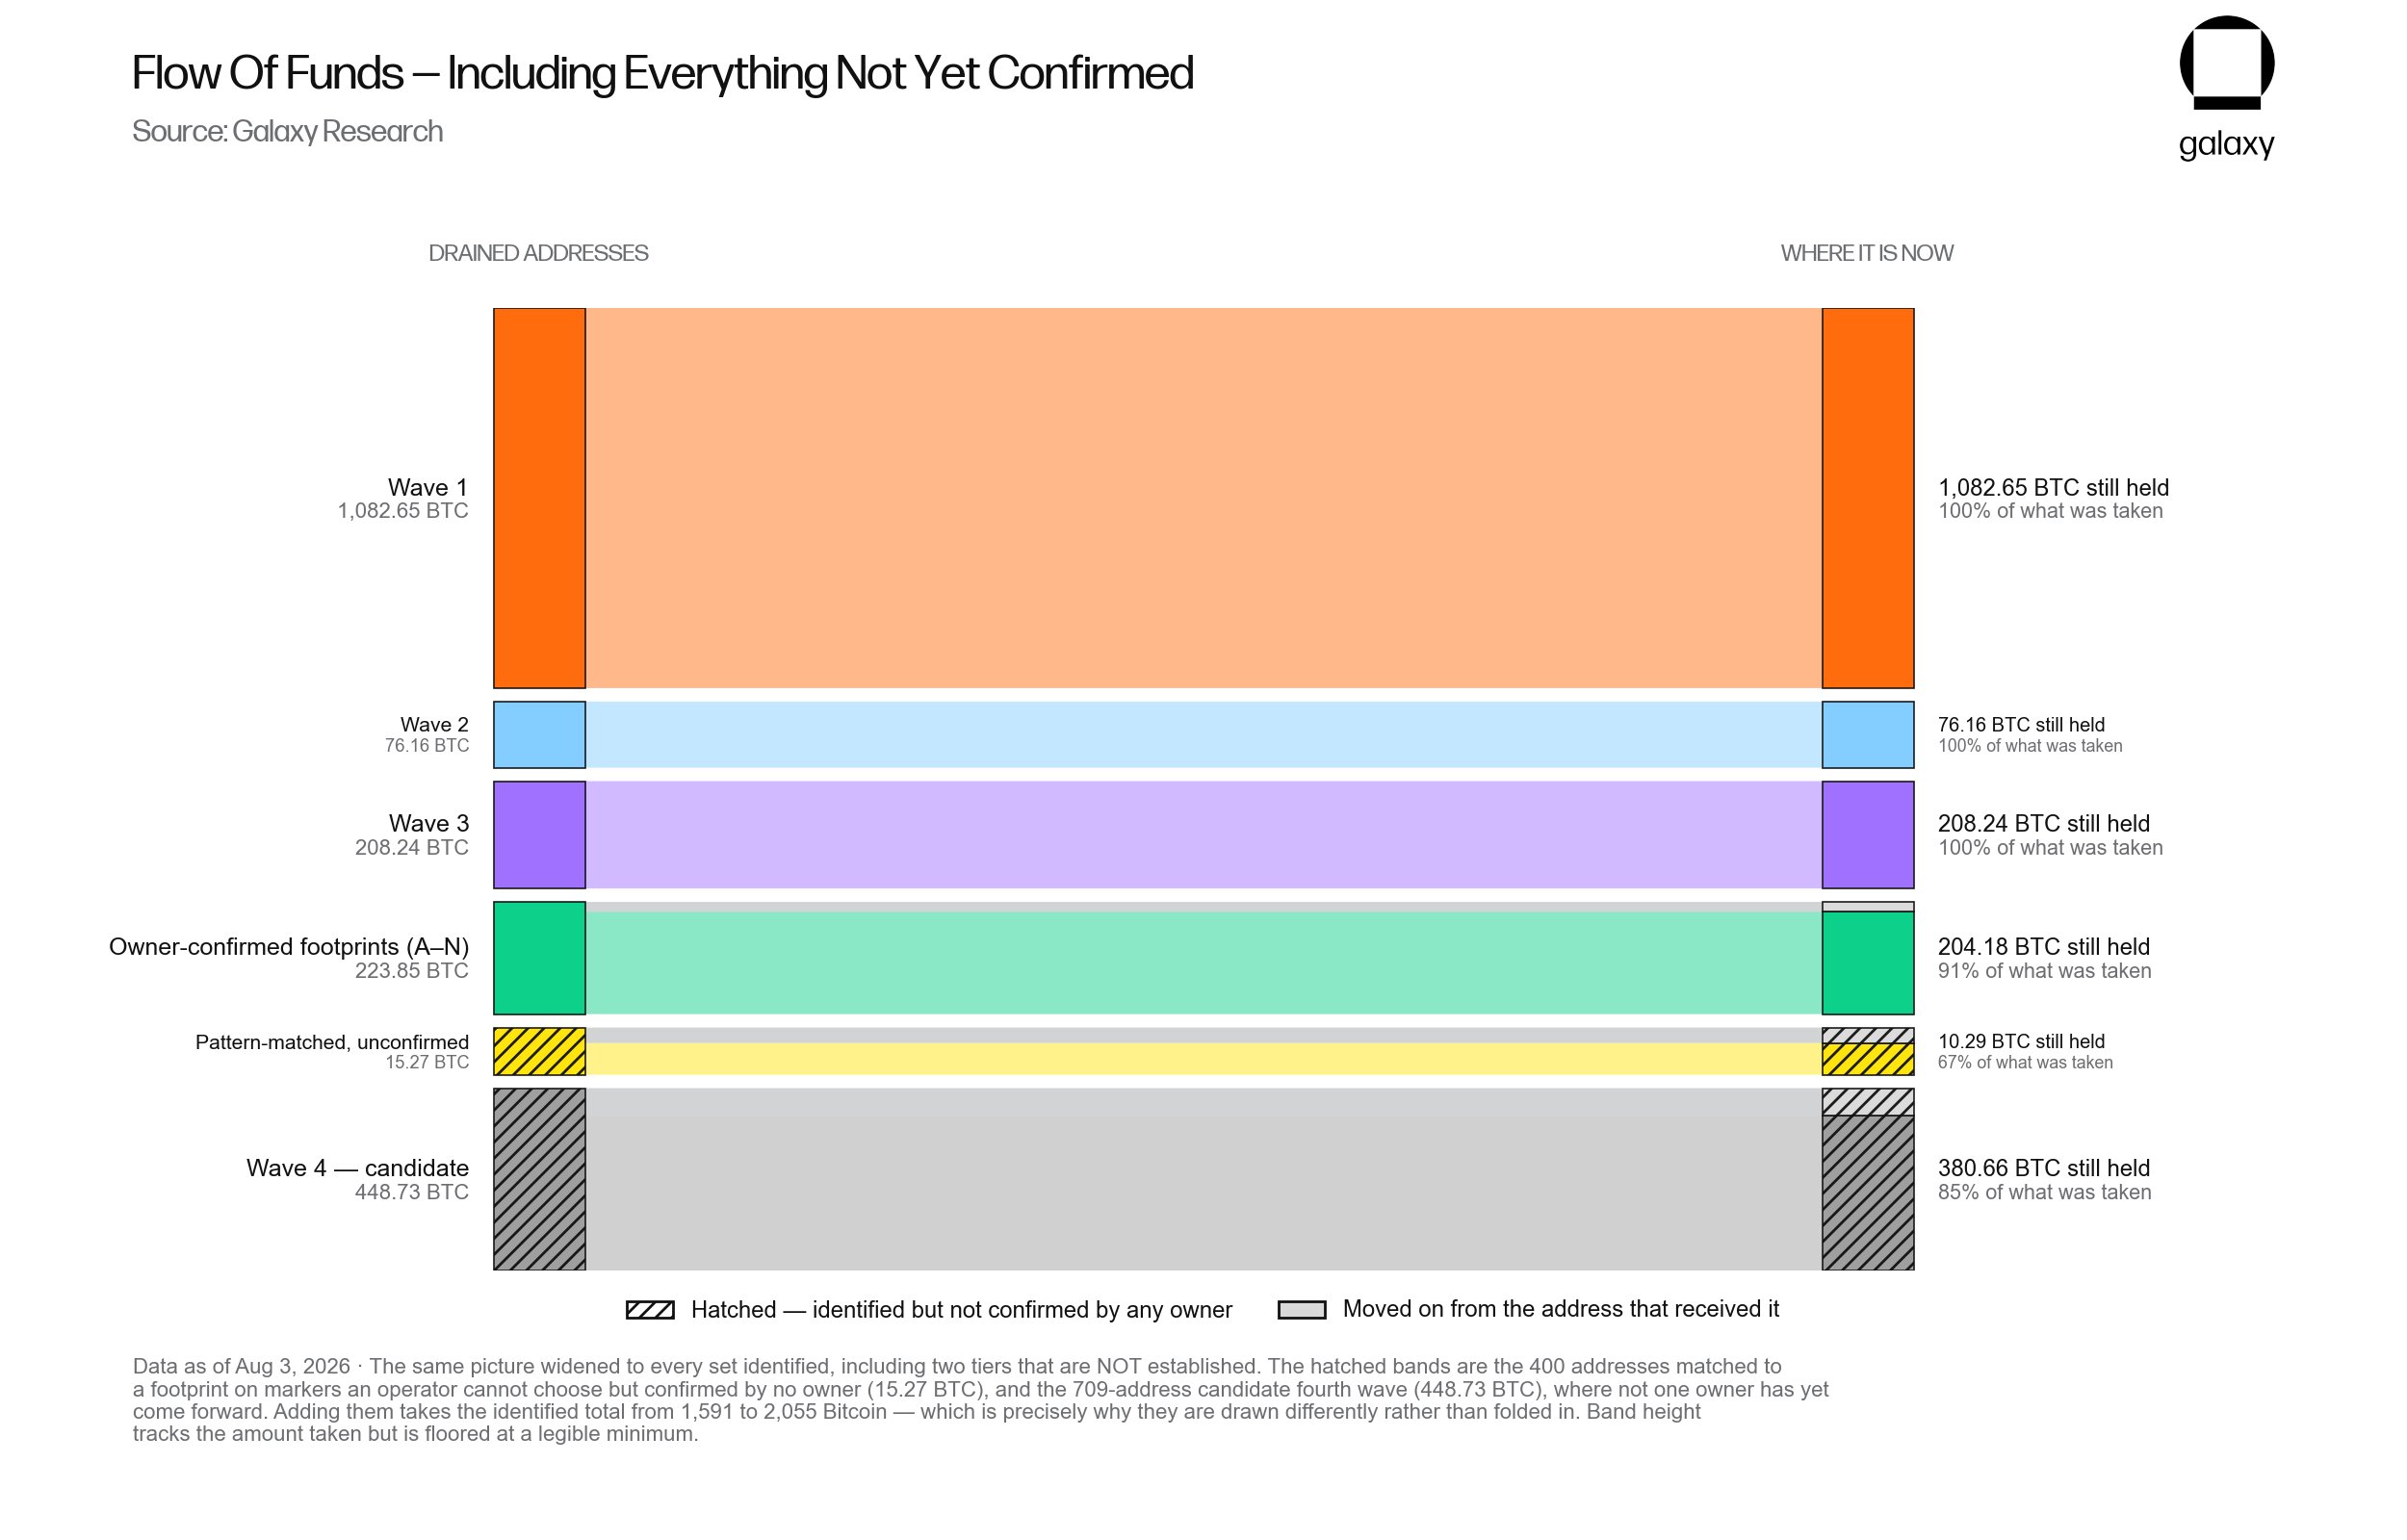
The full extent of the financial damage is still being assessed, with research firm Galaxy identifying at least three major attack waves and 14 smaller incidents that confirmed the losses. A potential fourth wave, which could push the total stolen Bitcoin to 2,055 BTC, remains under investigation pending further victim reports. This ongoing crisis has not only underscored the critical importance of robust security protocols in hardware wallets but has also reverberated across the entire Bitcoin network, causing a notable surge in transaction activity and sparking renewed debate about the safest methods for storing digital assets.
Unraveling the Coldcard Vulnerability
At the heart of this crisis lies a critical flaw within Coldcard’s firmware, dating back to March 2021. A coding error inadvertently caused certain devices to generate recovery seeds using a less secure software process. Instead of drawing sufficient randomness from the hardware’s random-number generator, the affected devices relied on a process that resulted in seeds with a significantly reduced number of possible combinations. This weakness provided a critical opening for attackers, enabling them to remotely reconstruct private keys without ever physically possessing the hardware wallet or obtaining the owner’s recovery words.
This vulnerability means that any Coldcard wallet whose recovery seed was generated using this flawed process remains exposed, even if the device itself is physically secure and the owner has never shared their recovery phrase. The manufacturer, Coinkite, has acknowledged the issue and issued urgent recommendations for users to update their firmware, generate a new recovery seed, and transfer all Bitcoin to wallets secured by these new, uncompromised phrases. However, updating the firmware only prevents the creation of additional weak seeds; it does not retroactively protect wallets whose seeds were already compromised.
The Scale of the Attack and the Hunt for Stolen Funds
Galaxy Research’s analysis indicates that approximately 90% of the stolen Bitcoin has remained in the attackers’ control, with funds linked to the initial confirmed attack waves yet to be moved. This suggests a calculated approach by the perpetrators, likely waiting for an opportune moment to liquidate their ill-gotten gains. In response to the growing number of victims, Galaxy’s head of research, Alex Thorn, has been inundated with requests for assistance in tracing the stolen Bitcoin. Over 73 victims have reportedly reached out to Thorn, providing crucial insights that have helped researchers identify additional attack patterns and estimate the number of active attackers to be at least 15.
In a proactive measure, Galaxy has shared the identified wallet addresses associated with the thefts with U.S. law enforcement agencies, cryptocurrency exchanges, and blockchain investigation firms. The aim is to flag these addresses, enabling swift action to freeze or trace any attempts by the attackers to move the funds through centralized platforms. This collaborative effort highlights the interconnected nature of the cryptocurrency ecosystem and the importance of swift information sharing in combating illicit activities.
A Network Under Pressure: Bitcoin Activity Surges
The Coldcard crisis has had a dramatic and immediate impact on the Bitcoin network itself. The urgent need for affected users to migrate their funds has driven on-chain activity to levels not seen in months, mirroring the market volatility observed during periods of significant stress, such as the FTX collapse.
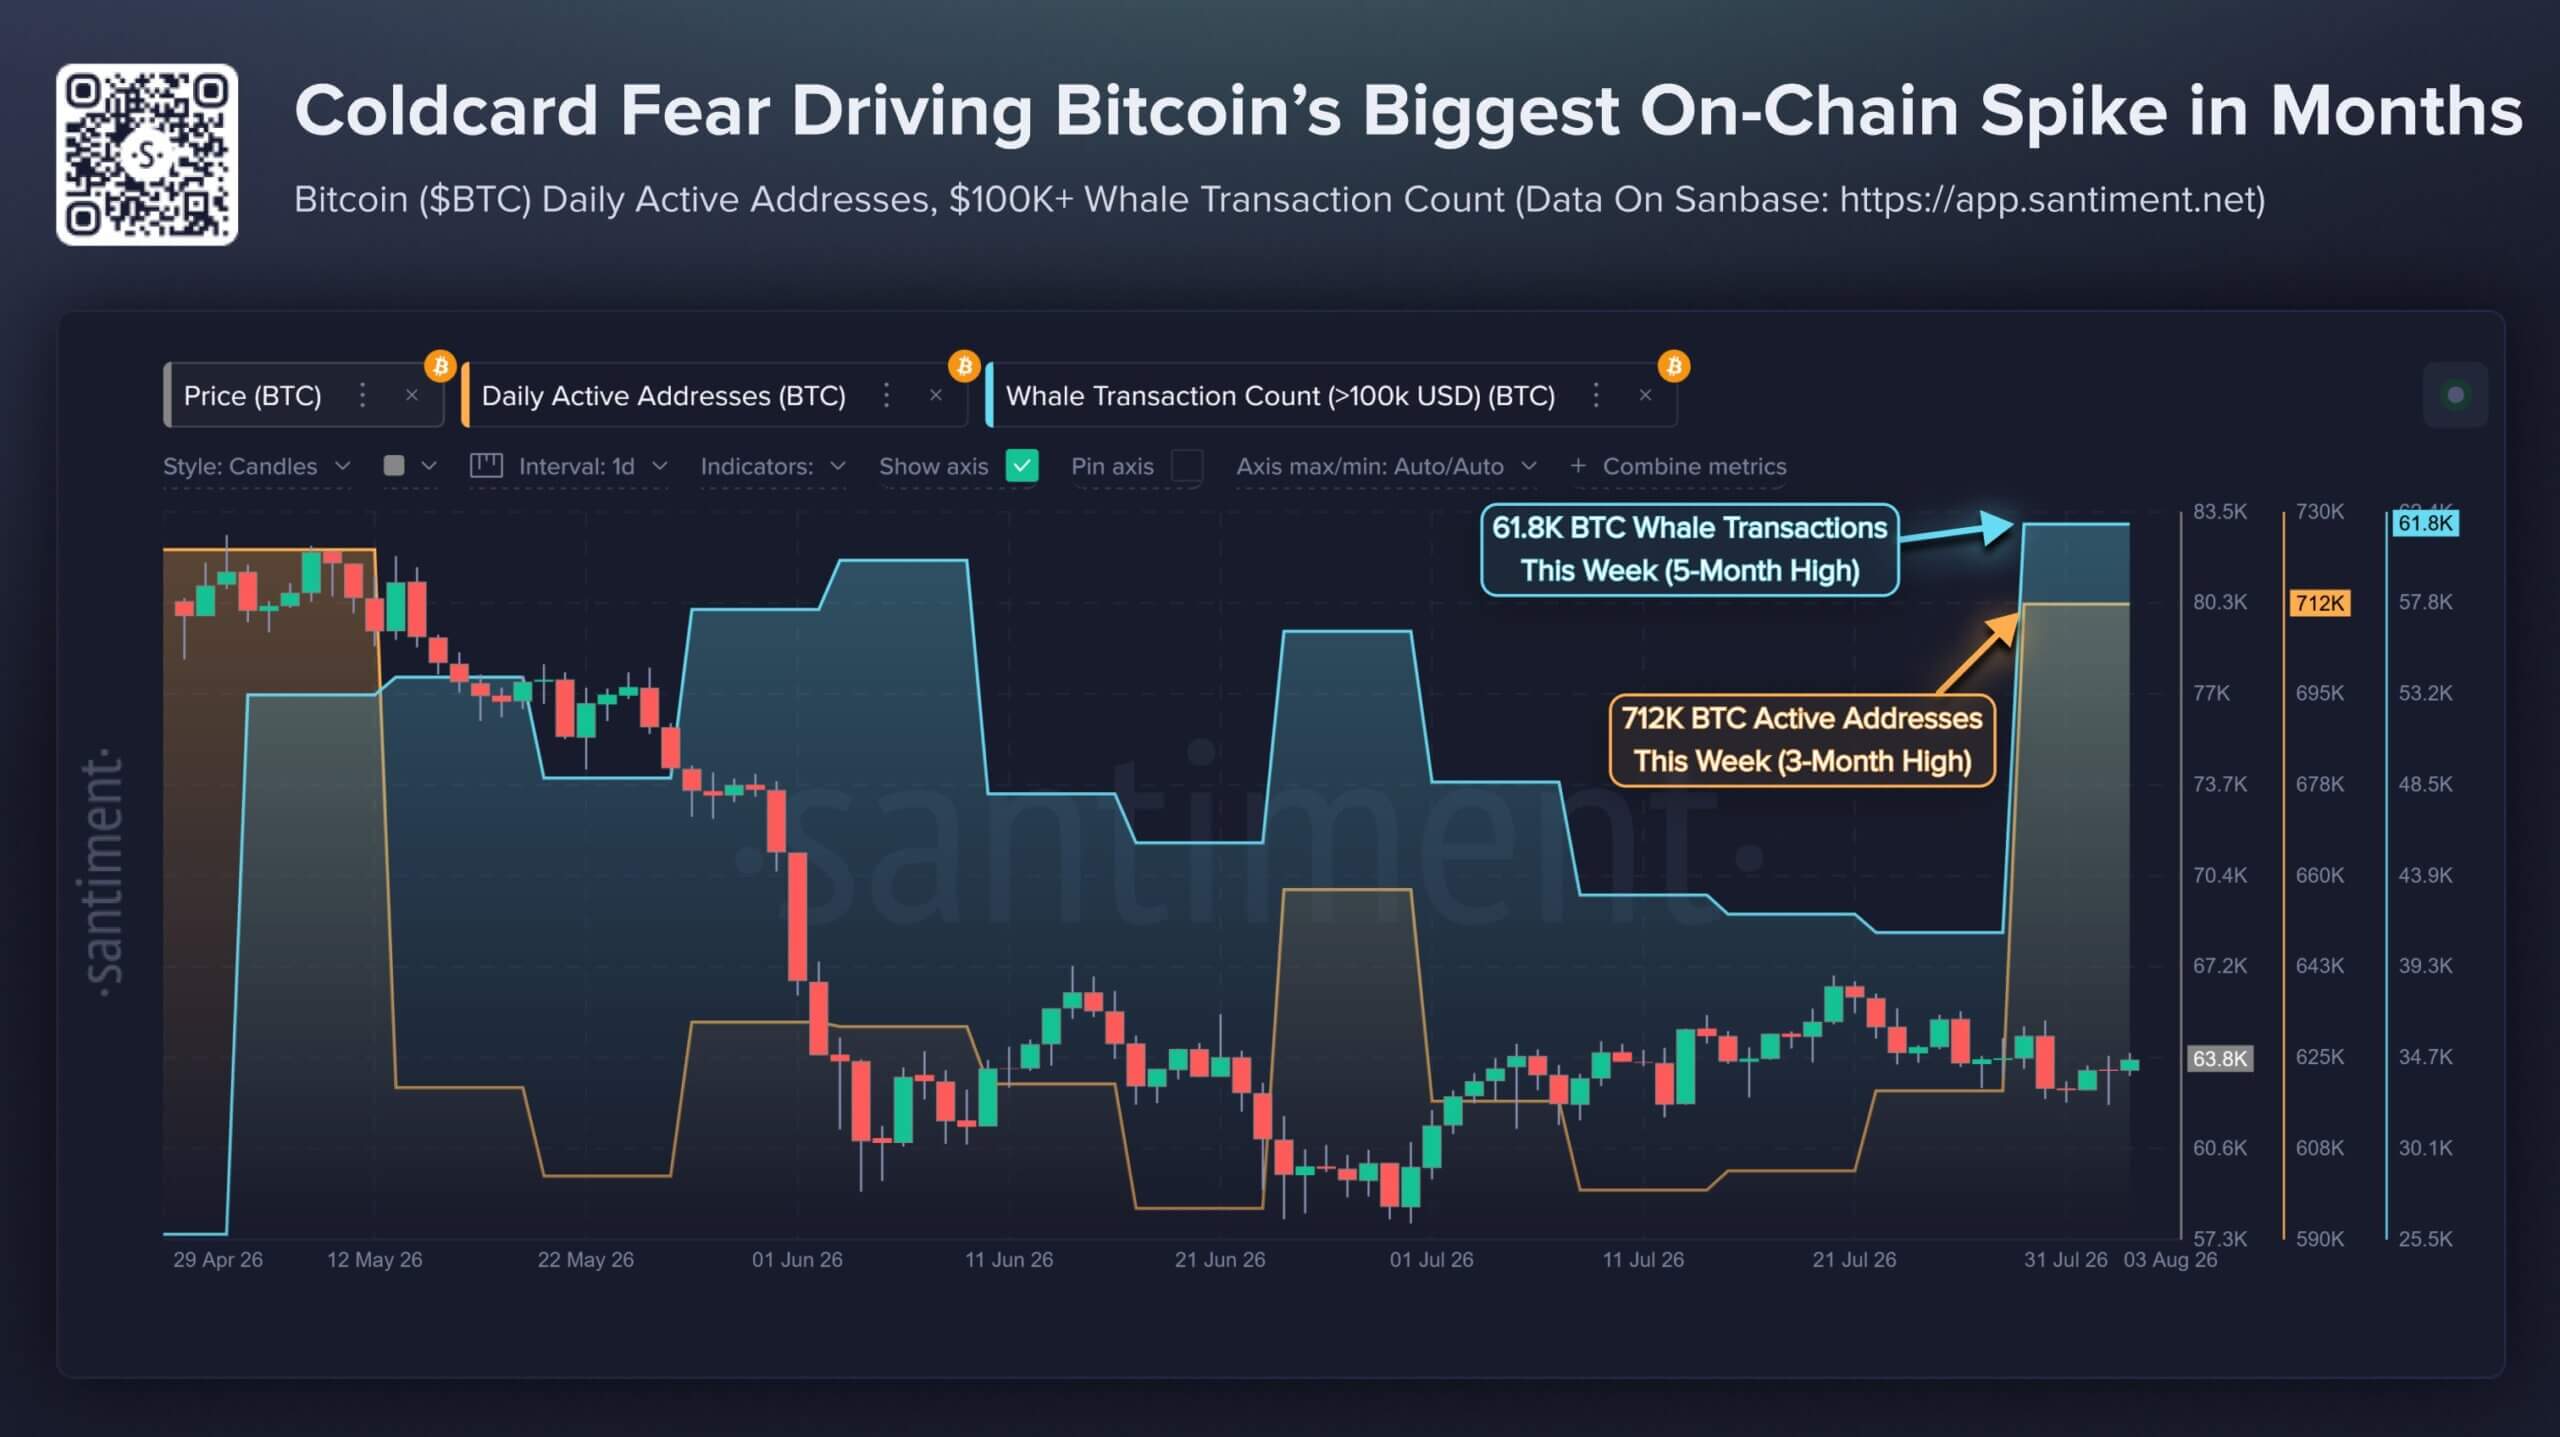
Data from Santiment reveals a surge in network activity, with 712,000 active Bitcoin addresses recorded over the past seven days, marking a three-month high. Furthermore, transactions exceeding $100,000 have reached 61,800 in the same period, a five-month peak. CryptoQuant attributes this heightened activity primarily to the Coldcard exploit, as affected users have been moving their coins to newly generated wallets, consolidating balances, or, in some cases, transferring funds to custodial platforms.
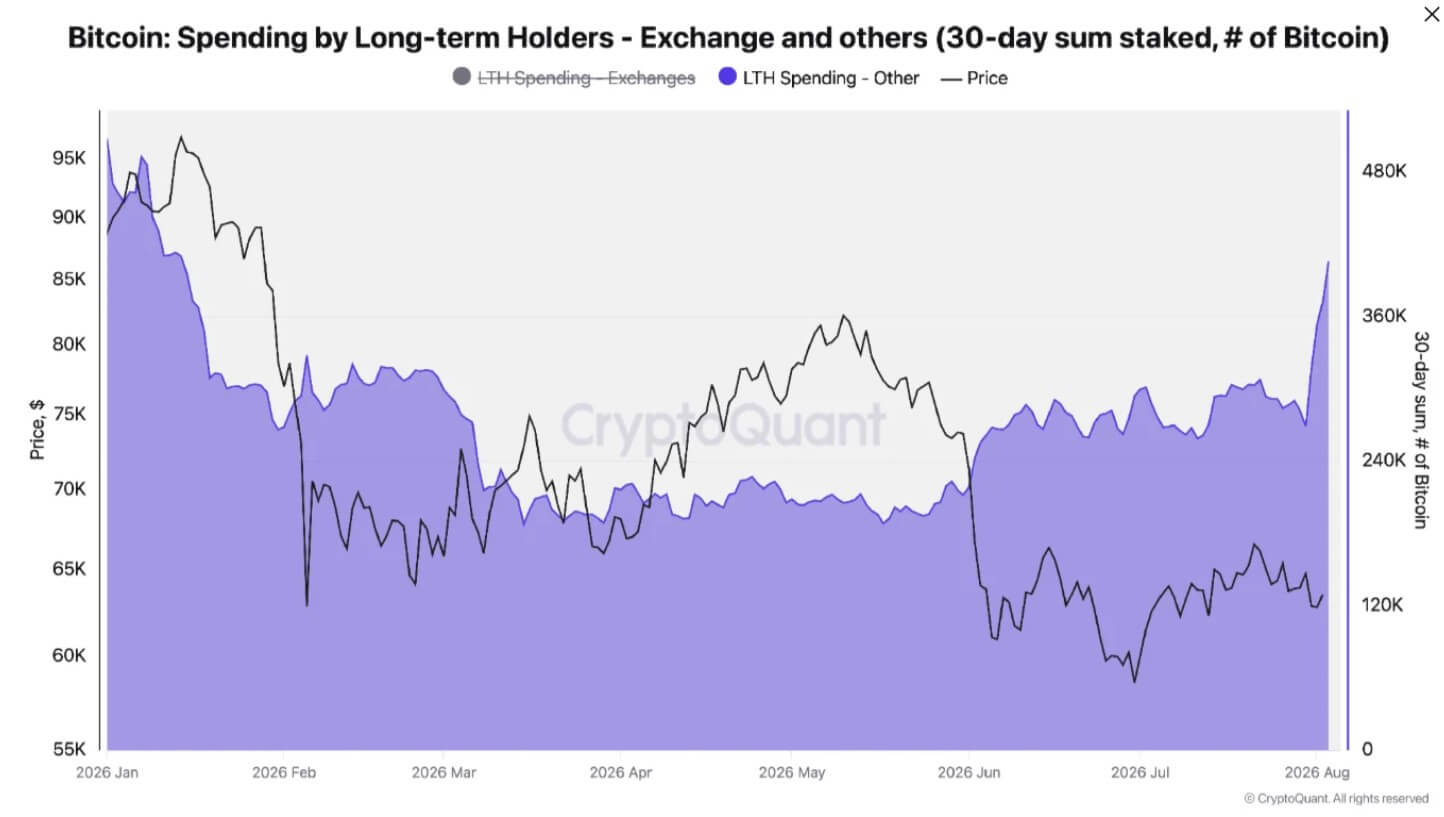
CryptoQuant’s report, shared with CryptoSlate, indicated that transactions valued below $100,000 surged to $3.2 billion, the highest volume since November 2024. This surge reflects the widespread nature of the migration, impacting a broad spectrum of Bitcoin holders. Simultaneously, the spending activity by long-term holders outside of exchanges has also seen a significant increase. As of August 3rd, this metric reached 406,000 BTC on a 30-day basis, a substantial jump from 269,000 BTC prior to the exploit and the highest level recorded since January. It is crucial to note that this increased spending does not necessarily equate to users selling their Bitcoin. Many transfers represent the movement of funds from a compromised Coldcard address to a newly secured wallet, a transaction that appears on-chain as spent Bitcoin even when ownership remains unchanged.
The sheer volume of these simultaneous transactions led to significant network congestion. The number of transactions waiting in Bitcoin’s mempool, the holding area for unconfirmed transactions, ballooned from approximately 33,000 to around 96,000, the highest level observed since June 20th. This congestion underscores the urgency felt by users attempting to secure their assets amidst the unfolding crisis.
The Rise of Phishing and the Shifting Custody Debate
As affected users diligently work to migrate their Bitcoin, they are increasingly becoming targets for opportunistic scammers. Criminals are exploiting the confusion and urgency surrounding these wallet migrations, distributing fraudulent instructions and impersonating wallet support teams. These phishing attempts aim to trick users into revealing their recovery seeds or directing their funds to malicious addresses.
Rival hardware wallet manufacturer Trezor has issued a stark warning about the surge in phishing attempts following the disclosure of the Coldcard flaw. The company has reiterated its steadfast advice to users: never share recovery seeds or enter them into websites, applications, or forms provided through unsolicited messages. Recovery words, Trezor emphasizes, should only be entered directly on a Trezor device during a wallet restoration process. Users are urged to disregard any migration instructions received via email, direct messages, or phone calls, and Trezor has confirmed that its devices are unaffected by the Coldcard incident.
This warning highlights the perilous tightrope that affected Coldcard users must walk. They must move their Bitcoin to safety before their private keys can be reconstructed by attackers, all while simultaneously evading scammers who are actively seeking to obtain their recovery words. It is critical to understand that simply importing an existing, potentially weak seed into another hardware wallet does not resolve the vulnerability. Users must generate an entirely new recovery phrase and transfer their funds to an address derived from this new, secure seed. This process is considerably more complex than a simple firmware update or a standard wallet restoration. Scammers are leveraging this complexity by directing users to fraudulent applications, requesting recovery words for supposed "security checks," or providing meticulously crafted fake addresses they claim are safe for fund transfers.
ETFs Gain Traction Amidst the Coldcard Fallout
The immediate aftermath of the Coldcard exploit has also reignited discussions surrounding the safest methods for Bitcoin custody, particularly concerning the role of regulated investment products like spot Bitcoin Exchange-Traded Funds (ETFs). While traditionally criticized by Bitcoin purists for not offering direct control over private keys, the increased perceived risk associated with hardware wallets has begun to shift perspectives.
Eric Balchunas, a Senior ETF Analyst at Bloomberg Intelligence, suggested that the Coldcard breach could indeed prompt some investors, including those who have historically favored self-custody, to consider migrating their assets to spot Bitcoin ETFs. The argument is that while ETFs rely on institutional custodians to hold the underlying assets, these custodians are large, established financial institutions with extensive experience in safeguarding client assets. This contrasts with smaller hardware wallet manufacturers, which, as demonstrated by the Coldcard incident, may not always possess the same level of robust security infrastructure.
The structure of an ETF, where assets are held by institutional custodians on behalf of the fund, may now appear more appealing when juxtaposed with the risks associated with a single hardware wallet manufacturer experiencing a significant vulnerability. While institutional custody does not eliminate the possibility of theft or operational failure, Balchunas notes that a successful attack on an ETF custodian would likely trigger an immediate and thorough regulatory investigation, coupled with a coordinated response involving the fund manager, custodian, and law enforcement agencies.
It is important to note that there is currently no direct evidence linking users purchasing ETF shares as a direct consequence of the Coldcard exploit. Similarly, the observed increase in deposits to centralized exchanges might prove to be a temporary measure as users secure new wallets and potentially return to self-custody. However, the breach has undeniably altered the risk-reward calculation for investors determining the safest place to store their Bitcoin. While self-custody offers independence from intermediaries, it places the full responsibility for hardware and software security squarely on the user. For those now navigating the complex and potentially dangerous path of escaping compromised seeds while fending off phishing attacks, the institutional framework of ETFs, once viewed with skepticism, may now present a more accessible and arguably simpler solution. The Coldcard crisis serves as a potent reminder that in the rapidly evolving world of digital assets, security is a multifaceted challenge requiring constant vigilance and a clear understanding of the inherent risks at every level.