admin
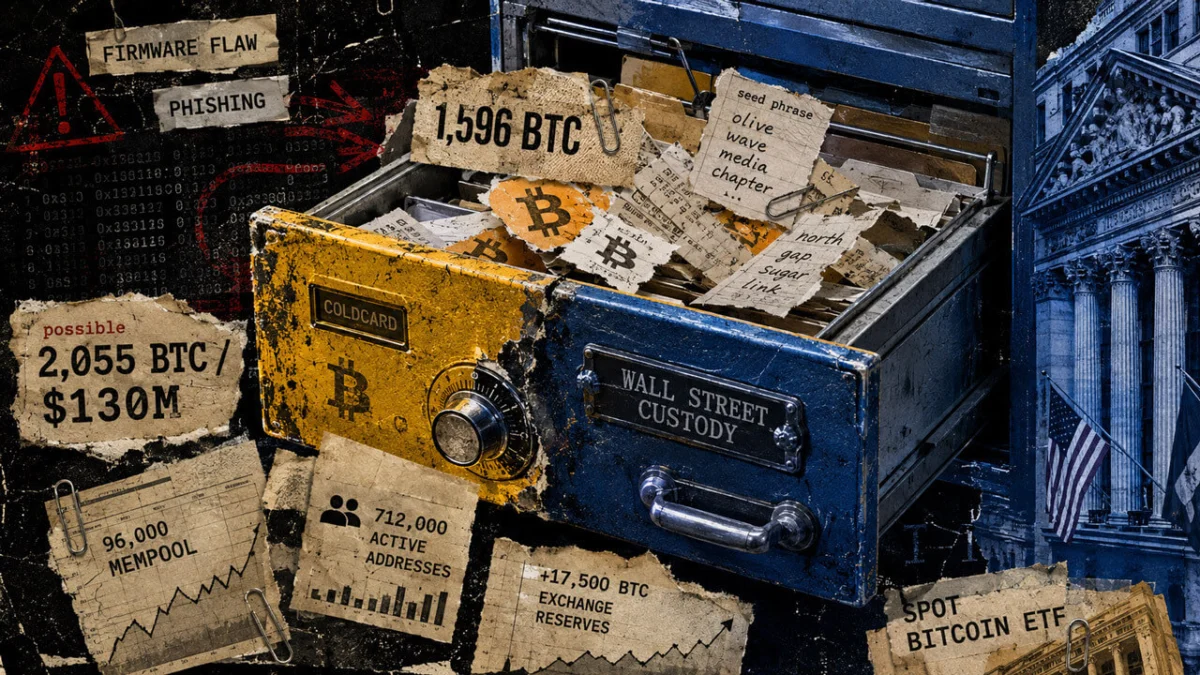
The cryptocurrency landscape has been shaken by a significant exploit affecting Coldcard hardware wallets, a popular choice for users prioritizing self-custody of their Bitcoin. Preliminary reports indicate that at least 1,596 Bitcoin (BTC), valued at approximately $130 million, has been stolen from around 7,300 addresses. This incident underscores the inherent risks associated with relying on single devices for private key generation and has triggered a massive migration of funds across the Bitcoin network, pushing on-chain activity to multi-month highs.
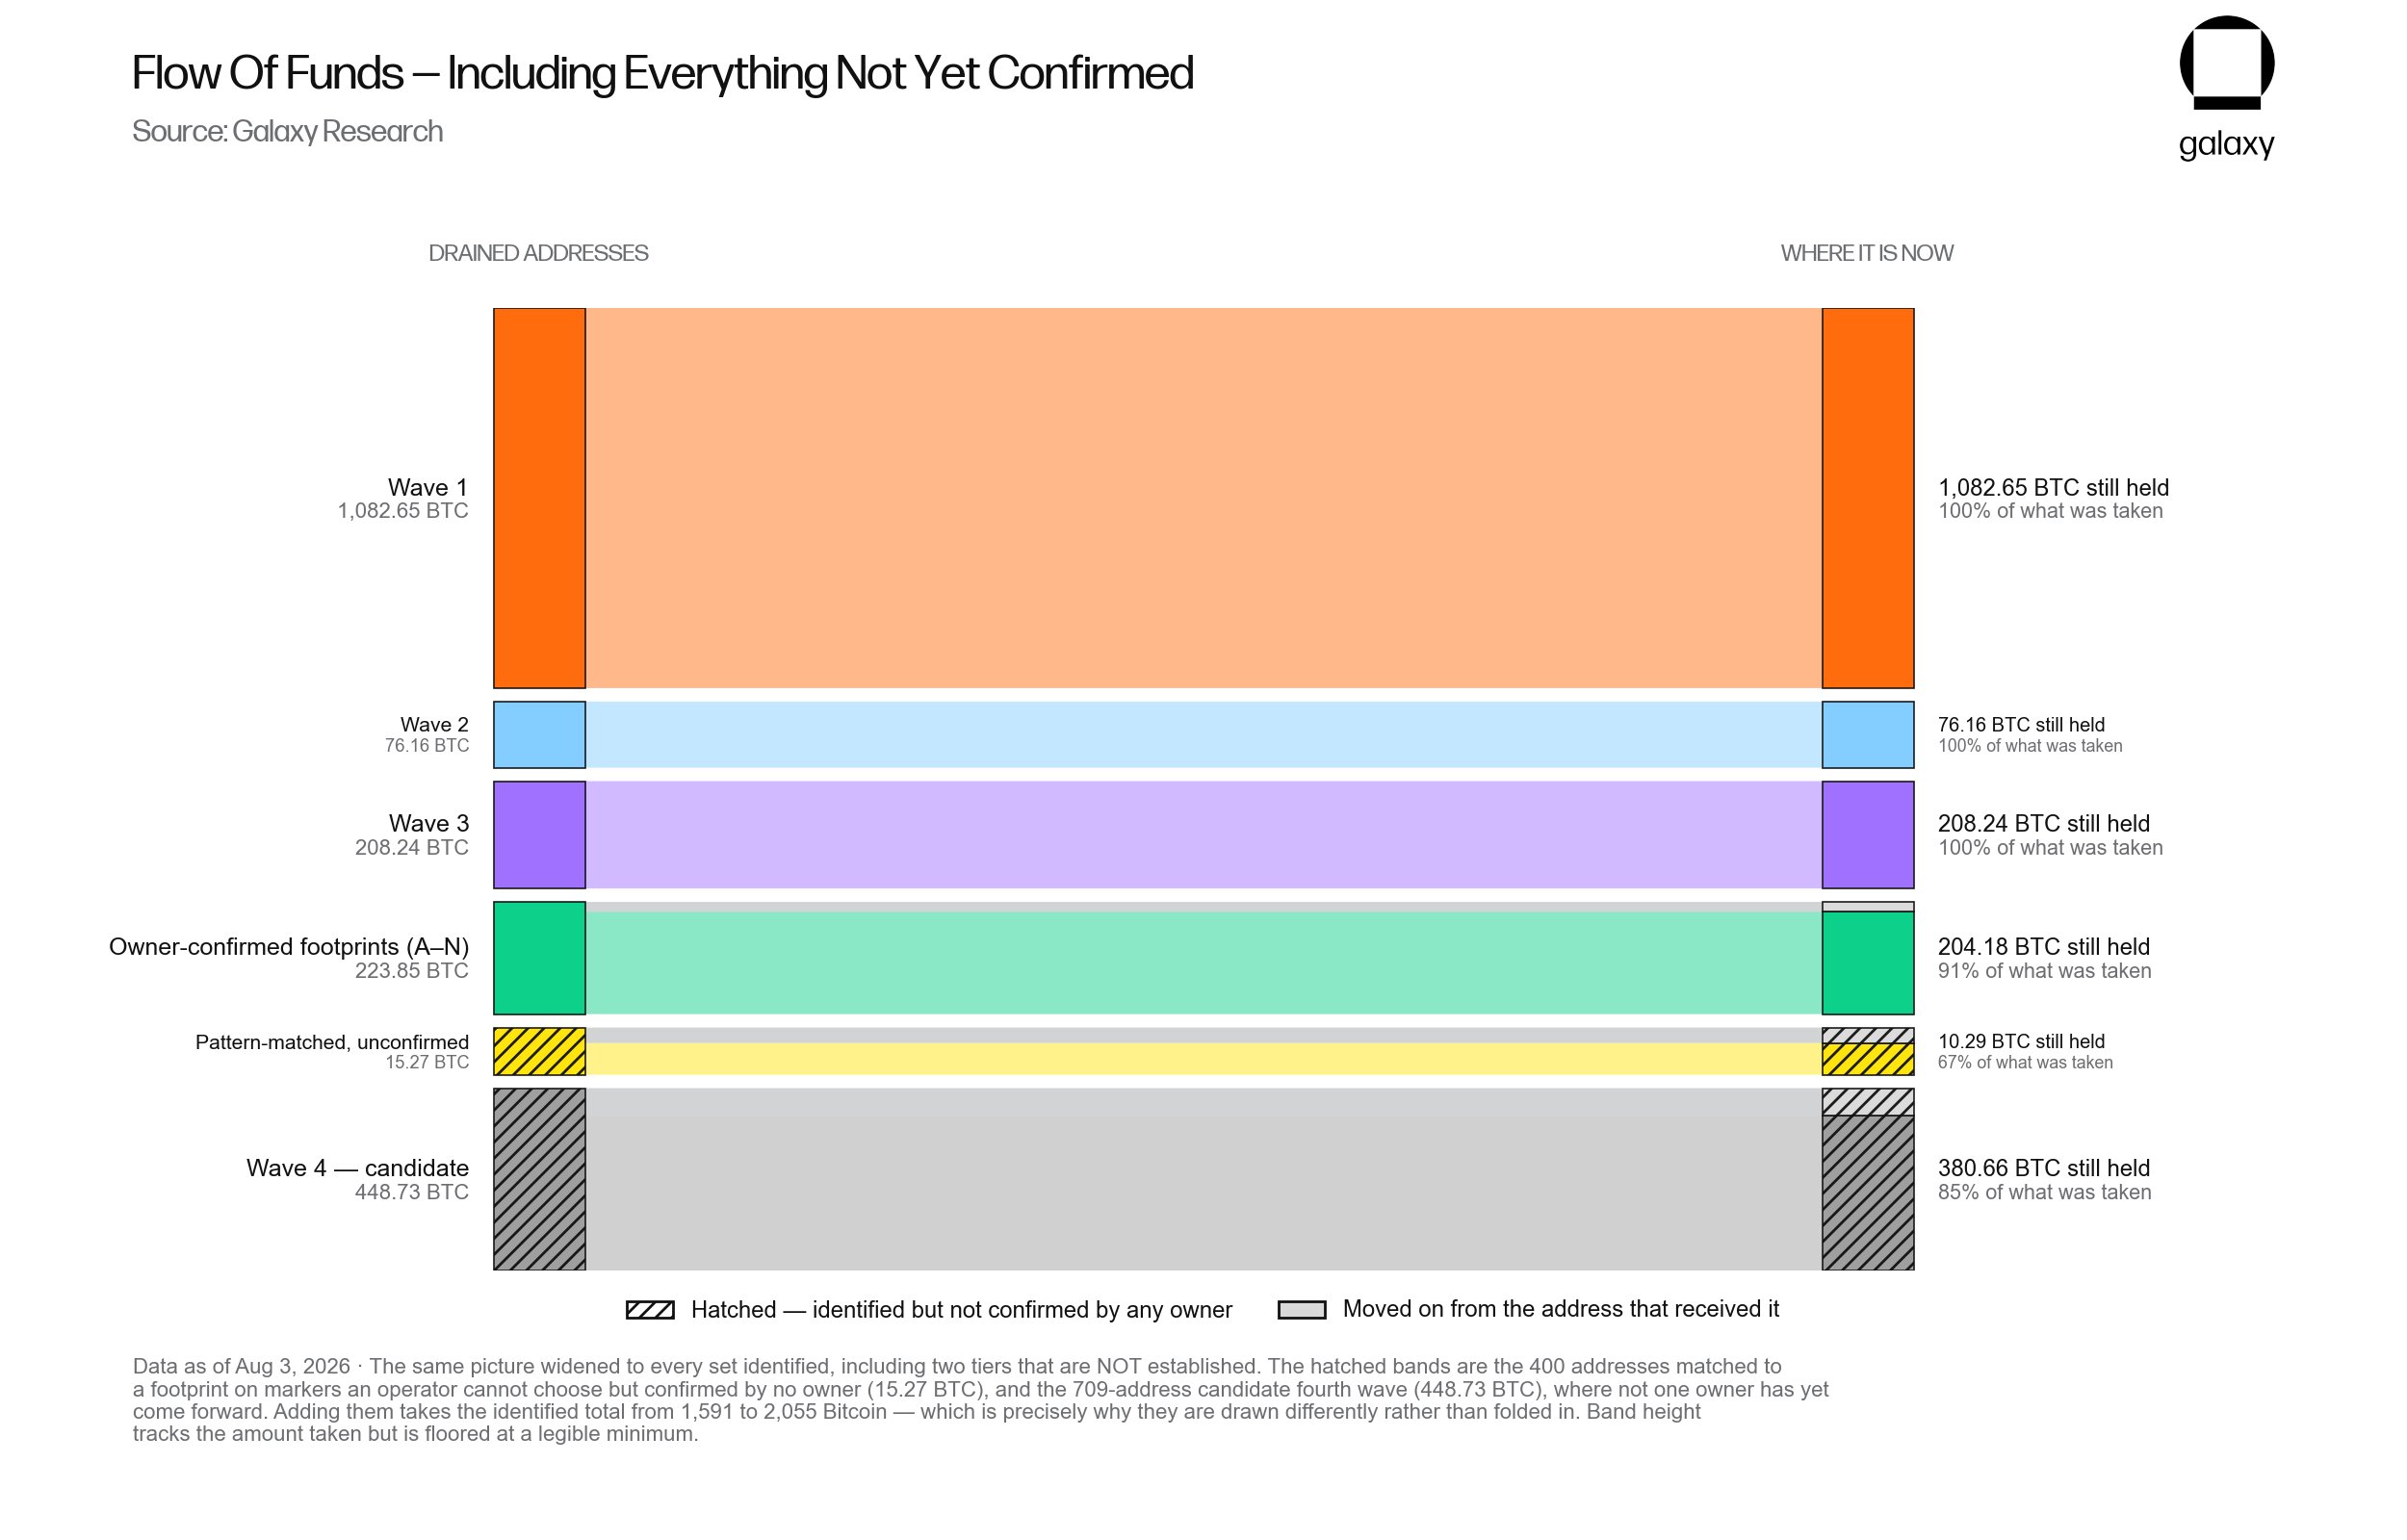
The ongoing fallout from the Coldcard vulnerability has prompted widespread concern among Bitcoin holders. Research from Galaxy, a prominent cryptocurrency investment firm, has identified at least three major attack waves and 14 smaller incidents directly linked to the exploit. These confirmed losses account for the substantial sum of stolen Bitcoin. Galaxy Research has also flagged a potential fourth wave of attacks, which, if confirmed, could escalate the total losses to 2,055 BTC, pushing the estimated value closer to $130 million. However, these addresses remain outside the confirmed loss tally pending further victim reports and detailed analysis.
Timeline of the Coldcard Crisis
The roots of this crisis trace back to a subtle but critical flaw within the Coldcard firmware, with the coding error dating back to March 2021. This vulnerability allowed certain Coldcard devices to generate recovery seeds using a less secure software process. Instead of drawing sufficient randomness from the hardware’s dedicated random-number generator, the flawed process resulted in seeds with a significantly reduced number of possible combinations. This weakness enabled attackers to remotely reconstruct private keys without ever needing physical access to the device or the owner’s recovery phrase.
While Coinkite, the manufacturer of Coldcard, has released a security update that prevents the creation of additional weak seeds, it does not offer protection for wallets whose recovery phrases were already generated under the flawed process. This means that any user whose device was affected prior to the firmware update remains exposed until their funds are moved to a new, securely generated wallet.
The first confirmed attack waves began to emerge, prompting early victim reports. Galaxy Research’s head of research, Alex Thorn, has been actively assisting at least 73 victims in tracing their stolen Bitcoin. These personal accounts have been instrumental in helping researchers identify distinct attack patterns and conclude that as many as 15 attackers may be actively exploiting this vulnerability.
The Scale of the Losses and Recovery Efforts
The confirmed losses paint a stark picture of the exploit’s impact. The vast majority of the stolen Bitcoin, approximately 90%, has not yet been moved by the attackers. Crucially, all coins associated with the initial three confirmed attack waves remain in the attacker-controlled addresses, suggesting a degree of confidence or a planned strategy on the part of the perpetrators.
In response to the growing threat, Galaxy has proactively shared the identified addresses of compromised funds with U.S. law enforcement agencies, major cryptocurrency exchanges, and specialized blockchain investigation firms. This collaborative effort aims to flag any attempts by the attackers to move the stolen Bitcoin through centralized platforms, thereby increasing the likelihood of asset recovery or seizure.
Network Activity Skyrockets Amidst Migration
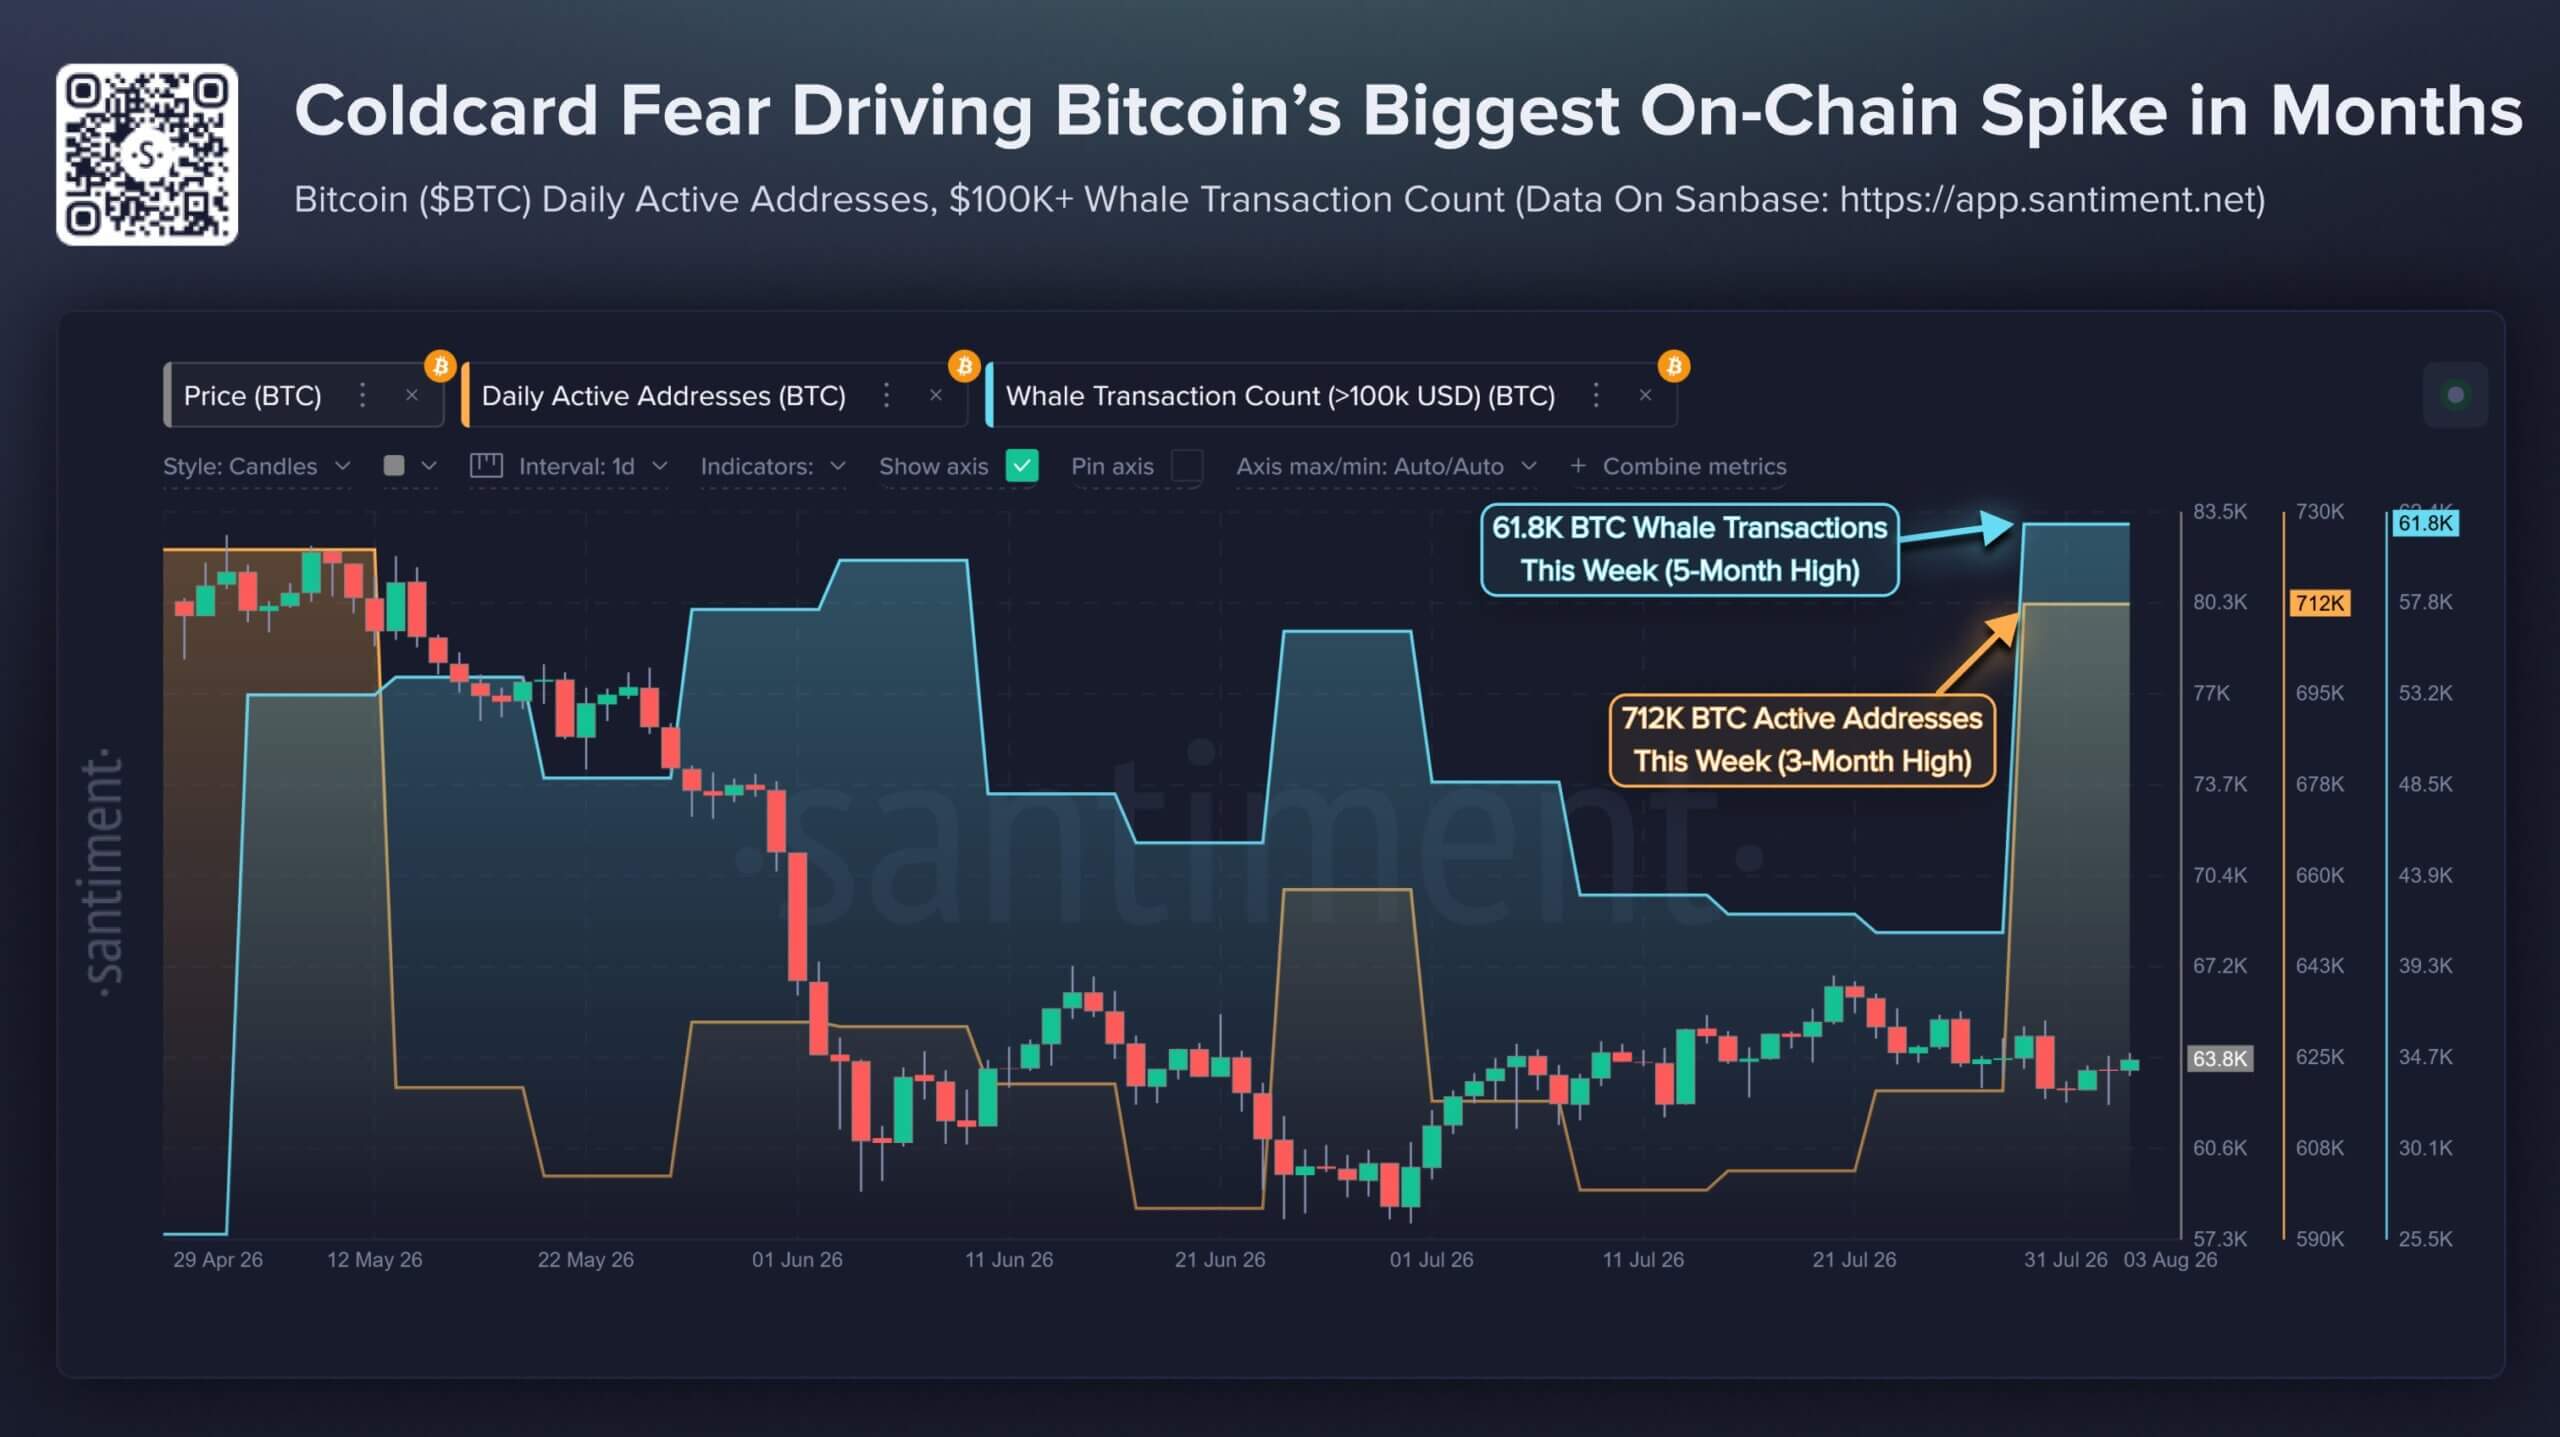
The urgency to secure funds has precipitated a dramatic surge in activity across the entire Bitcoin network. Data from Santiment reveals a significant uptick in the number of active Bitcoin addresses, reaching 712,000 over the past seven days, a three-month high. Similarly, transactions exceeding $100,000 in value have surged to 61,800 in the same period, marking a five-month peak.
CryptoQuant, a leading on-chain analytics firm, has identified the Coldcard crisis as the primary driver behind this heightened network activity. Affected users are actively migrating their coins into newly generated, secure wallets, consolidating their balances, or, in some cases, transferring funds to custodial platforms.
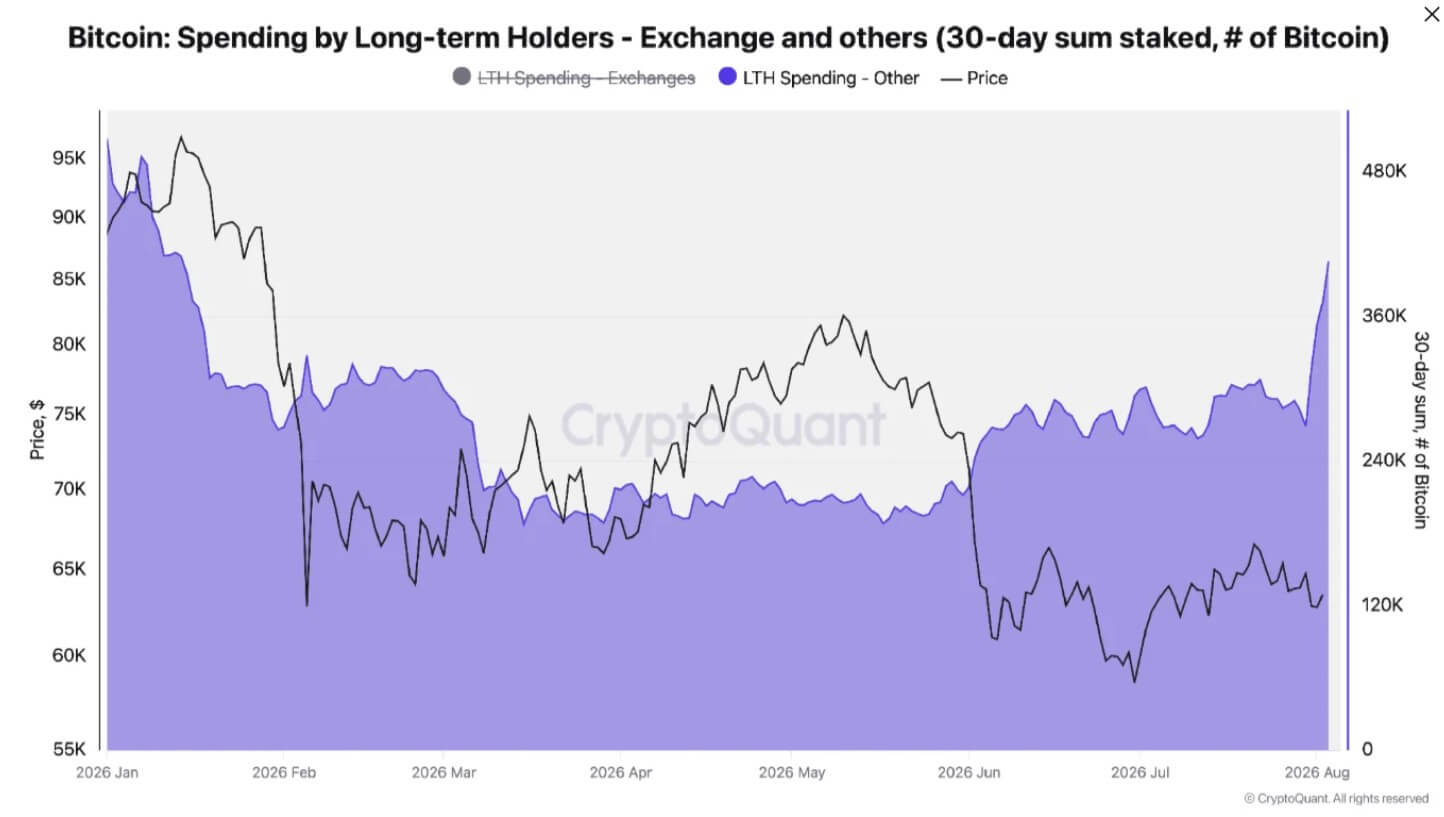
A report shared by CryptoQuant with CryptoSlate highlighted that transactions valued below $100,000 have reached $3.2 billion, the highest volume since November 2024. This indicates a broad-based movement of funds, affecting both large and small holders. Furthermore, spending by long-term Bitcoin holders outside of exchanges has seen a substantial increase, rising to 406,000 BTC on a 30-day basis as of August 3rd. This figure represents a significant jump from 269,000 BTC prior to the exploit and is the highest recorded level since January, suggesting that even long-term investors are taking action to secure their assets.
It is important to note that this surge in "spending" by long-term holders does not necessarily imply they are selling their Bitcoin. A transfer from a compromised Coldcard address to a newly established secure wallet is recorded on the blockchain as a spent transaction, even if the ultimate ownership of the funds remains unchanged.
The sheer volume of these simultaneous transactions led to network congestion. The number of transactions waiting in Bitcoin’s mempool, the holding area for unconfirmed transactions, ballooned from approximately 33,000 to around 96,000, reaching its highest point since June 20th. This illustrates the immense pressure placed on the network as thousands of users attempted to move their funds concurrently.
Exchange Inflows and the Rise of Phishing Scams
A portion of the Bitcoin migration has found its way into centralized exchanges, providing users with an immediate destination for funds removed from vulnerable wallets. CryptoQuant data indicates that deposits from smaller holders have reached their highest levels since February 6th. This suggests that some users are opting for temporary custody on exchanges while they assess their options for establishing new self-custody solutions or potentially switching hardware providers.
Between July 28th and August 3rd, total exchange reserves saw an increase of approximately 17,500 BTC, rising from around 2.702 million BTC to 2.719 million BTC. Binance, in particular, absorbed a significant portion of this influx, with its reserves climbing by approximately 9,000 BTC to 659,000 BTC, accounting for roughly 51% of the net increase.
While these inflows contribute to increased Bitcoin availability for trading and could potentially exert short-term selling pressure, they do not definitively indicate an intention to sell. As previously mentioned, these deposits might represent temporary arrangements as users secure their assets and re-evaluate their long-term storage strategies.
Concurrently, the urgency to migrate has created fertile ground for malicious actors. Criminals are actively distributing fraudulent migration instructions and impersonating wallet support teams to trick users into divulging their sensitive recovery information. Trezor, a competitor in the hardware wallet market, has issued a stark warning about the surge in phishing attempts following the disclosure of the Coldcard flaw.
Trezor has strongly advised its users to never share their recovery seeds or enter them into websites, applications, or forms received through unsolicited messages. The company emphasizes that recovery words should only be entered directly onto a Trezor device during the wallet restoration process. They further urge users to disregard any migration instructions received via email, messages, or phone calls, and have confirmed that their devices are unaffected by the Coldcard incident.
This warning highlights the precarious position of affected Coldcard users. They are under immense pressure to move their Bitcoin before private keys can be reconstructed by attackers, all while navigating a landscape rife with scammers attempting to acquire recovery words directly. It is critical to understand that simply importing an existing, compromised seed phrase into another device does not resolve the vulnerability. Users must generate an entirely new recovery phrase and transfer their funds to an address derived from this secure phrase, a process considerably more complex than a standard firmware update or wallet restoration. Scammers are exploiting this complexity by directing users to fake applications, demanding recovery words under the guise of security checks, or providing fraudulent addresses they claim are secure.
The Custody Debate and the Rise of ETFs
The ongoing turmoil surrounding hardware wallet security and the increasing risks associated with wallet migrations are reigniting a long-standing debate within the Bitcoin community: the merits of self-custody versus regulated investment products. The movement of funds towards centralized exchanges and the heightened threat of scams during migration processes are bolstering the argument for holding Bitcoin through regulated investment vehicles like spot Bitcoin Exchange-Traded Funds (ETFs).
Eric Balchunas, a senior ETF analyst at Bloomberg Intelligence, has suggested that the Coldcard breach could prompt some investors, including those who have historically prioritized self-custody, to consider migrating towards spot Bitcoin ETFs. Traditionally, Bitcoin enthusiasts have viewed ETFs with skepticism, arguing that investors in these products do not directly control the underlying coins or private keys. Instead, institutional custodians hold these assets on behalf of the funds.
However, Balchunas posits that this arrangement may now appear more attractive when contrasted with the perceived risks of relying on a smaller hardware wallet manufacturer. ETF issuers and their custodians are typically large financial institutions with extensive experience in safeguarding client assets over decades. In contrast, Coldcard is operated by a comparatively smaller Canadian company with a limited workforce.
While institutional custody does not eliminate the possibility of theft or operational failure, Balchunas suggests that a successful attack on an ETF custodian would likely trigger an immediate and comprehensive regulatory investigation. Such an event would involve a coordinated response from the fund manager, the custodian, and law enforcement agencies, offering a different level of recourse and oversight compared to individual hardware wallet exploits.
Currently, there is no direct evidence to suggest that Coldcard users have specifically purchased ETF shares as a direct consequence of this exploit. Furthermore, the increased deposits into exchanges may prove to be a temporary trend as users establish new, secure wallets and potentially return to self-custody.
Nevertheless, the Coldcard breach has undeniably altered the risk calculus for investors deciding on the safest place to hold their Bitcoin. Self-custody offers independence from banks, exchanges, or fund managers but places the full responsibility for the security of hardware and software responsible for private key generation squarely on the user. For those now navigating the perilous journey of escaping compromised seeds while simultaneously fending off phishing attacks, the institutional structure of ETFs, once criticized for aligning Bitcoin with traditional Wall Street finance, may now present a more straightforward and potentially safer alternative. The incident serves as a potent reminder that in the realm of digital assets, security is paramount, and the "not your keys, not your coins" mantra carries with it the profound responsibility of safeguarding those keys with utmost diligence.