admin
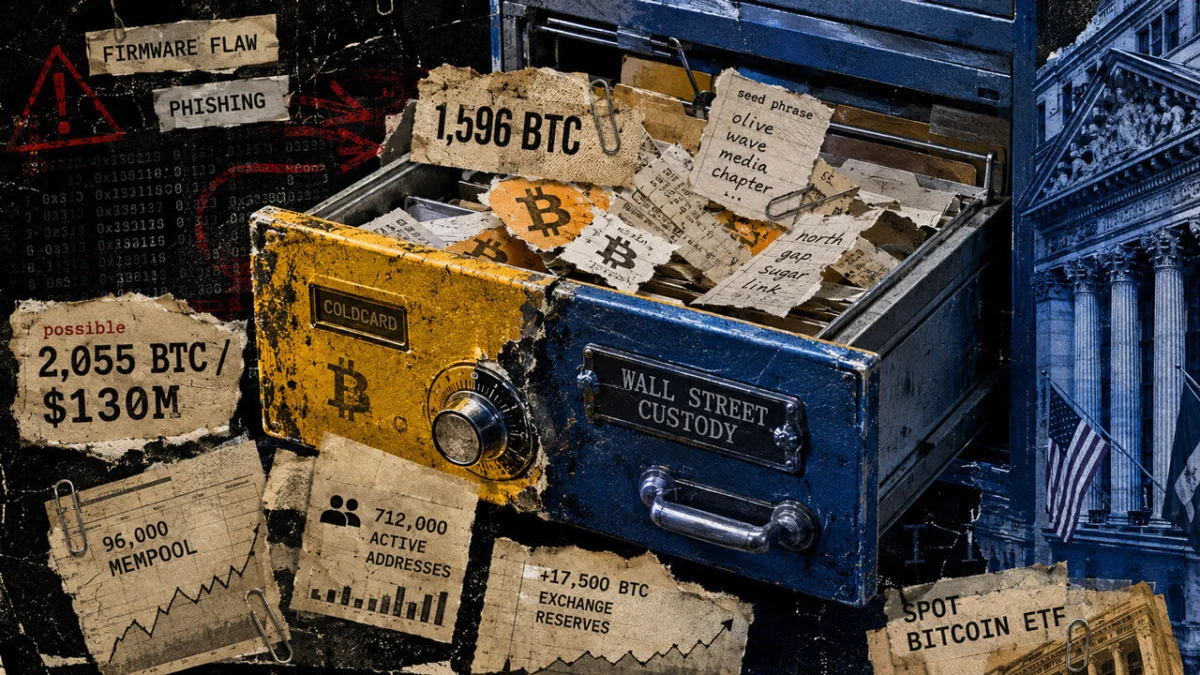
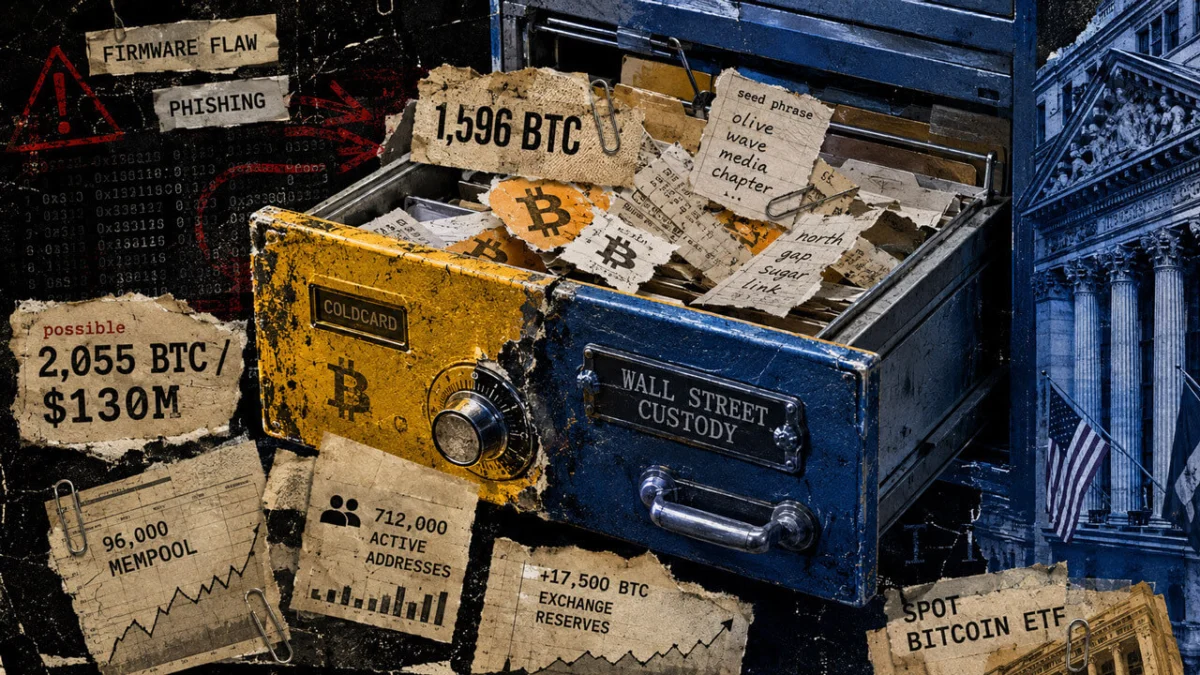
The security vulnerability affecting Coldcard hardware wallets has resulted in the estimated theft of approximately 1,596 Bitcoin (BTC), valued at around $130 million, impacting an estimated 7,300 addresses. As users grapple with the implications of this exploit, a significant wave of fund movements is being observed across the Bitcoin network, highlighting the critical importance of secure private key generation and the complex trade-offs in cryptocurrency custody.
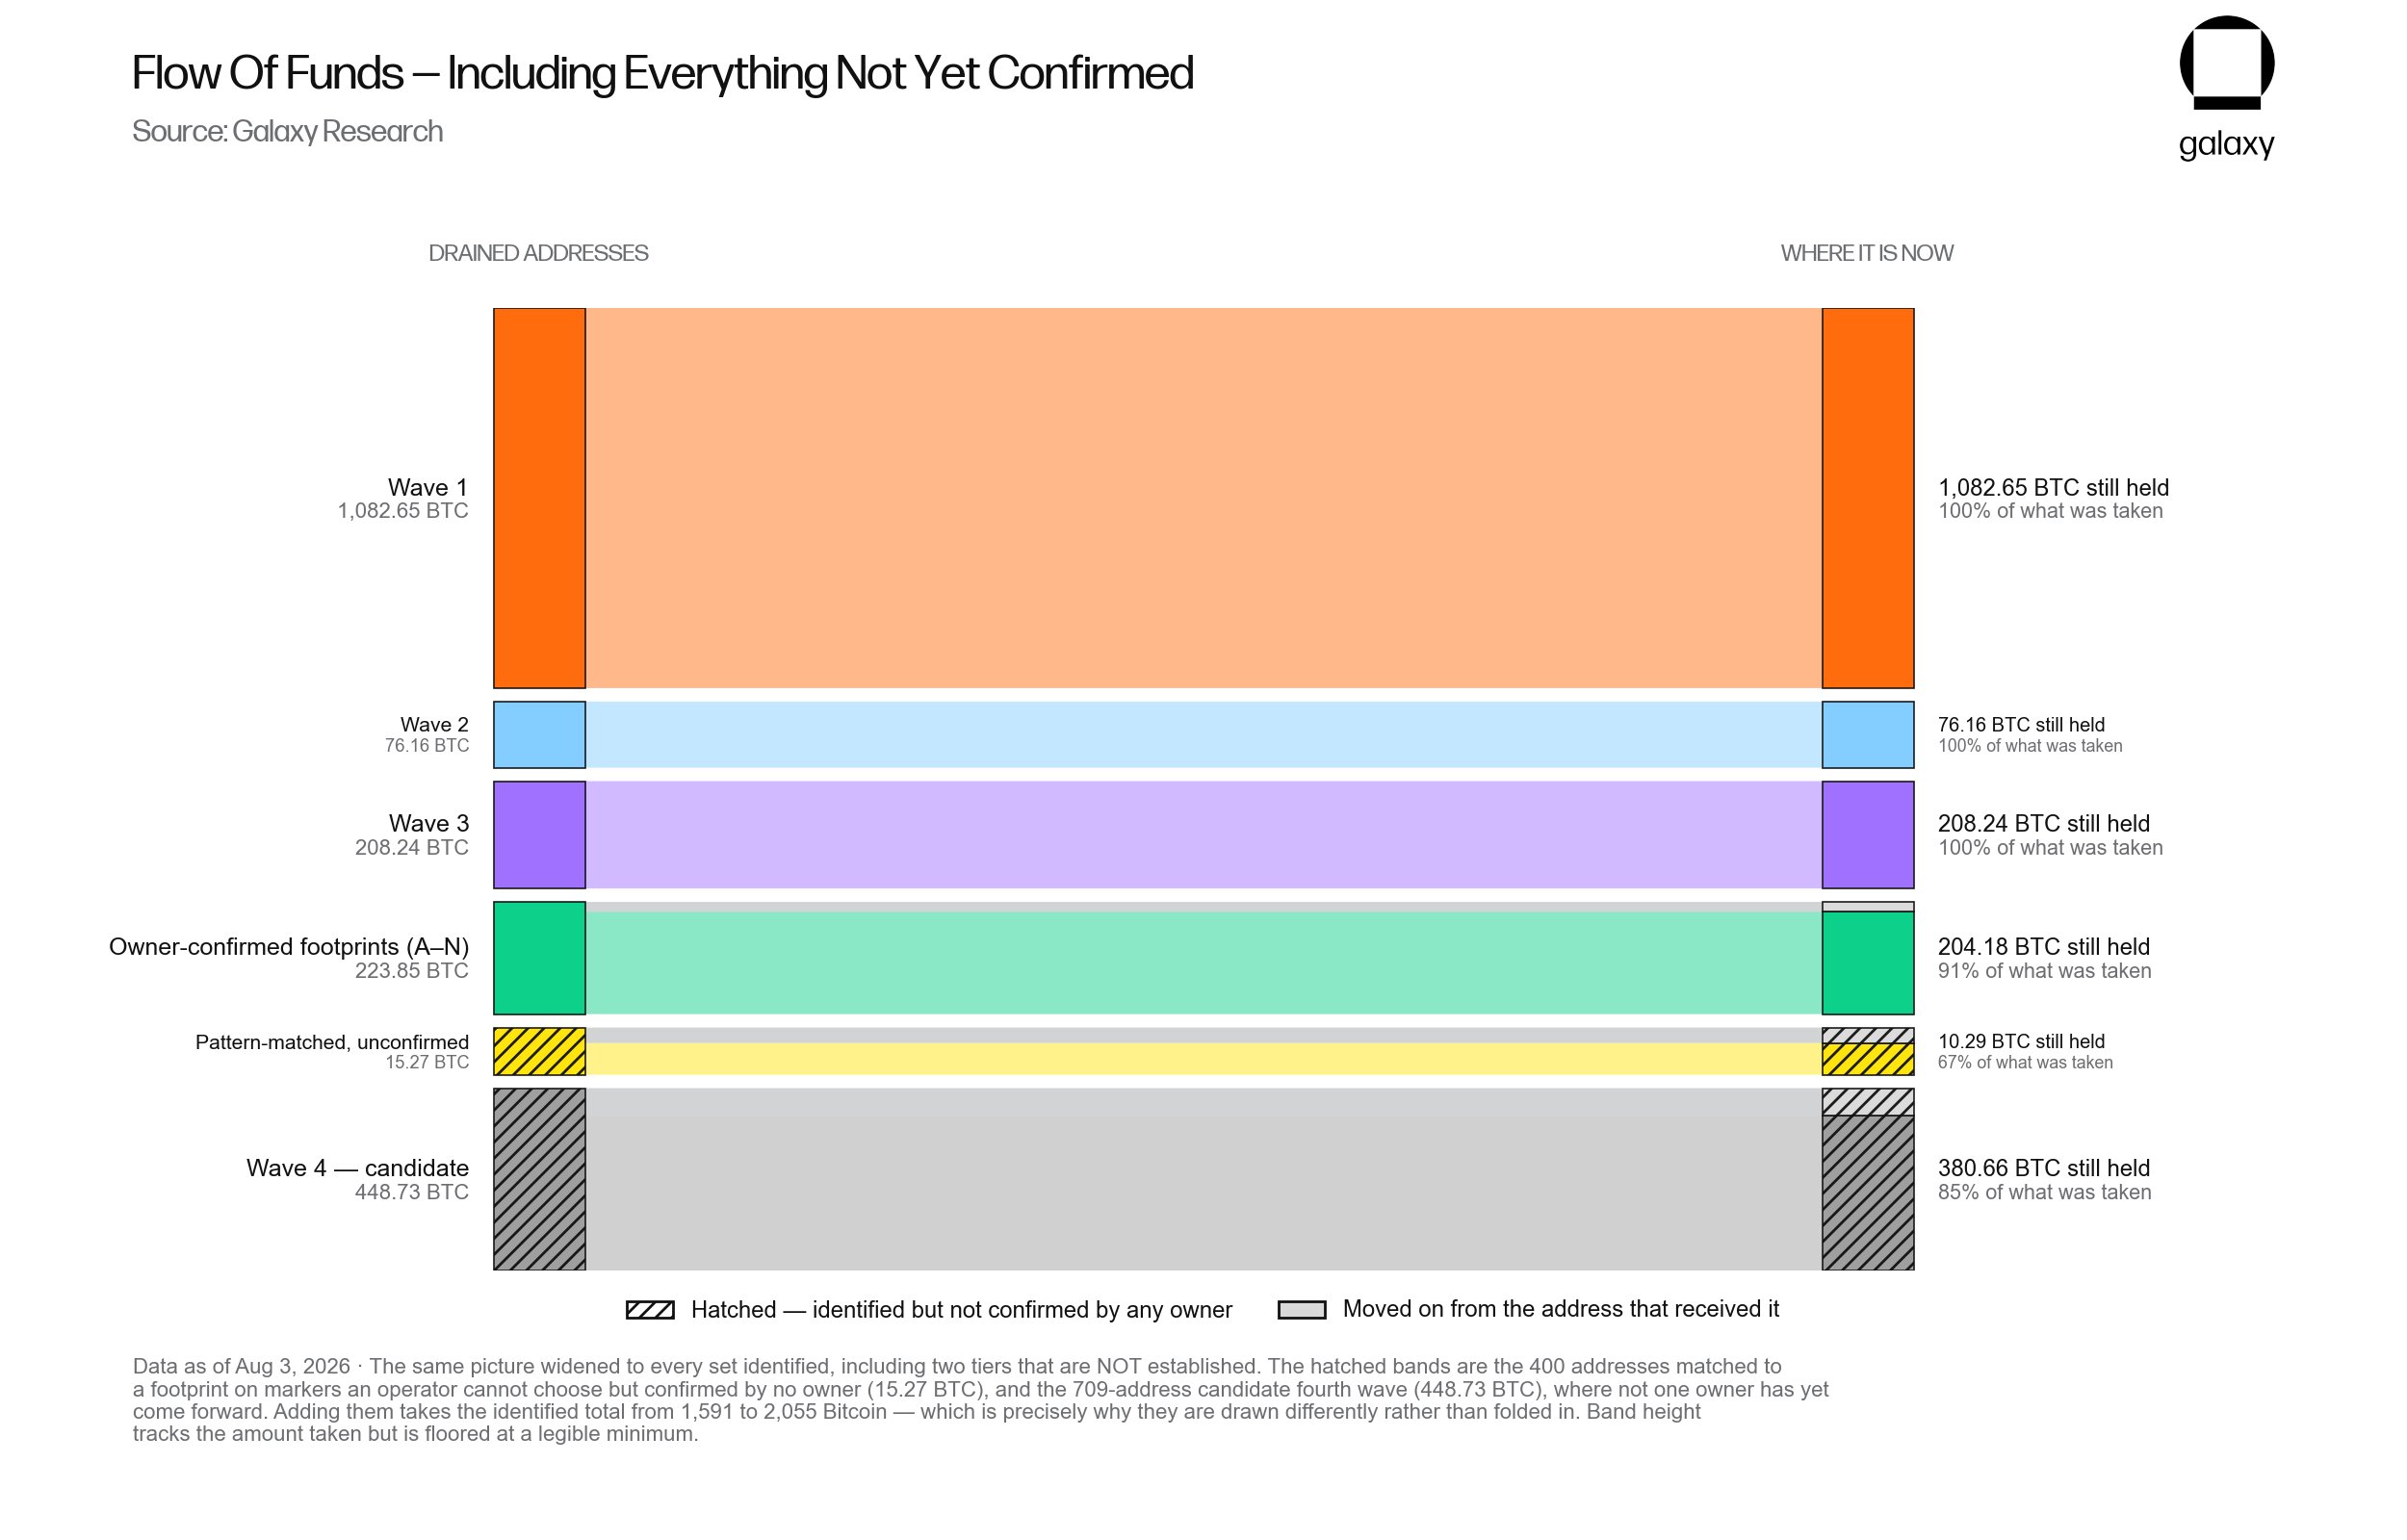
The extent of the confirmed losses, meticulously detailed by Galaxy Research, stems from a series of malicious activities, comprising three major attack waves and fourteen smaller incidents. Researchers at Galaxy have also identified a potential fourth wave of attacks that could elevate the total stolen Bitcoin to 2,055 BTC, further increasing the financial impact. These additional addresses remain under scrutiny, pending further victim reports and confirmation.
The Genesis of the Coldcard Crisis: A Flaw in Randomness
At the heart of this security breach lies a fundamental flaw within the Coldcard firmware, traced back to a coding error introduced in March 2021. This error compromised the integrity of the recovery seed generation process on affected devices. Instead of relying solely on the robust hardware random-number generator, some units inadvertently utilized a weaker software-based process. This deviation resulted in the generation of recovery seeds with a significantly reduced number of possible combinations, making them susceptible to brute-force reconstruction of private keys. Crucially, this vulnerability allowed attackers to remotely derive private keys without physical access to the device or possession of the owner’s recovery phrase.
While Coinkite, the manufacturer of Coldcard, has released a security update to prevent the generation of new weak seeds, this measure does not safeguard wallets whose recovery phrases were already compromised by the flawed process. The threat persists for any user who has not migrated their funds to a newly generated, secure seed. Coinkite has issued urgent recommendations for users to install the firmware update, create a fresh recovery seed, and transfer all Bitcoin holdings from potentially vulnerable wallets. The ongoing nature of the threat underscores the principle that "not your keys, not your coins" is only meaningful if the keys themselves are generated and protected with the utmost security.
Unraveling the Attack: Victim Reports and Attacker Coordination
The scale of the exploitation became apparent as approximately 73 victims reached out to Alex Thorn, Galaxy Research’s head of research, seeking assistance in tracing their stolen Bitcoin. These victim reports were instrumental in identifying distinct attack patterns and led to the conclusion that at least 15 attackers are actively exploiting the vulnerability.
A significant portion of the stolen Bitcoin, approximately 90%, remains unmoved in attacker-controlled addresses. Notably, all funds associated with the initial three confirmed attack waves are still held at their original misappropriated locations, indicating a degree of patience or strategic planning by the perpetrators. Galaxy Research has proactively shared the identified addresses of the stolen funds with U.S. law enforcement agencies, cryptocurrency exchanges, and blockchain investigation firms. This collaboration aims to flag any attempts by the attackers to move the funds through centralized platforms, enhancing the chances of recovery or apprehension.
A Network Under Pressure: Bitcoin Activity Surges
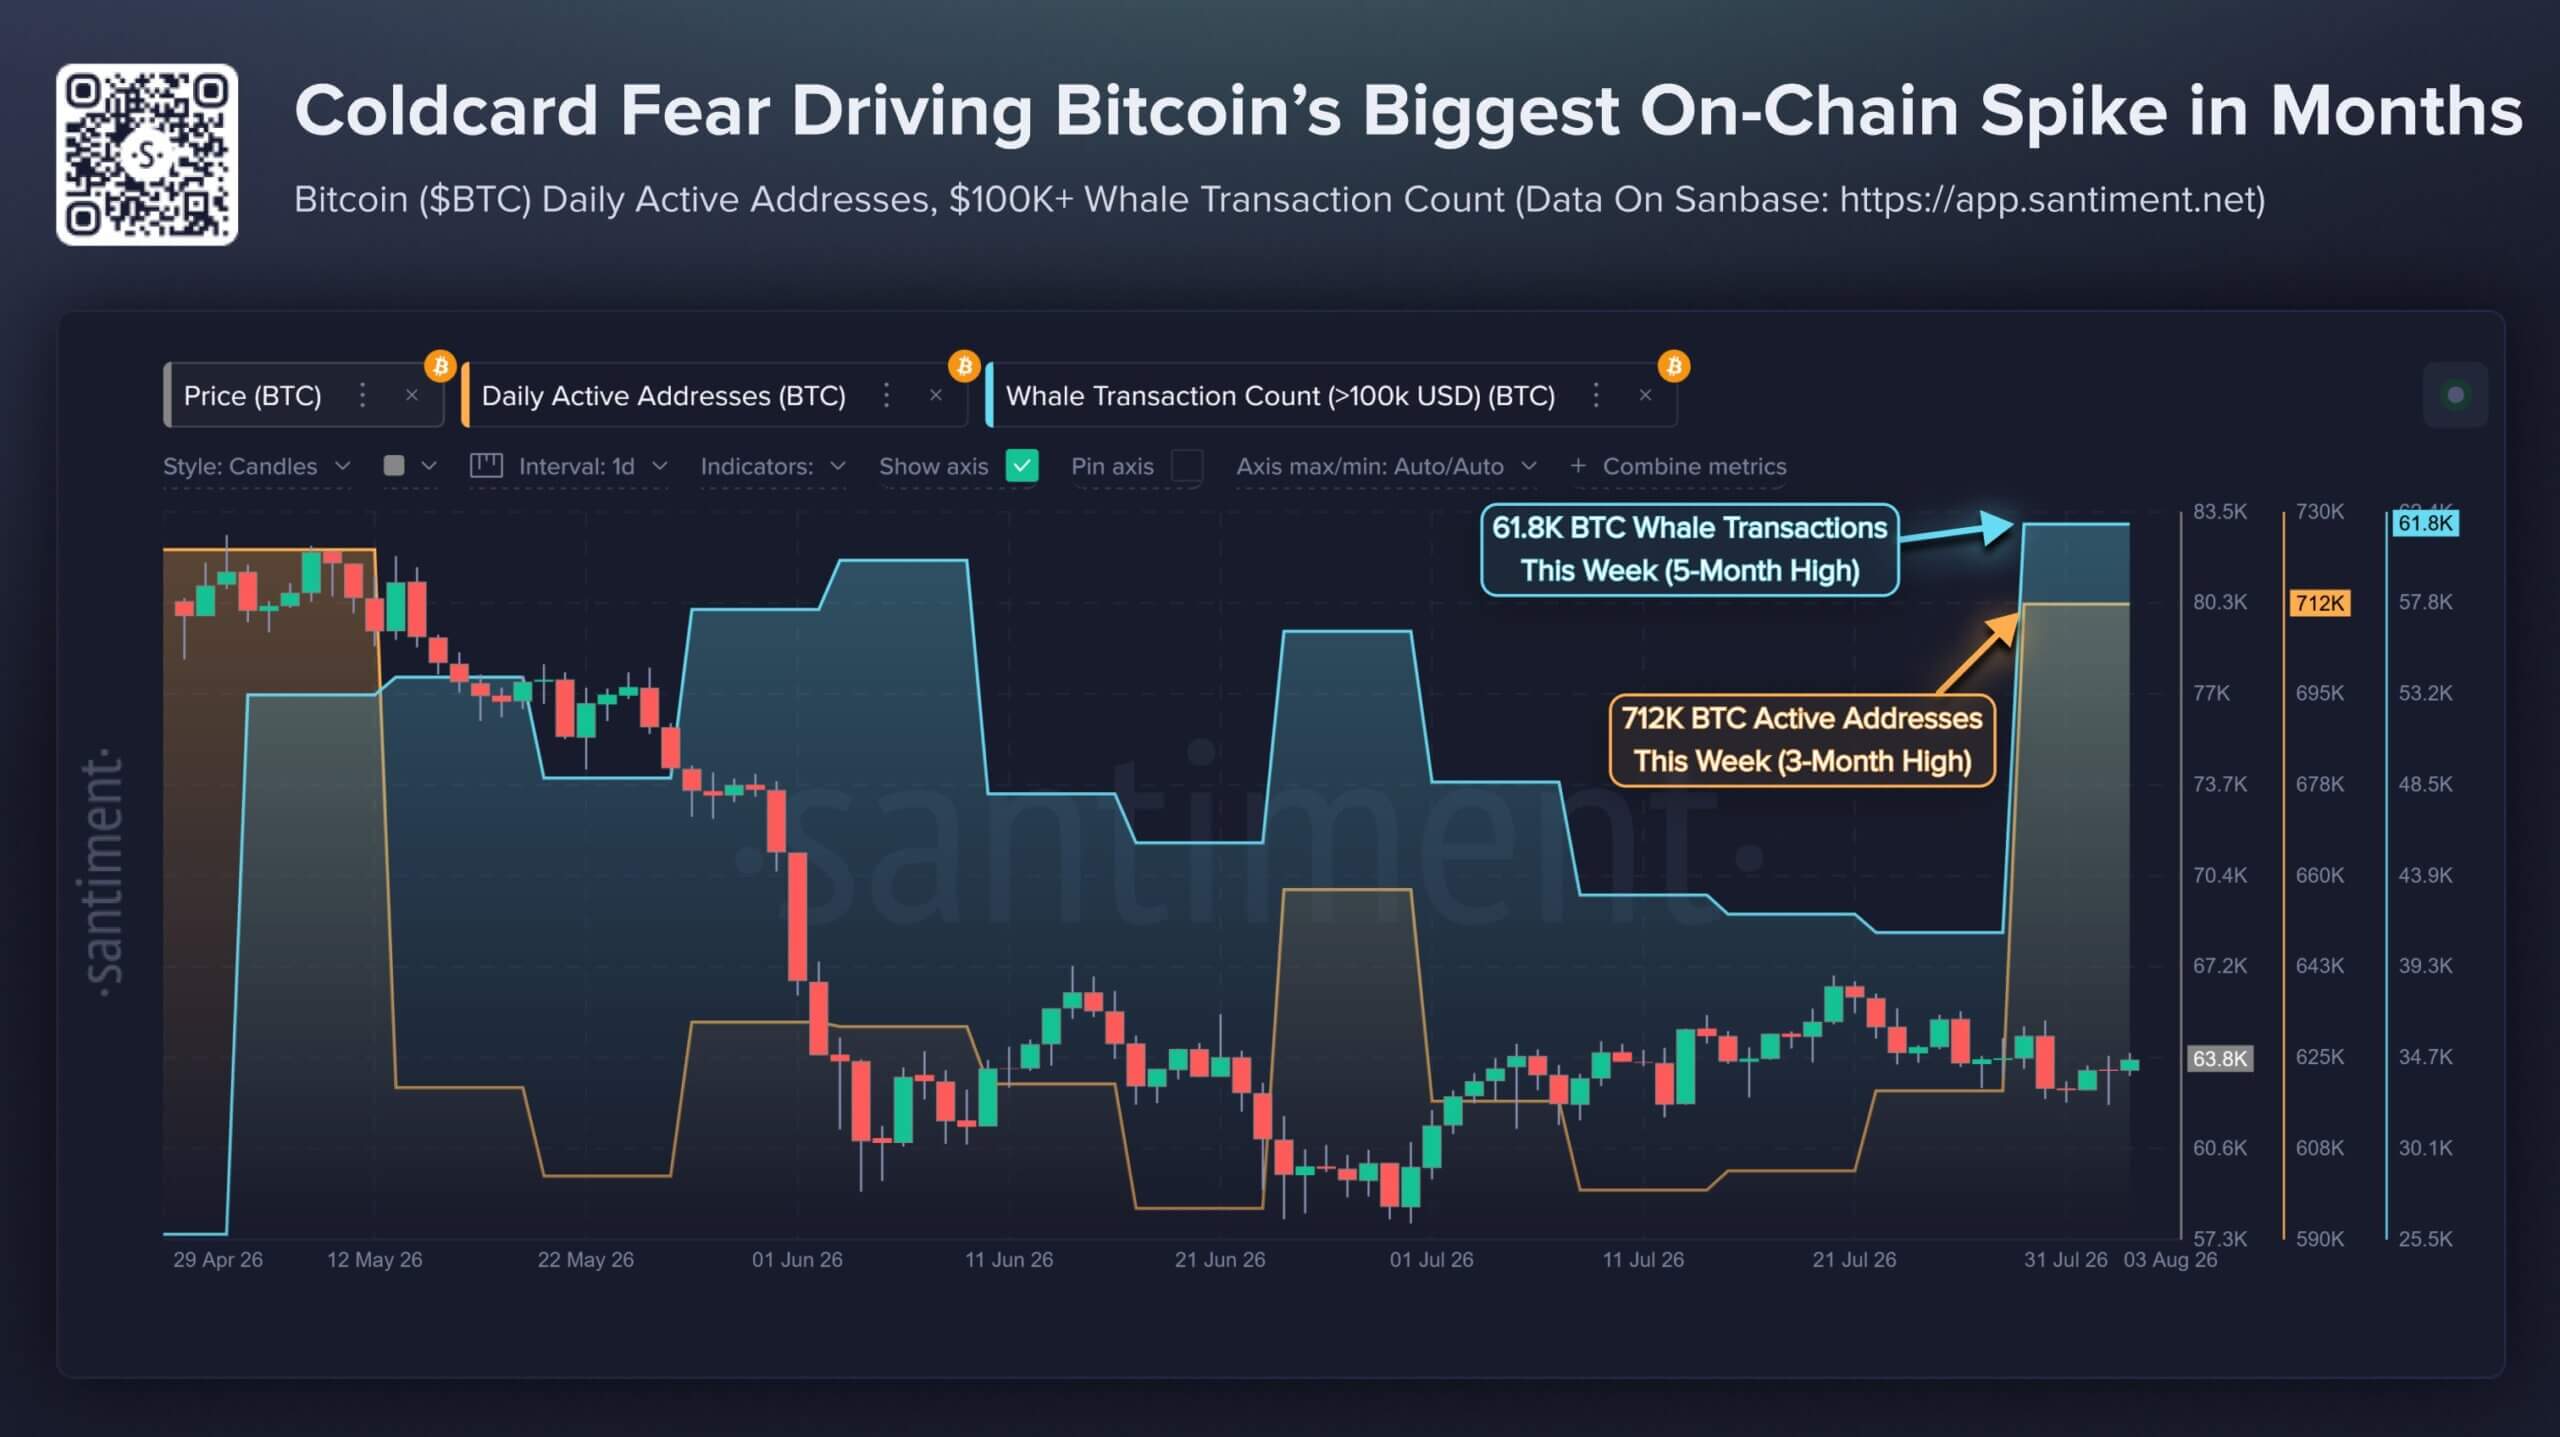
The urgency to secure funds has triggered a substantial surge in activity across the Bitcoin network, pushing metrics to levels not seen in several months. Data from Santiment reveals that the past seven days have seen 712,000 active Bitcoin addresses, marking a three-month high. Furthermore, the number of transactions exceeding $100,000 has reached 61,800 in the same period, a five-month peak.
CryptoQuant, a prominent blockchain analytics firm, has identified the Coldcard crisis as the primary catalyst for this increased network activity. Affected users are actively migrating their Bitcoin by creating new wallets, consolidating existing balances, or transferring funds to custodial platforms. A report by CryptoQuant shared with CryptoSlate indicates that transactions valued below $100,000 have surged to $3.2 billion, the highest volume recorded since November 2024.
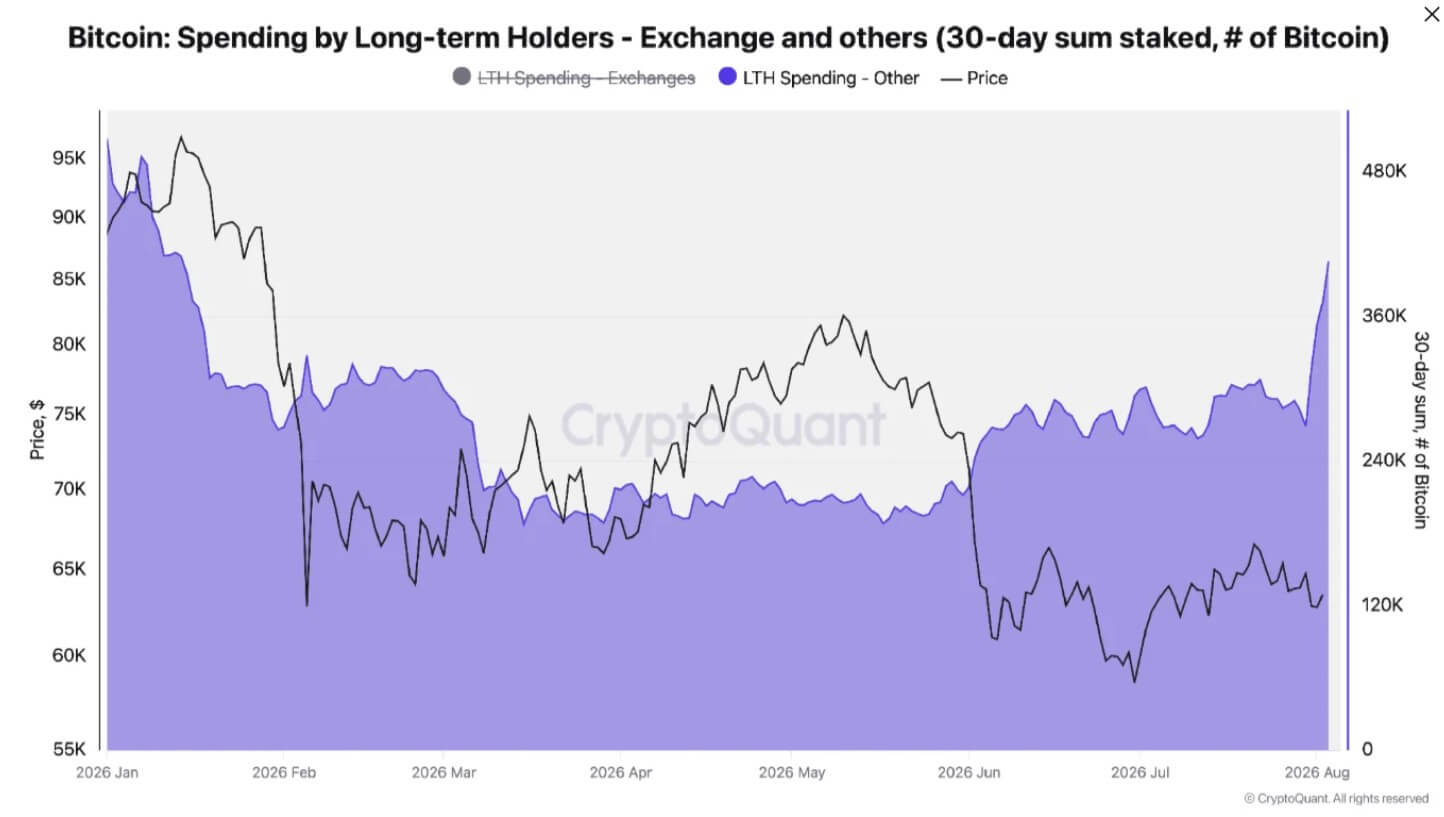
The movement of Bitcoin by long-term holders outside of exchanges has also seen a dramatic uptick. As of August 3rd, spending by this cohort on a 30-day basis rose to 406,000 BTC, a significant increase from 269,000 BTC prior to the exploit and the highest figure since January. It is important to note that these on-chain movements do not necessarily signify outright sales. A transfer from a compromised Coldcard address to a newly secured wallet will appear as "spent Bitcoin" on the blockchain, even if the ownership effectively remains with the original holder.
The sheer volume of these transfers has led to network congestion. Transactions awaiting confirmation in Bitcoin’s mempool increased from approximately 33,000 to around 96,000, reaching levels not observed since June 20th. This spike reflects the simultaneous efforts of thousands of holders attempting to migrate their assets to safety.
Inflows to Exchanges and the Rise of Phishing Scams
A portion of the migrating Bitcoin has found its way to centralized exchanges, offering an immediate holding place for users evacuating vulnerable wallets. CryptoQuant data indicates that deposits from smaller holders have reached their highest point since February 6th. This suggests that some users are temporarily entrusting their funds to existing custodial accounts while they deliberate on their next steps, whether it be establishing a new self-custody solution or switching hardware providers.
Between July 28th and August 3rd, total exchange reserves saw a net increase of approximately 17,500 BTC, rising from roughly 2.702 million BTC to 2.719 million BTC. Binance, in particular, absorbed a significant portion of this influx, receiving about 51% of the net increase, with its reserves climbing by approximately 9,000 BTC to 659,000 BTC. While these inflows bolster immediate trading liquidity and could exert short-term selling pressure, they do not definitively indicate an intention to sell. As previously mentioned, these deposits may represent temporary custodial arrangements during the process of securing new wallets.
Heightened Scammer Activity Amidst Wallet Migrations
The frantic migration process has also created fertile ground for scammers. Criminals are actively distributing fraudulent migration instructions and impersonating wallet support teams to exploit users seeking to secure their assets. Trezor, a rival hardware wallet manufacturer, has issued a stark warning, noting a significant increase in phishing attempts following the disclosure of the Coldcard vulnerability.
Trezor has emphatically advised its users never to share their recovery seeds or enter them into websites, applications, or forms provided through unsolicited messages. The company stresses that recovery words should only be entered directly onto a Trezor device during a legitimate wallet restoration process. Furthermore, users are urged to disregard any migration instructions received via email, direct messages, or phone calls. Trezor has confirmed that its devices were not affected by the Coldcard security incident.
This warning underscores the precarious situation faced by affected users. They must navigate the complex and time-sensitive task of moving their Bitcoin before their private keys can be reconstructed, all while evading scammers who are actively attempting to solicit their recovery words. It is crucial to understand that simply importing an existing, compromised seed into another hardware wallet does not neutralize the vulnerability. Users must generate an entirely new recovery phrase and transfer their funds to an address derived from this secure seed – a process more intricate than a standard firmware update or wallet restoration. Scammers are exploiting this complexity by directing users to malicious applications, requesting recovery words under the guise of security checks, or providing fraudulent addresses they claim are secure.
Revisiting Custody Debates: ETFs Gain Traction
The widespread migration towards exchanges and the escalating risks associated with wallet transfers have reignited the debate surrounding Bitcoin custody, potentially bolstering the case for regulated investment products like spot Bitcoin Exchange-Traded Funds (ETFs). Eric Balchunas, a senior ETF analyst at Bloomberg Intelligence, suggested that the Coldcard breach could influence investors, including long-term holders, to consider migrating towards spot Bitcoin ETFs.
Traditionally, Bitcoin proponents have expressed reservations about ETFs, arguing that investors in these products do not directly control the underlying coins or private keys. Instead, institutional custodians hold these assets on behalf of the funds. However, in the current environment, this custodial arrangement may appear more appealing when contrasted with the risks associated with relying on a smaller hardware wallet manufacturer. ETF issuers and their custodians are typically large, established financial institutions with extensive experience in safeguarding client assets, whereas Coldcard is operated by a relatively small company.
While institutional custody does not eliminate the possibility of theft or operational failures, a successful attack on an ETF custodian would likely trigger an immediate regulatory investigation and a coordinated response involving the fund manager, custodian, and law enforcement agencies.
Currently, there is no direct evidence to suggest that Coldcard users have purchased ETF shares as a direct consequence of this exploit. Similarly, the increased deposits into exchanges might prove to be a temporary measure as users establish new wallets and return to self-custody. Nevertheless, the breach has undeniably altered the risk assessment for investors deciding on the safest place to store their Bitcoin. Self-custody offers independence from intermediaries but places the entire responsibility for hardware and software security on the user. For those now attempting to escape compromised seeds while fending off sophisticated phishing attacks, the institutional framework, once criticized for ceding control to "Wall Street," may now present a more straightforward and potentially safer alternative. The incident serves as a stark reminder that in the realm of digital assets, security is paramount, and the methods employed to achieve it are constantly evolving, as are the threats designed to undermine them.