admin
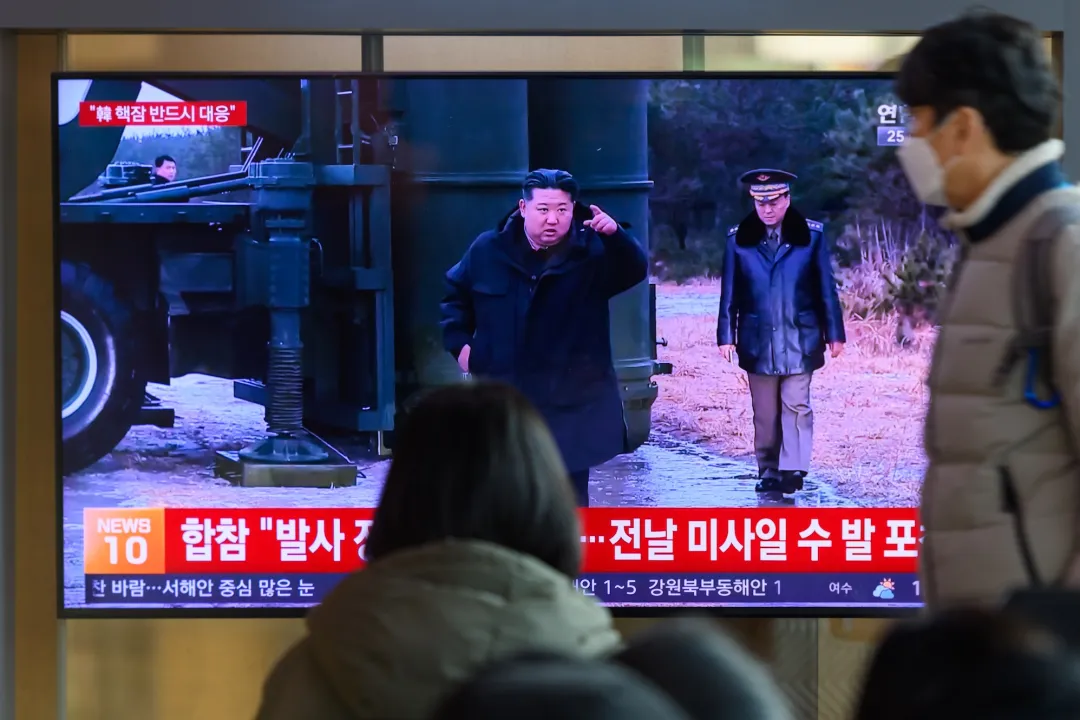
The global cryptocurrency landscape was reshaped last week as Binance, the world’s largest digital asset exchange by trading volume, confirmed that state-sponsored hackers from North Korea successfully orchestrated a heist totaling $6.3 billion. This unprecedented breach, now recognized as the largest single theft in the history of decentralized finance, was the culmination of a meticulous, months-long social engineering campaign targeting specific internal personnel. According to updated statements from the exchange and corroborating reports from federal investigators, the attackers utilized a blend of deceptive social media engagement and sophisticated malware to bypass the company’s multi-layered security infrastructure. The incident has prompted a complete suspension of customer withdrawals across the Binance network and triggered an international investigation involving the Federal Bureau of Investigation (FBI) and several prominent blockchain forensic firms.
The Anatomy of a State-Sponsored Social Engineering Attack
The genesis of the breach traces back several months, involving a highly targeted social engineering operation aimed at the Binance wallet development team. Cybersecurity researchers have long warned of the "fake recruiter" trope, a tactic where attackers pose as hiring managers from prestigious technology or investment firms to build rapport with high-value targets. In this instance, North Korean actors created elaborate, fake social media profiles to contact a senior software engineer responsible for maintaining Binance’s wallet architecture.
The attackers initiated contact under the guise of a lucrative job opportunity, engaging the engineer in a series of professional discussions and technical interviews. To maintain the illusion of legitimacy, the perpetrators utilized stolen identities of American citizens, creating a dossier of credentials that appeared authentic to both the target and initial background checks. Following two successful rounds of purported interviews, the engineer was asked to complete a technical "coding assignment" as part of the final evaluation process.
The assignment was delivered as a downloadable file which, when executed, deployed a sophisticated piece of malware onto the engineer’s work-issued laptop. Despite Binance’s investment in advanced threat detection systems, the company admitted that its security tools failed to identify the malicious code at the point of entry. This initial compromise provided the attackers with a persistent foothold within the exchange’s internal network, allowing them to monitor communications and identify further targets for lateral movement.
Lateral Movement and the Exploitation of Network Trust
Once the initial workstation was compromised, the hackers demonstrated a high degree of technical proficiency by navigating Binance’s internal environment. The goal was to escalate privileges and gain access to systems with the authority to move massive quantities of digital assets. The attackers leveraged the first engineer’s access to compromise an internal tool, which subsequently allowed them to take control of the workstations of two additional engineers on the same wallet team.
The investigation revealed a secondary vulnerability that accelerated the hackers’ progress. One of the additional engineers had unwittingly downloaded a tampered application months earlier. This malware, categorized as a "password-stealer," was acquired after the engineer clicked on a malicious link in search engine results—a technique known as SEO poisoning. Although Binance had identified the anomaly and replaced that specific laptop prior to the $6.3 billion heist, the hackers had already successfully exfiltrated the engineer’s credentials.
By combining the fresh access from the social engineering hook with the previously stolen credentials, the attackers moved to a third engineer’s computer. This individual held high-level administrative permissions, granting the hackers the ability to interact with the core systems that control Binance’s liquidity and wallet reserves. This sequence of events highlights a critical failure in the "defense-in-depth" strategy, as the attackers were able to pivot through multiple layers of the organization by exploiting individual human errors and fragmented security oversights.
Chronology of the $6.3 Billion Heist
The timeline of the attack suggests a level of patience and planning characteristic of state-sponsored groups like the Lazarus Group, to whom the FBI has officially attributed the theft.
- Early 2026: Initial contact is established with Binance software engineers via professional networking platforms. The attackers spend months "grooming" the targets.
- Mid-2026: A secondary engineer’s credentials are stolen via a malicious search engine result, providing the attackers with backup access points.
- Late October 2026: The primary social engineering target downloads the malicious coding assignment. The attackers gain active remote access to the internal network.
- October 28, 2026: Hackers navigate laterally to the third engineer’s workstation, gaining control over wallet protocols.
- October 29, 2026: Large-scale unauthorized transfers begin. Binance systems detect anomalies, and the exchange officially pauses all customer withdrawals to prevent further loss.
- November 3, 2026: Binance releases a comprehensive statement via X (formerly Twitter) and its official blog, confirming the North Korean origin of the attack and the $6.3 billion valuation of the stolen assets.
The FBI’s Cyber Division, in coordination with blockchain investigators, released a formal alert confirming that the Democratic People’s Republic of Korea (DPRK) was responsible. The alert emphasized that such heists are a primary source of revenue for the North Korean regime, specifically intended to circumvent international sanctions and fund its ballistic missile and nuclear weapons programs.
Supporting Data: The Rising Scale of Crypto Heists
The Binance hack represents a significant escalation in the volume of capital stolen by North Korean actors. According to data from cybersecurity firm CrowdStrike, state-sponsored actors from the DPRK were responsible for nearly half of all major intrusions at U.S.-based technology and fintech companies over the past year. These actors frequently pose as remote IT workers, venture capitalists, or recruiters to gain internal access.
The $6.3 billion figure dwarfs previous records in the industry. For comparison:
- Ronin Bridge (2022): $625 million stolen (also attributed to North Korea).
- FTX Collapse/Hack (2022): Approximately $400 million in unauthorized transfers.
- Harmony Horizon Bridge (2022): $100 million.
Binance’s own internal audit revealed that the company has faced at least 57 suspected state-sponsored attacks from North Korea in the last 24 months. While most were successfully thwarted, the persistence of these actors suggests that cryptocurrency exchanges remain the highest-priority targets for the regime’s cyber units.
Official Responses and Remediation Efforts
In the wake of the disclosure, Binance leadership has adopted a posture of accountability, though many questions regarding the failure of their internal controls remain unanswered. A Binance spokesperson emphasized that the attack "should not have happened" and confirmed that the company is working with leading cybersecurity experts to perform a "ground-up" review of its network architecture.
"We are taking this incident with the utmost seriousness," the company stated. "Our primary focus is the security of our users’ funds and the integrity of our systems. We have already implemented new, more rigorous security measures, including enhanced endpoint protection and stricter protocols for the execution of third-party software on employee devices."
However, when pressed by investigative journalists regarding how the hackers managed to bypass specific security gateways—such as the ability to run unauthorized code on work laptops—Binance declined to provide granular details. The company also remained silent on whether any third-party cybersecurity audits had been conducted prior to the breach, or why the suspicious lateral movement across three high-security workstations was not flagged in real-time by internal monitoring tools.
Analysis of Broader Industry Implications
The Binance heist serves as a stark reminder that even the most well-capitalized firms in the digital asset space are vulnerable to the human element of cybersecurity. The reliance on social engineering rather than a direct "brute force" attack on the blockchain itself underscores a shift in adversary tactics. As cryptographic protocols become more robust, hackers are increasingly targeting the individuals who hold the "keys to the kingdom."
The implications for the broader cryptocurrency market are profound. The $6.3 billion loss has renewed calls for stricter regulatory oversight of centralized exchanges. Regulators in the United States and Europe are likely to use this incident as a catalyst for mandatory security standards, including required air-gapping of significant reserves and mandatory, frequent third-party security audits.
Furthermore, the incident highlights the ongoing challenge of "SEO poisoning" and the risks associated with the remote-work culture of the tech industry. When employees use search engines to find professional tools or engage in recruitment processes on personal or semi-secured devices, they create openings that state-sponsored actors are ready to exploit.
As Binance works to recover the stolen assets—a task that blockchain analysts describe as nearly impossible given the sophisticated laundering techniques used by the Lazarus Group—the industry must reckon with a new reality. The threat posed by state-sponsored actors is not a hypothetical risk but a persistent, well-funded, and highly patient operation. For Binance, the road to restoring customer trust will be long, and the $6.3 billion theft will remain a definitive case study in the devastating effectiveness of social engineering in the digital age.