admin
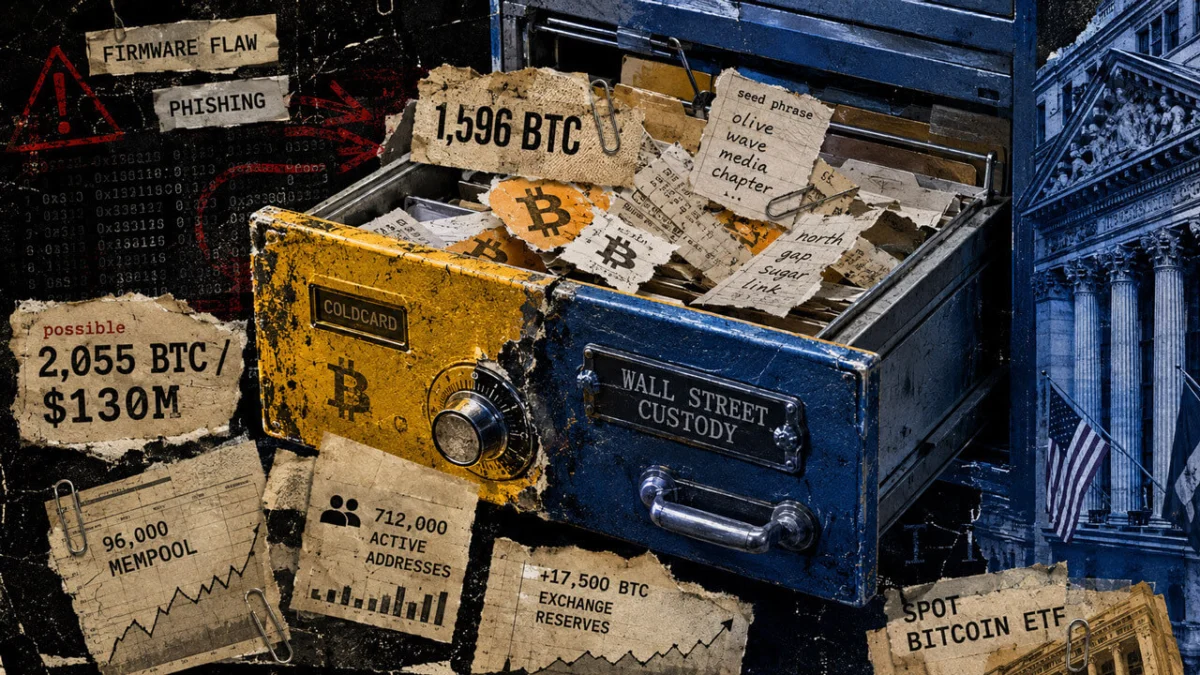
The Coldcard hardware wallet exploit has resulted in the theft of at least 1,596 BTC, valued at approximately $130 million, impacting an estimated 7,300 addresses. As users scramble to secure their digital assets, a significant movement of funds across the Bitcoin network is underway, pushing on-chain activity to multi-month highs and reigniting debates about cryptocurrency custody.
The Unfolding Crisis: Millions in Bitcoin Lost to Seed Generation Flaw
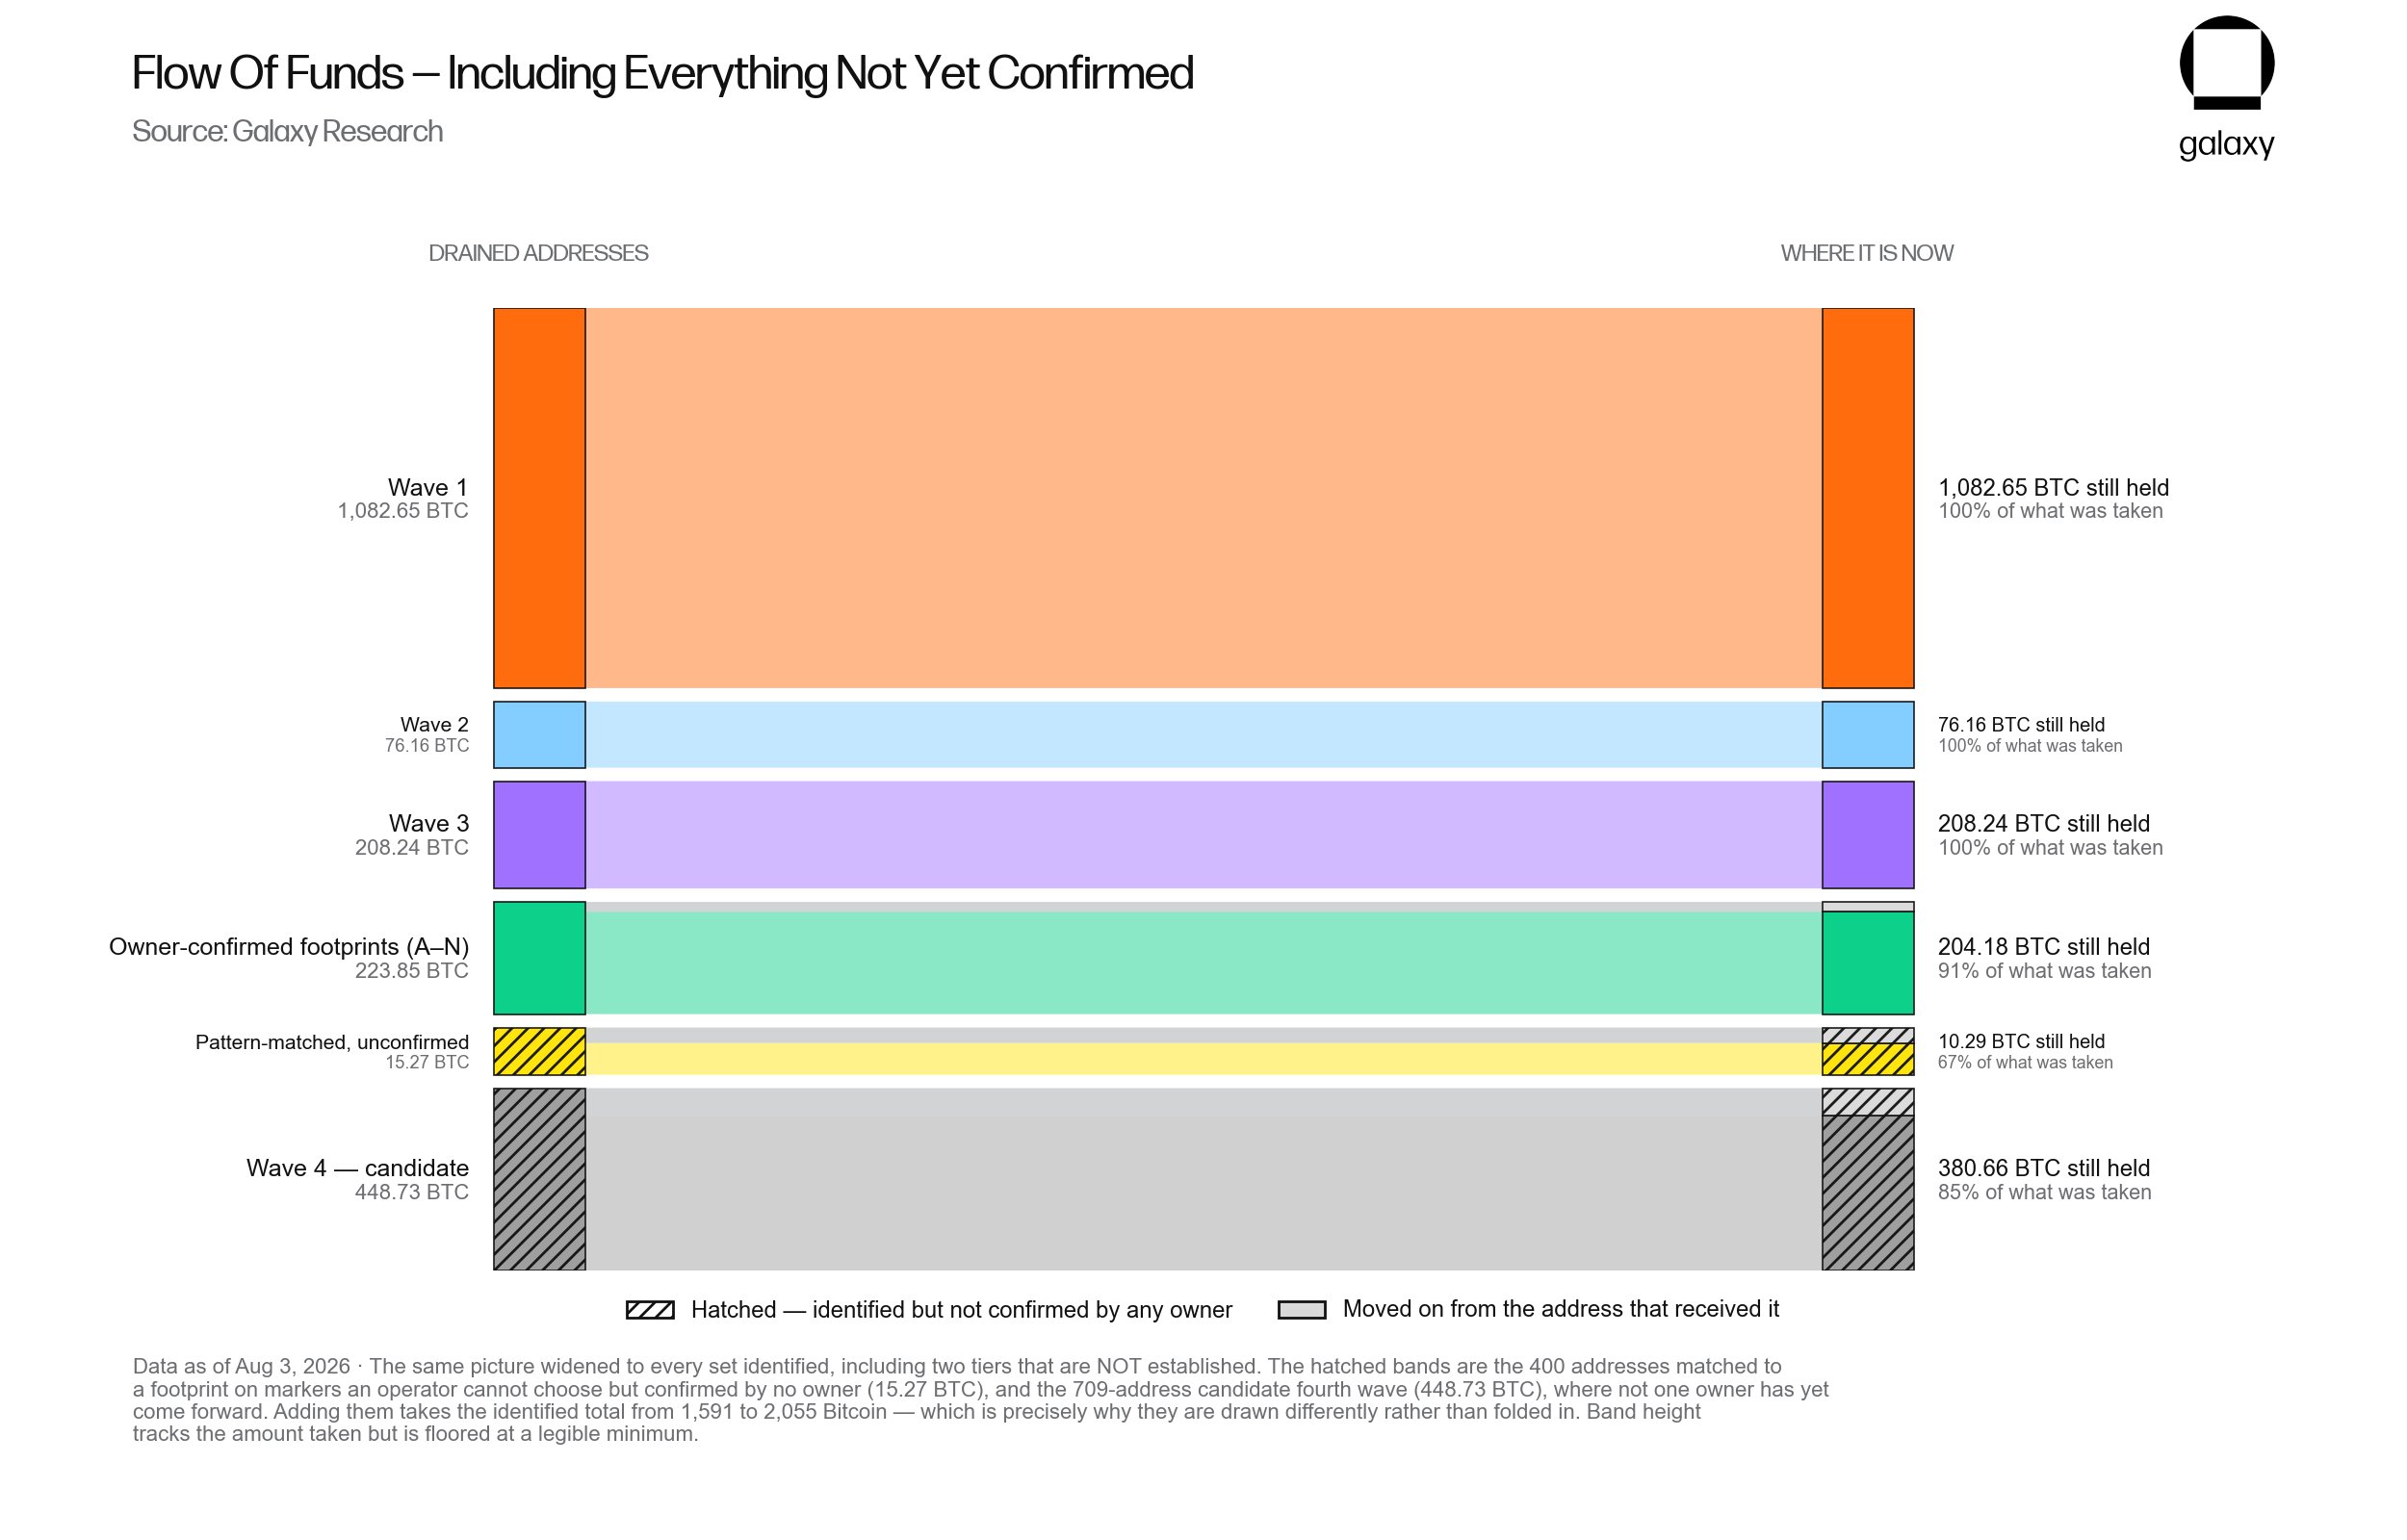
The security breach, initially identified and detailed by Galaxy Research, has sent shockwaves through the cryptocurrency community. The firm confirmed losses stemming from three major attack waves and at least 14 smaller incidents. Furthermore, Galaxy Research has identified a potential fourth wave of attacks that could push the total stolen Bitcoin to 2,055 BTC, a figure worth roughly $130 million. However, these potentially affected addresses remain outside the confirmed loss estimate pending additional victim reports.
Approximately 73 victims have proactively reached out to Alex Thorn, Galaxy’s head of research, seeking assistance in tracing their stolen Bitcoin. These individual reports have been instrumental in helping researchers pinpoint additional attack patterns and have led to the conclusion that at least 15 distinct attackers may be exploiting this vulnerability. A concerning aspect of the ongoing thefts is that roughly 90% of the stolen Bitcoin has remained stationary in attacker-controlled wallets, particularly those linked to the initial confirmed attack waves. This suggests attackers may be patiently awaiting opportune moments for liquidation or have yet to fully realize the scale of their illicit gains.
Galaxy Research has been actively collaborating with law enforcement agencies in the United States, cryptocurrency exchanges, and blockchain investigation firms. By sharing the identified addresses of the stolen funds, the aim is to flag any attempts by the perpetrators to move the Bitcoin through centralized platforms, thereby increasing the chances of recovery or apprehension.
Root Cause: A Subtle Flaw in Randomness Generation
The underlying cause of this significant security lapse lies in a flaw within the Coldcard firmware, reportedly dating back to March 2021. A coding error inadvertently caused certain devices to generate recovery seeds using a less robust software process. Instead of drawing sufficient randomness from the hardware’s dedicated random-number generator, the flawed process resulted in seeds with a significantly reduced number of possible combinations. This weakness created a vulnerability that allowed attackers to remotely reconstruct private keys without ever needing physical access to the device or obtaining the owner’s recovery words.
While Coinkite, the manufacturer of Coldcard, has issued a critical security update to prevent the creation of additional weak seeds, this update offers no protection for wallets whose recovery phrases were already compromised by the flawed generation process. This distinction is crucial, as it means any user who generated their seed on an affected device before the firmware update remains exposed.
Coinkite’s Response and Urgent Call to Action
In response to the unfolding crisis, Coinkite has issued urgent directives to its user base. The company is strongly advising all users to immediately install the latest security update, generate a completely new recovery seed, and then transfer all their Bitcoin holdings to wallets secured by these new, uncompromised seeds. The threat remains active because any wallet with a seed generated through the flawed process is perpetually vulnerable until its funds are migrated to a secure address.
On-Chain Activity Skyrockets: A Network Under Strain
The urgent need for Coldcard users to migrate their funds has had a dramatic and visible impact on the broader Bitcoin network. On-chain analytics firms are reporting activity levels not seen since earlier periods of significant market stress.
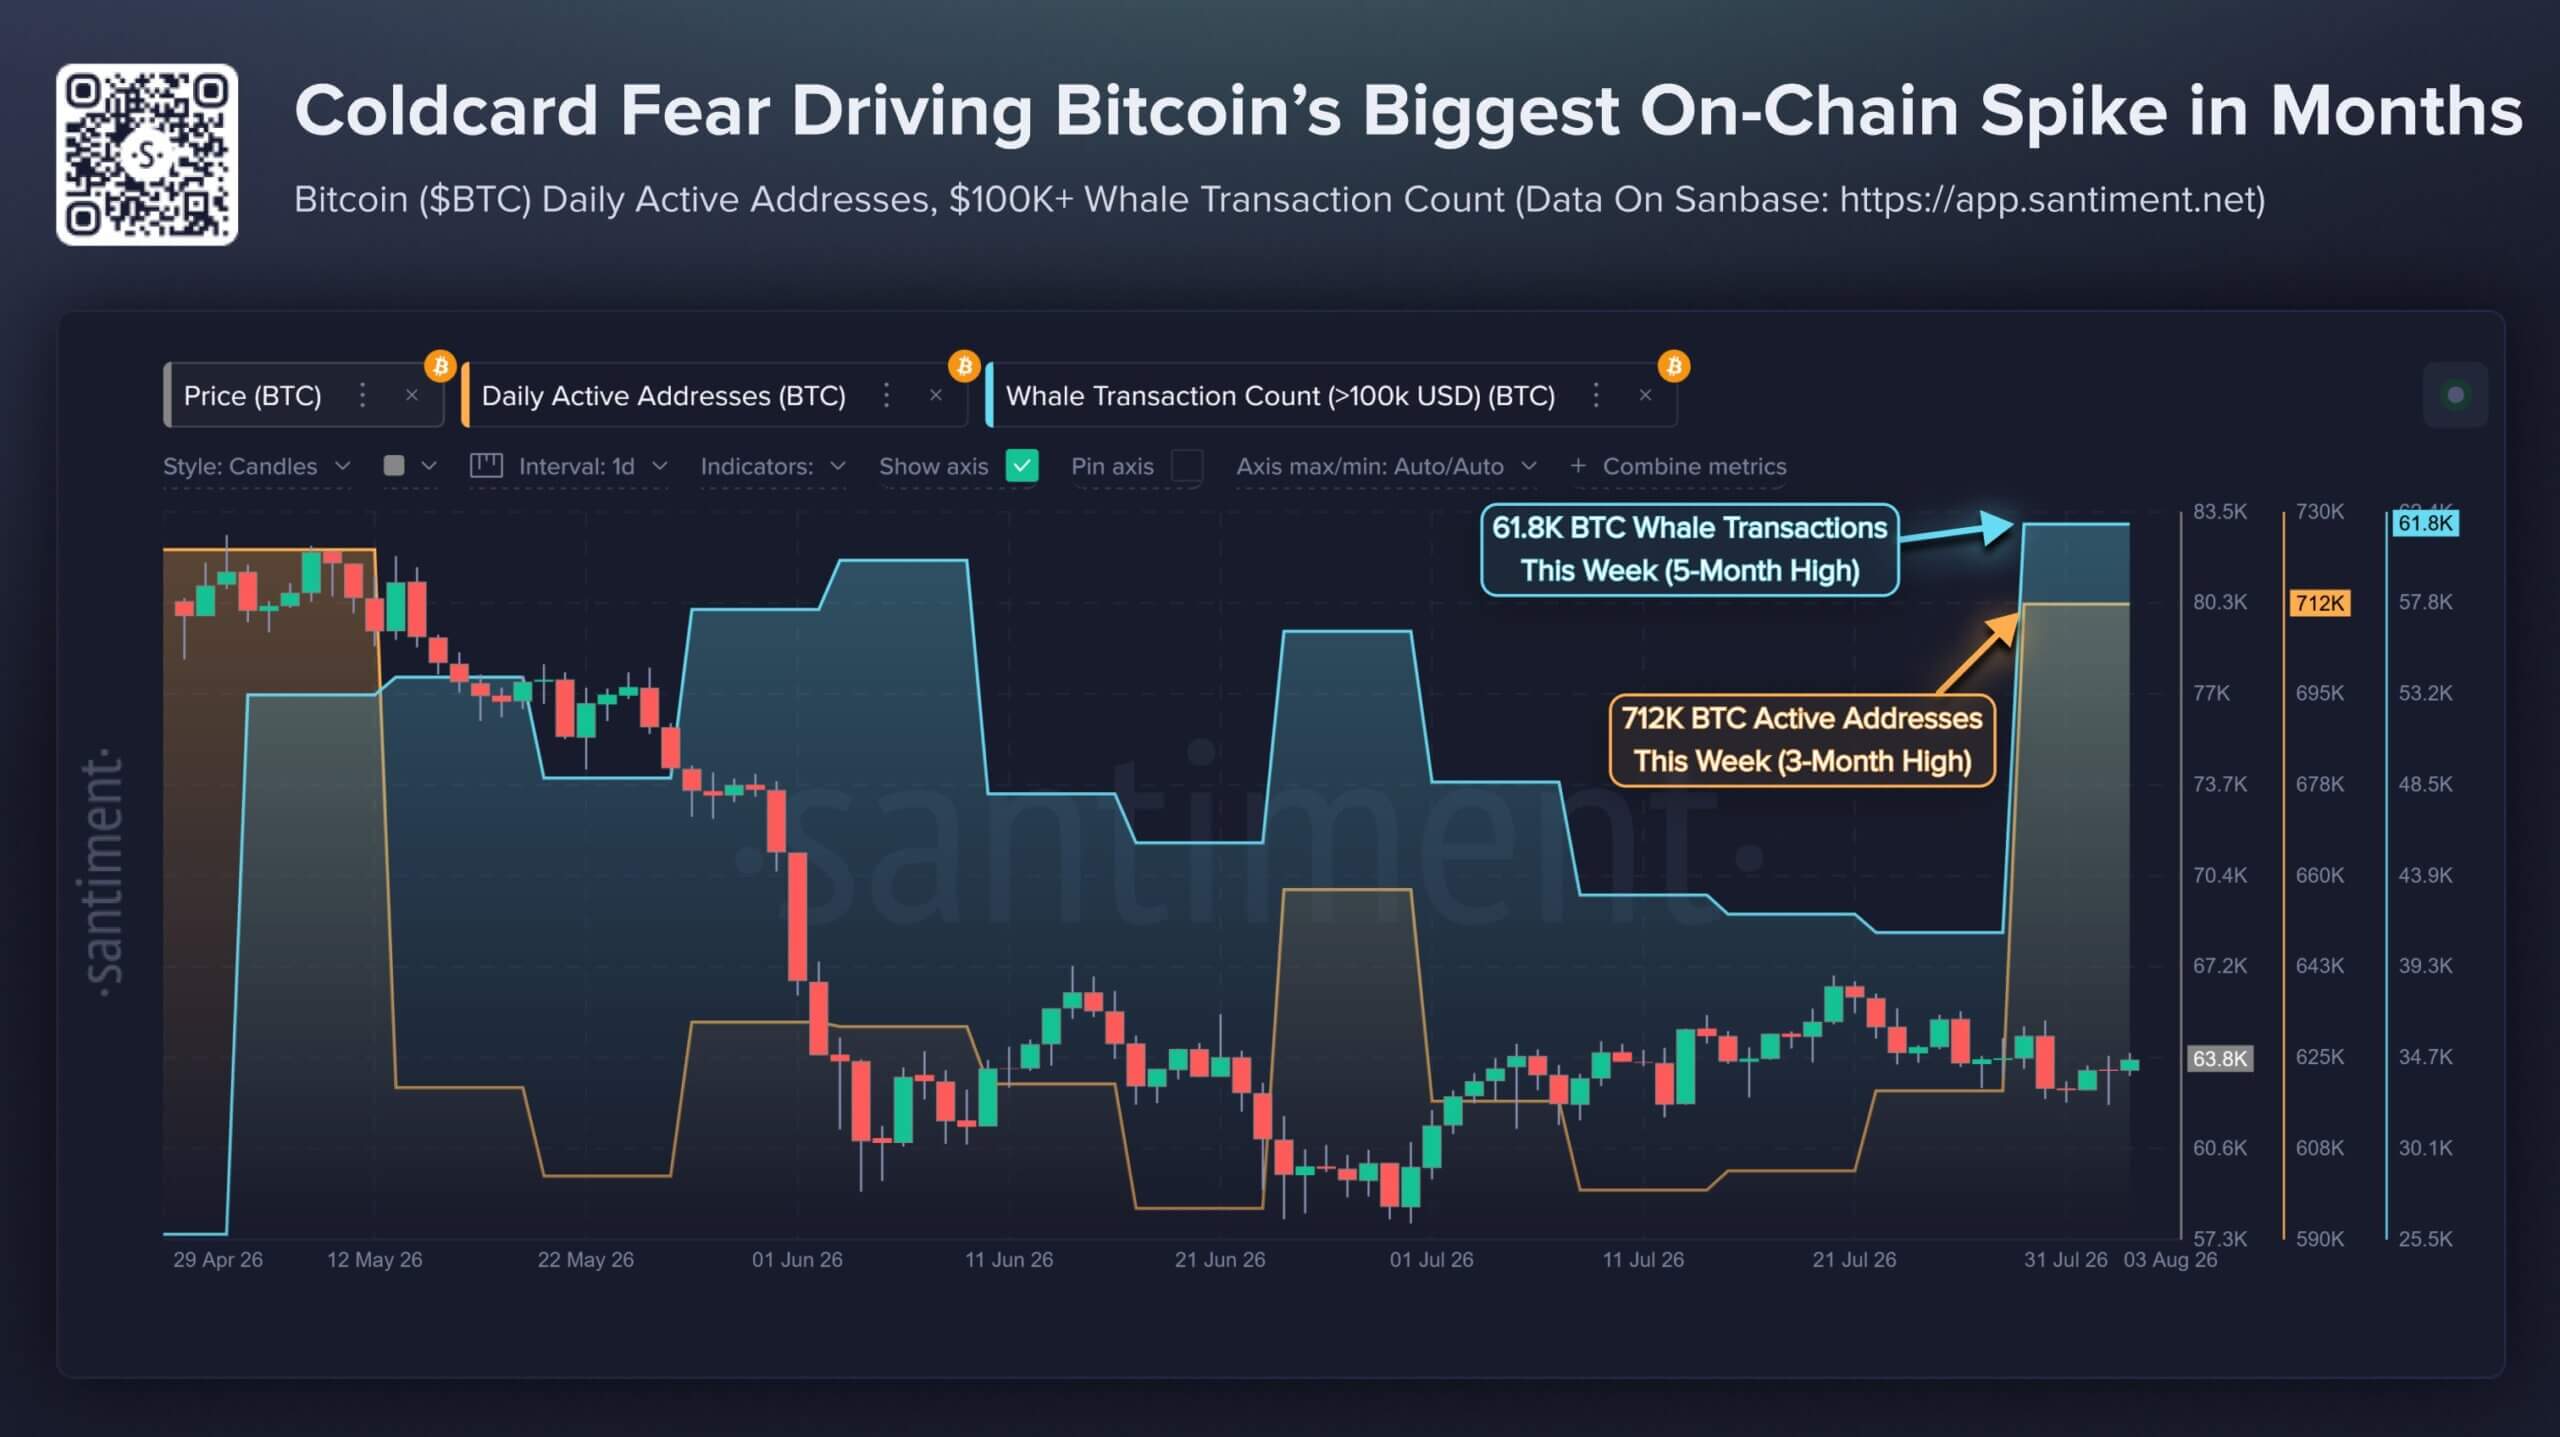
Data from Santiment indicates that the past seven days have seen approximately 712,000 active Bitcoin addresses, the highest number recorded in the last three months. Concurrently, the volume of transactions exceeding $100,000 has surged, reaching 61,800 within the same period, marking a five-month high.
CryptoQuant, another leading on-chain analytics provider, has identified the Coldcard crisis as the primary catalyst for this network surge. Affected users are reportedly migrating their coins into newly generated wallets, consolidating balances, or, in some cases, transferring funds to custodial platforms for temporary safekeeping.
In a report shared with CryptoSlate, CryptoQuant highlighted that transactions valued below $100,000 have reached a staggering $3.2 billion, representing the highest figure since November 2024. This indicates a broad-based movement of funds, not just among large holders but across a wide spectrum of users.
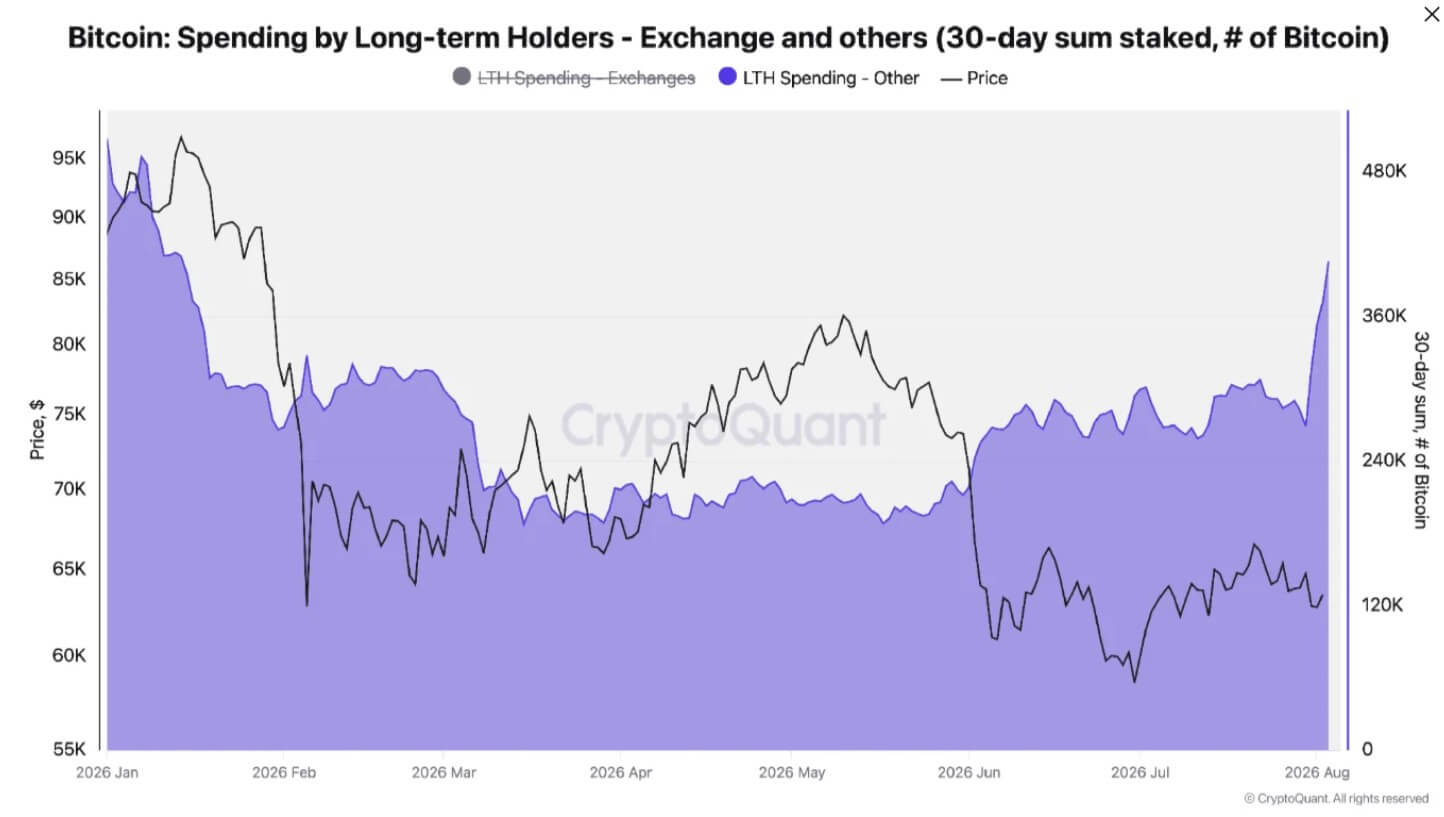
Furthermore, the spending activity by long-term Bitcoin holders outside of exchanges has also seen a significant increase. As of August 3rd, this metric reached 406,000 BTC on a 30-day basis, a substantial jump from 269,000 BTC prior to the exploit and the highest level observed since January. It is important to note, as CryptoQuant clarifies, that this increased spending does not necessarily equate to selling. A transfer from a compromised Coldcard address to a newly secured wallet will appear on-chain as a "spent" Bitcoin, even if the ownership remains with the original user.
The sheer volume of users attempting to migrate their funds simultaneously has led to network congestion. The number of transactions waiting in Bitcoin’s mempool has escalated dramatically, jumping from approximately 33,000 to around 96,000, the highest level recorded since June 20th. This congestion highlights the urgency and scale of the user response to the security threat.
Exchange Inflows Rise Amidst Phishing Scams Targeting Migrating Users
As a consequence of the mass migration, a portion of the Bitcoin being moved from potentially vulnerable Coldcard wallets has found its way into centralized exchanges. CryptoQuant data indicates that deposits from smaller holders have reached their highest levels since February 6th. This suggests that some users are opting for immediate safekeeping in existing custodial accounts while they strategize their next steps, whether that involves setting up a new self-custody solution or switching hardware providers.
Between July 28th and August 3rd, total exchange reserves saw an increase of approximately 17,500 BTC, rising from roughly 2.702 million BTC to 2.719 million BTC. Binance, in particular, has absorbed a significant portion of this influx, receiving about 51% of the net increase, with its reserves climbing by approximately 9,000 BTC to reach 659,000 BTC.
While these inflows boost the immediate availability of Bitcoin for trading and could potentially exert short-term sell-side pressure, they do not definitively indicate that holders intend to liquidate their assets. As mentioned, some of these deposits may represent temporary custody arrangements during the critical transition period of replacing compromised seeds and testing new wallet configurations.
The Rise of Scams: Exploiting User Vulnerability
The urgency surrounding wallet migrations has unfortunately created a fertile ground for opportunistic scammers. Criminals are actively distributing fraudulent migration instructions and impersonating wallet support teams to trick unsuspecting users. These phishing attempts capitalize on the stress and confusion of the migration process.
Trezor, a prominent rival hardware wallet manufacturer, has issued a stark warning about the increase in phishing activities following the disclosure of the Coldcard flaw. They strongly advise users to never share their recovery seeds or enter them into any websites, applications, or forms, especially those received through unsolicited messages. Recovery words should only be entered directly onto a Trezor device during a legitimate wallet restoration process. Users are urged to disregard any migration instructions received via email, direct messages, or phone calls, and Trezor has confirmed that its devices were not affected by the Coldcard incident.
This warning underscores the perilous tightrope walk facing affected users. They must act swiftly to move their Bitcoin before private keys can be reconstructed by attackers, while simultaneously fending off scammers who aim to steal their recovery words directly. It’s critical to understand that simply importing an existing, compromised weak seed into another hardware device does not eliminate the vulnerability. The only secure solution involves generating an entirely new recovery phrase and transferring funds to an address derived from this fresh seed. This process is significantly more complex than a simple firmware update or a standard wallet restoration. Scammers are adept at exploiting this complexity by directing users to malicious applications, demanding recovery words under the guise of security checks, or providing seemingly safe, but fraudulent, deposit addresses.
Broader Implications: The ETF Debate Reignited
The ongoing Coldcard crisis, coupled with the increased migration of funds towards centralized exchanges, has inadvertently bolstered the argument for holding Bitcoin through regulated investment products like spot Bitcoin Exchange-Traded Funds (ETFs).
Eric Balchunas, a senior ETF analyst at Bloomberg Intelligence, suggested that the Coldcard breach could prompt a shift in investor behavior, potentially encouraging some, including long-term holders, to migrate towards spot Bitcoin ETFs. Traditionally, Bitcoin purists have criticized ETFs, arguing that investors lose direct control over their private keys, with institutional custodians holding the underlying assets on behalf of the funds.
However, Balchunas posits that this arrangement might now appear more appealing when contrasted with the perceived risk of relying on a smaller hardware wallet manufacturer. ETF issuers and their custodians are typically large, established financial institutions with extensive experience in safeguarding client assets over decades. In contrast, a company like Coldcard, while reputable, operates with a smaller workforce.
It is important to acknowledge that institutional custody does not eliminate the possibility of theft or operational failure. Nevertheless, Balchunas suggests that a successful attack on an ETF custodian would likely trigger an immediate and comprehensive regulatory investigation, involving a coordinated response from the fund manager, custodian, and relevant law enforcement agencies.
While there is no direct evidence to suggest that Coldcard users have already purchased ETF shares as a direct consequence of this exploit, and the current rise in exchange deposits might prove temporary as users re-establish self-custody, the incident has undoubtedly altered the risk-reward calculation for many investors. Self-custody offers independence from intermediaries like banks, exchanges, or fund managers, but it places the full burden of securing hardware and software for private key generation squarely on the user. For those now navigating the complex and dangerous landscape of escaping compromised seeds while evading sophisticated phishing attacks, the institutional structure of ETFs, once criticized for entrenching Bitcoin within traditional finance, may present a seemingly simpler, albeit different, path forward.