admin
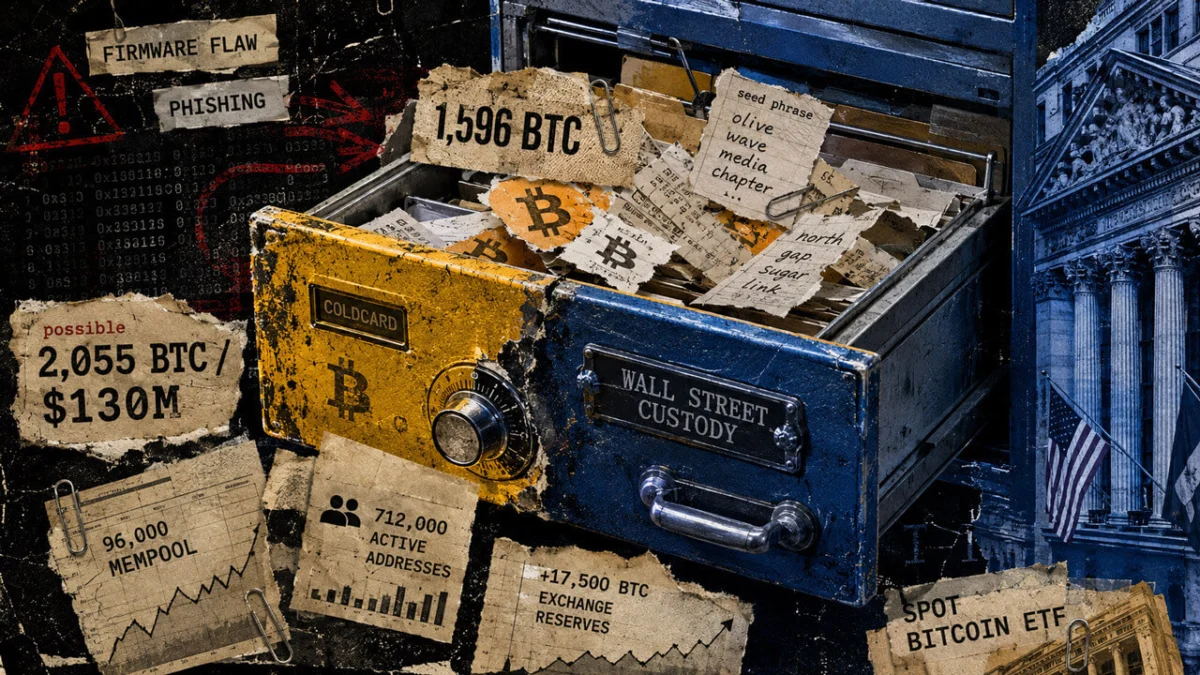
The cryptocurrency world is reeling from a significant security breach impacting Coldcard hardware wallets, resulting in the confirmed theft of at least 1,596 Bitcoin (BTC), valued at approximately $130 million. The exploit, stemming from a critical flaw in the device’s firmware, has prompted a widespread exodus of funds as an estimated 7,300 addresses are believed to be compromised. This event underscores the inherent risks of entrusting private key generation to a single point of failure, even within the typically secure realm of hardware wallets, and has sent ripples of activity across the Bitcoin network.
The Genesis of the Crisis: A Flawed Seed Generation Process
At the heart of this unfolding crisis lies a subtle yet devastating coding error within Coldcard firmware versions dating back to March 2021. Researchers at Galaxy Research, who have been meticulously tracking the exploit, identified that this flaw caused certain Coldcard devices to generate recovery seeds using an inferior software-based process. Instead of relying sufficiently on the hardware’s true random-number generator (TRNG), the compromised devices drew less randomness, leading to recovery seeds with a drastically reduced number of possible combinations.
This weakness proved to be a critical vulnerability. Attackers, leveraging this predictable randomness, were able to remotely reconstruct private keys without ever physically possessing the Coldcard device or obtaining the owner’s recovery words. This remote reconstruction bypasses the fundamental security principles of hardware wallets, which are designed to keep private keys offline and inaccessible.
Unraveling the Attack: Waves of Theft and Growing Victim Count
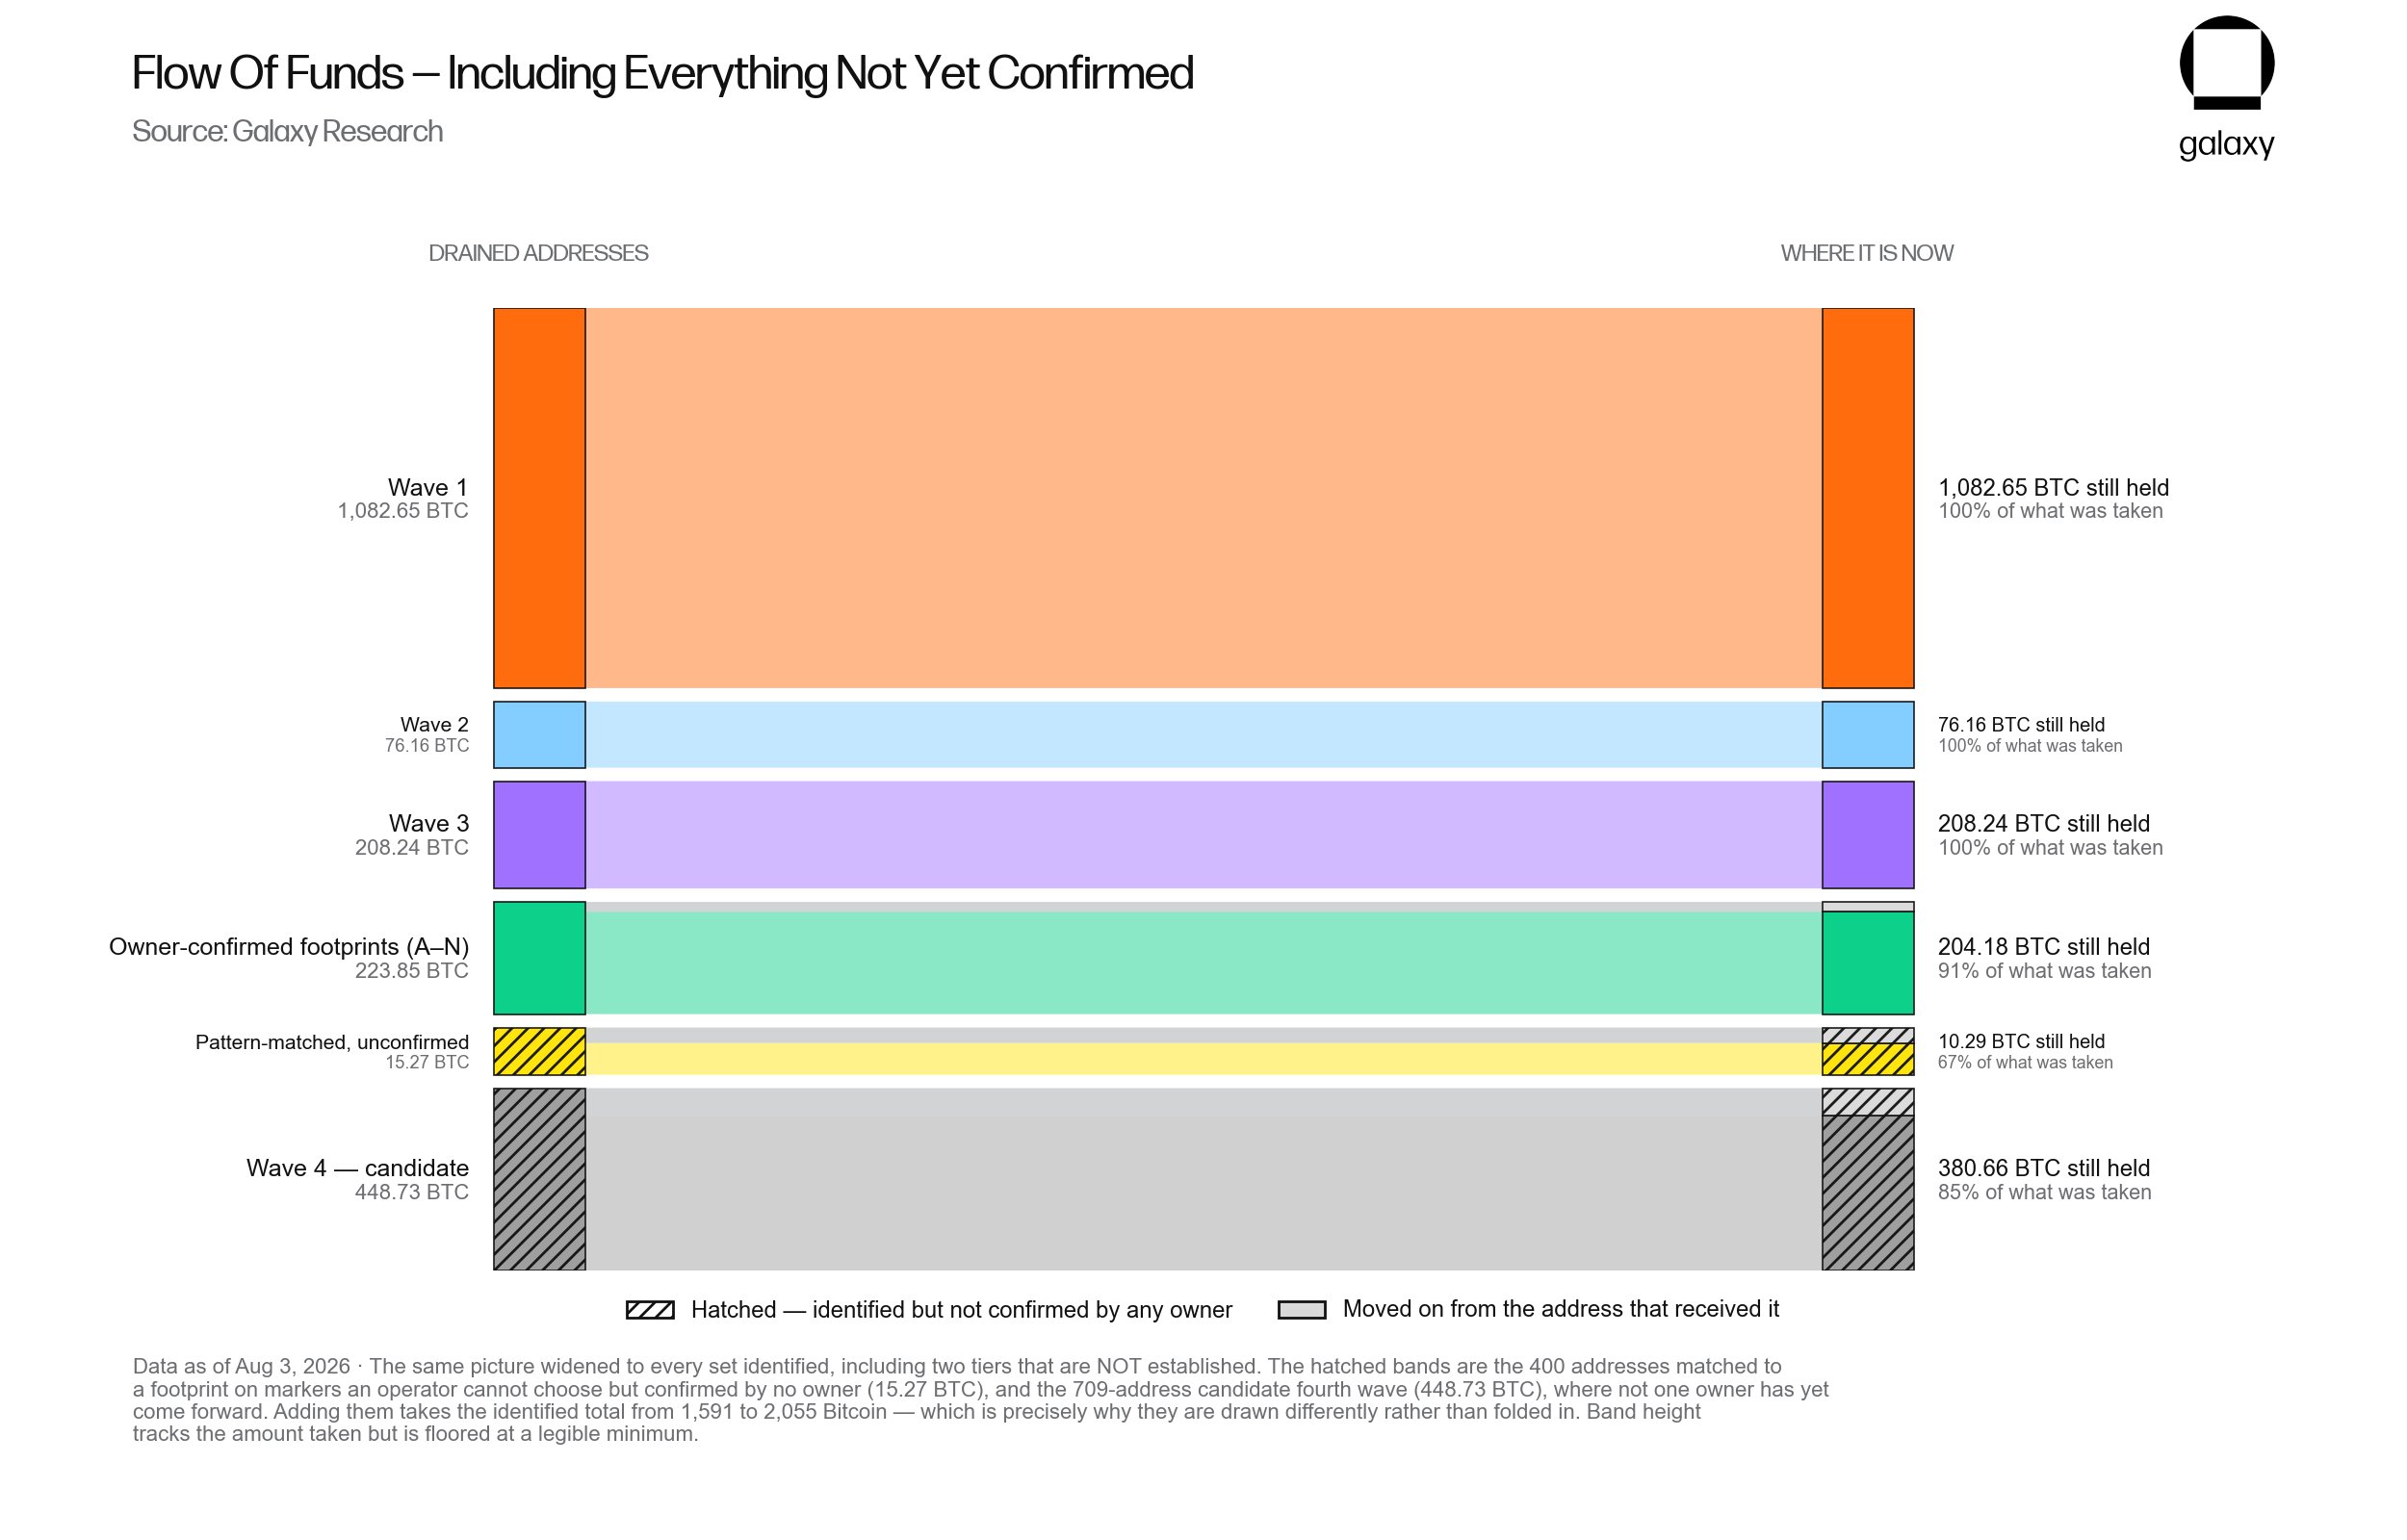
Galaxy Research has documented at least three major attack waves and 14 smaller, distinct incidents that have collectively led to the confirmed losses. The firm’s head of research, Alex Thorn, has been inundated with requests for assistance, with at least 73 victims reaching out to help trace their stolen Bitcoin. These victim reports have been instrumental in helping researchers identify additional attack patterns and estimate that as many as 15 individual attackers may now be exploiting this vulnerability.
While 1,596 BTC has been definitively confirmed as stolen, Galaxy Research has identified a potential fourth wave of attacks that could elevate the total loss to 2,055 BTC, pushing the estimated value closer to $130 million. However, these additional addresses remain outside the confirmed loss figure pending further victim confirmations and on-chain analysis.
A concerning aspect of the theft is the current status of the stolen funds. Approximately 90% of the pilfered Bitcoin has remained untouched since the initial attacks. Crucially, all coins linked to the first three confirmed waves are still held in the attacker-controlled addresses, suggesting a potential pause or careful planning by the perpetrators before attempting to liquidate their ill-gotten gains. Galaxy has proactively shared the identified addresses with U.S. law enforcement agencies, cryptocurrency exchanges, and blockchain investigation firms to flag any attempts to move these funds through centralized platforms.
The Immediate Aftermath: A Mass Exodus and Network Congestion
The revelation of the Coldcard exploit has triggered a frantic scramble among affected users to secure their digital assets. Coinkite, the manufacturer of Coldcard, has issued urgent directives, urging users to install the latest security update, generate a completely new recovery seed, and transfer their Bitcoin to wallets secured by these new, uncompromised phrases.
This urgent migration has had a profound and visible impact on the Bitcoin network. On-chain analytics firms, including Santiment and CryptoQuant, have reported a significant surge in network activity, reaching levels not seen since earlier periods of market volatility.
Key On-Chain Indicators Spiked:
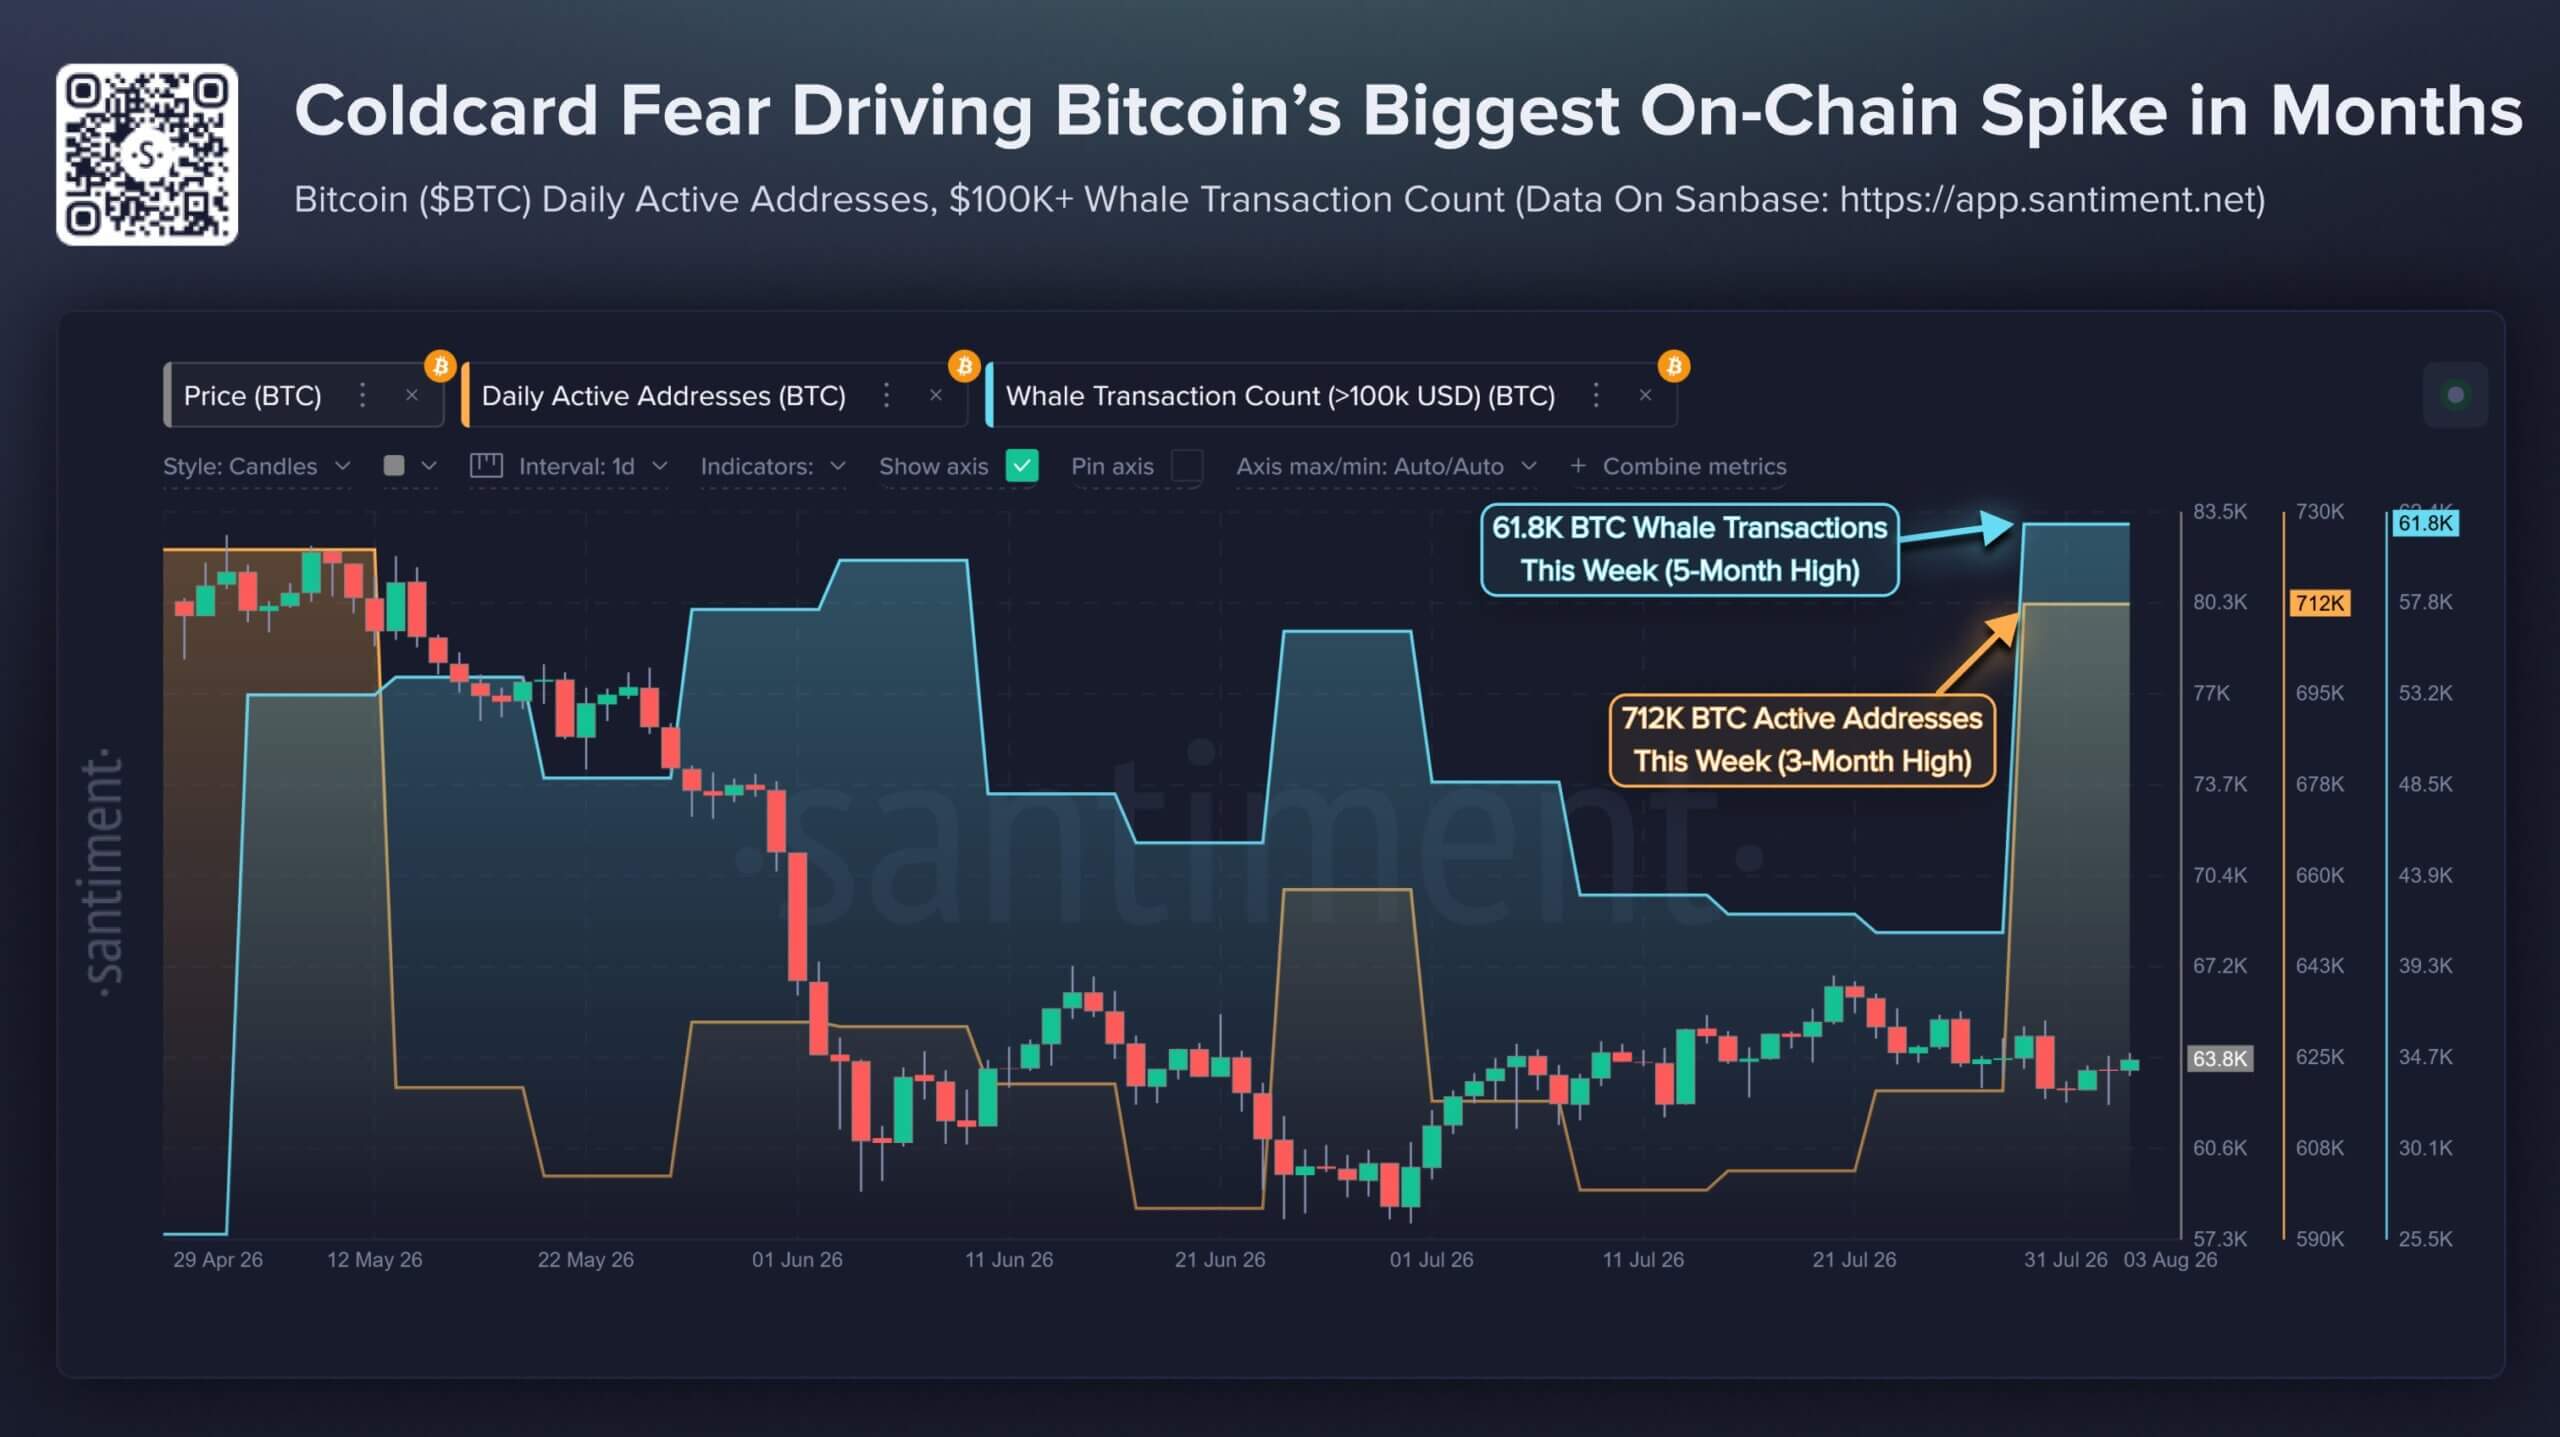
- Active Addresses: Santiment data revealed a seven-day average of 712,000 active Bitcoin addresses, marking a three-month high.
- Large Transactions: Transactions exceeding $100,000 surged to 61,800 in the past seven days, the highest figure in five months.
- Smaller Transactions: CryptoQuant noted that transactions valued below $100,000 reached $3.2 billion in the past week, a level not observed since November 2024.
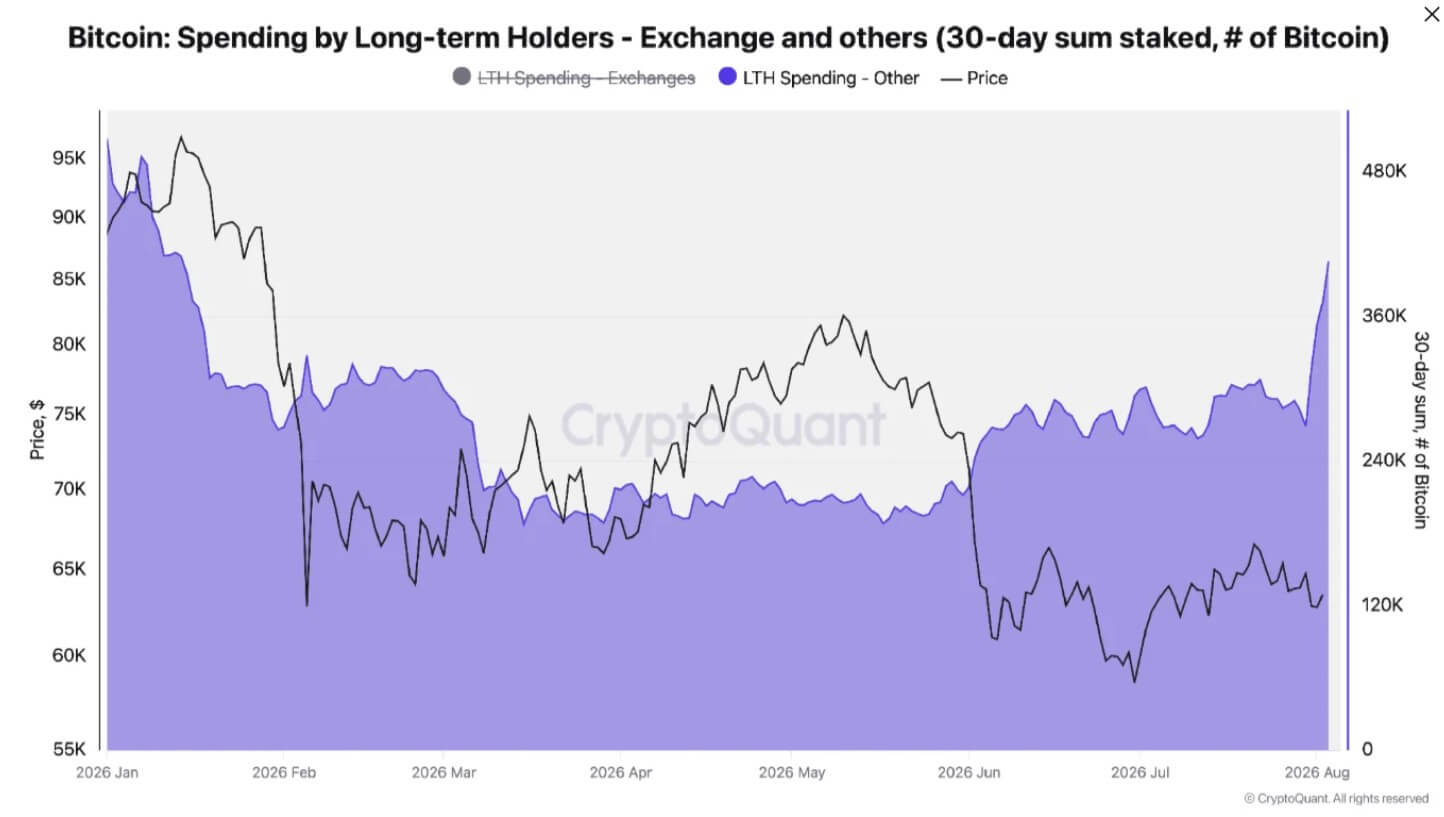
- Long-Term Holder Activity: Spending by long-term holders outside of exchanges saw a dramatic increase. As of August 3rd, 406,000 BTC was spent by this cohort on a 30-day basis, a significant jump from 269,000 BTC prior to the exploit and the highest since January.
It is important to note that this heightened spending by long-term holders does not necessarily equate to selling pressure. The act of moving Bitcoin from a vulnerable Coldcard address to a newly generated, secure wallet is recorded on the blockchain as a "spent" transaction, even if the ultimate ownership of the funds remains unchanged.
The sheer volume of users attempting to migrate their funds simultaneously led to significant network congestion. Transaction fees reportedly spiked, and the Bitcoin mempool – the holding area for unconfirmed transactions – swelled from approximately 33,000 to around 96,000 pending transactions, the highest level since June 20th. This congestion underscored the urgency felt by users and the technical challenges of executing secure migrations under duress.
Rise of Exchange Inflows and Heightened Phishing Threats
As users navigate the complex process of migrating their funds, a portion of the Bitcoin has found its way to centralized exchanges. CryptoQuant data indicates that deposits from smaller holders to exchanges reached their highest point since February 6th. This suggests that some users, uncertain about their next steps or seeking immediate refuge for their assets, have temporarily moved their Bitcoin into existing custodial accounts.
The total reserves across exchanges saw an increase of approximately 17,500 BTC between July 28th and August 3rd, rising from around 2.702 million BTC to 2.719 million BTC. Binance, in particular, absorbed a significant portion of this influx, accounting for about 51% of the net increase, with its reserves climbing by approximately 9,000 BTC to 659,000 BTC.
However, these exchange inflows do not definitively signal a shift towards long-term custodial holding. They may represent temporary holding patterns while users establish new, secure self-custody solutions or weigh their options for hardware wallet replacements.
Compounding the challenge for affected users is the emergence of sophisticated phishing attacks. The disclosure of the Coldcard vulnerability has created a fertile ground for scammers posing as wallet support teams or offering fraudulent migration instructions. Rival hardware wallet manufacturer Trezor issued a public warning, highlighting an increase in phishing attempts targeting users attempting to migrate their funds. Trezor emphatically reminded its users never to share their recovery seeds or enter them into unsolicited websites or applications, stressing that recovery words should only be entered directly on a Trezor device during a legitimate wallet restoration process. They also advised users to disregard any migration instructions received via email, messages, or phone calls, and confirmed their own devices were not affected by the Coldcard incident.
The complexity of securely migrating funds from a compromised seed presents a significant hurdle. Importing a known weak seed into another device does not rectify the underlying vulnerability. Users must generate an entirely new recovery phrase and meticulously transfer their Bitcoin to an address derived from this secure phrase. This process is more intricate than a simple firmware update or a standard wallet restoration, making users susceptible to scams that might direct them to fraudulent applications, request recovery words under the guise of a security check, or provide a malicious address for fund transfers.
The ETF Debate Reignited: Self-Custody vs. Regulated Products
The Coldcard crisis has injected new momentum into the ongoing debate surrounding Bitcoin custody, specifically highlighting the perceived advantages of regulated investment products like spot Bitcoin Exchange-Traded Funds (ETFs). Eric Balchunas, a Senior ETF Analyst at Bloomberg Intelligence, suggested that the Coldcard breach could prompt some investors, including long-term holders, to consider migrating towards ETFs.
Historically, Bitcoin advocates have expressed reservations about ETFs, arguing that investors in these products do not directly control the underlying Bitcoin or their private keys. Instead, institutional custodians hold these assets on behalf of the ETF. However, in the wake of the Coldcard exploit, this model of institutional custody, managed by large financial institutions with extensive experience in asset safeguarding, may appear more appealing when contrasted with relying on a smaller hardware wallet manufacturer.
While institutional custody does not eliminate the risk of theft or operational failure, Balchunas noted that a successful attack on an ETF custodian would likely trigger immediate regulatory scrutiny and a coordinated response involving the fund manager, custodian, and law enforcement. This contrasts with the more fragmented response typically seen in individual hardware wallet breaches.
It is crucial to emphasize that there is currently no direct evidence linking the Coldcard exploit to users purchasing spot Bitcoin ETFs as a consequence. Furthermore, the observed increase in exchange deposits may prove to be a temporary phenomenon as users re-establish secure self-custody solutions.
Nevertheless, the Coldcard breach has undeniably altered the risk-reward calculus for investors contemplating where to store their Bitcoin. While self-custody offers independence from financial intermediaries, it places the onus of securing hardware and software—the very mechanisms that generate private keys—squarely on the individual. For those currently navigating the precarious task of migrating away from compromised seeds while simultaneously evading malicious actors, the perceived security and robust infrastructure of regulated institutional custody, once criticized for placing Bitcoin in the hands of Wall Street, might now present a simpler, albeit different, path to safeguarding their assets. The incident serves as a stark reminder that in the world of digital assets, security is a multi-layered endeavor, and even the most trusted tools are not immune to vulnerabilities.